In an ideal world, every analyst in your security operations center would always be able to investigate and respond to an investigation efficiently and effectively. In the real world, of course, that is not the case.
Most SOCs have seasoned analysts, junior analysts and everything in between. This variety of skill sets means that investigation and response to any given case can be dramatically different depending on the analyst working the case.
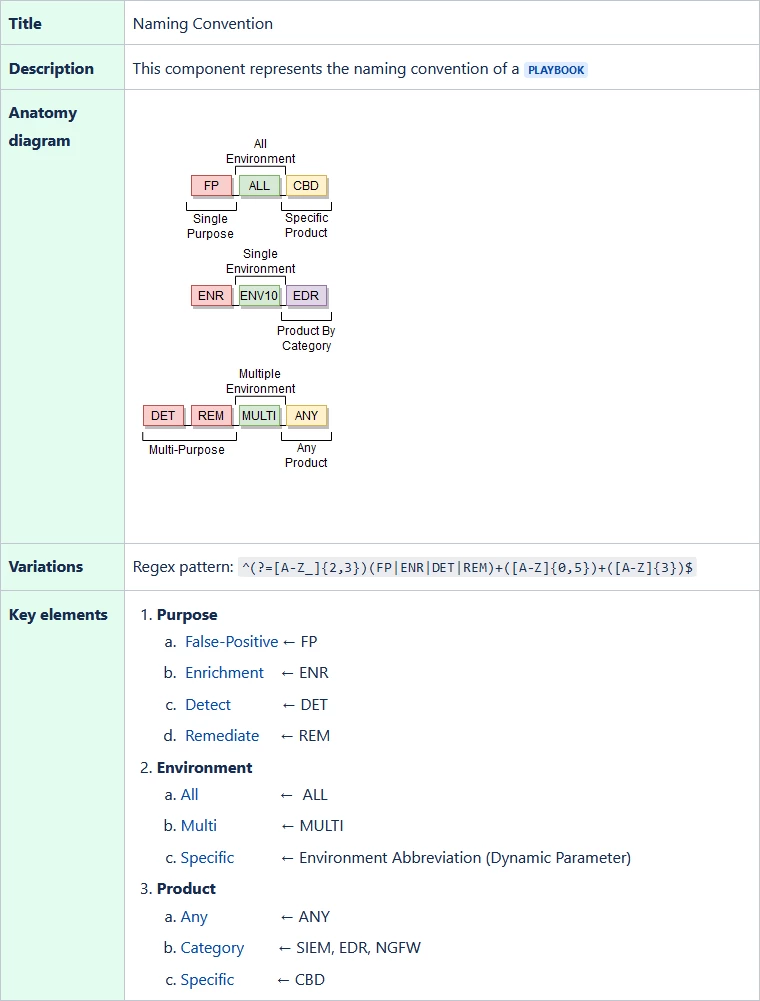
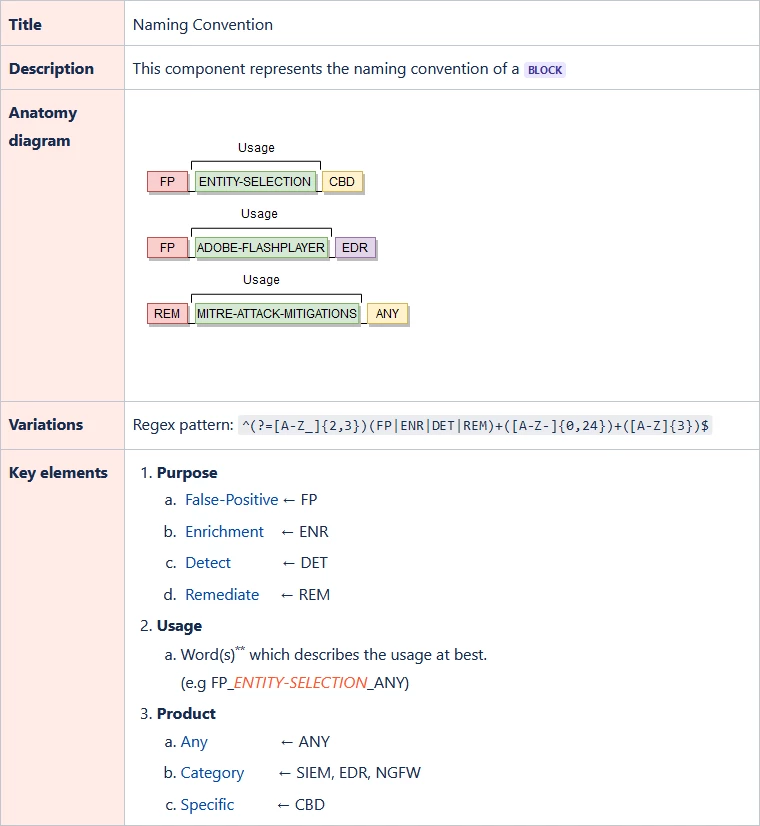
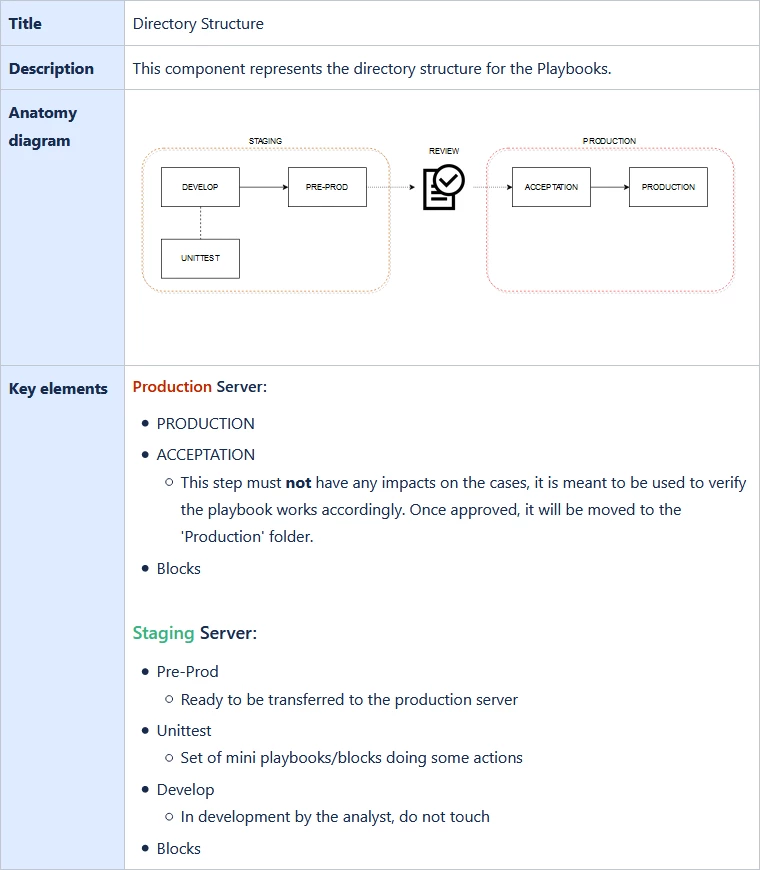
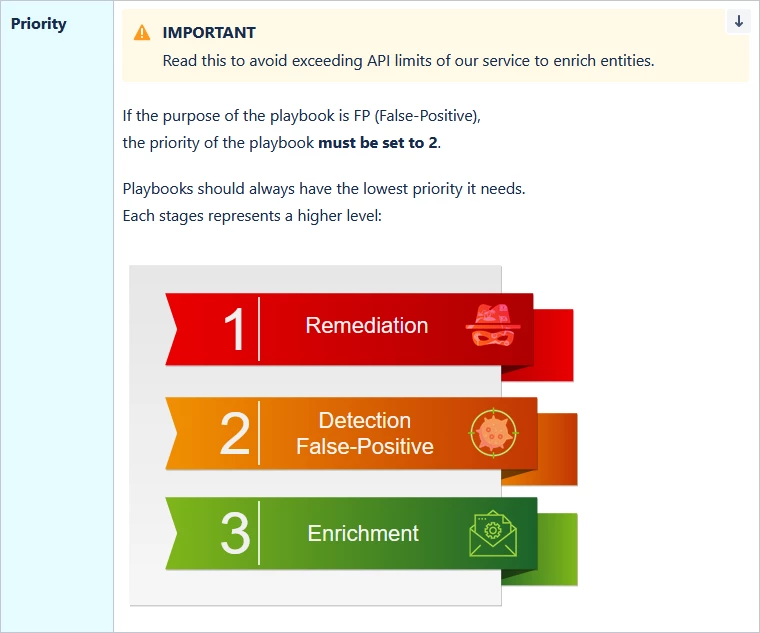
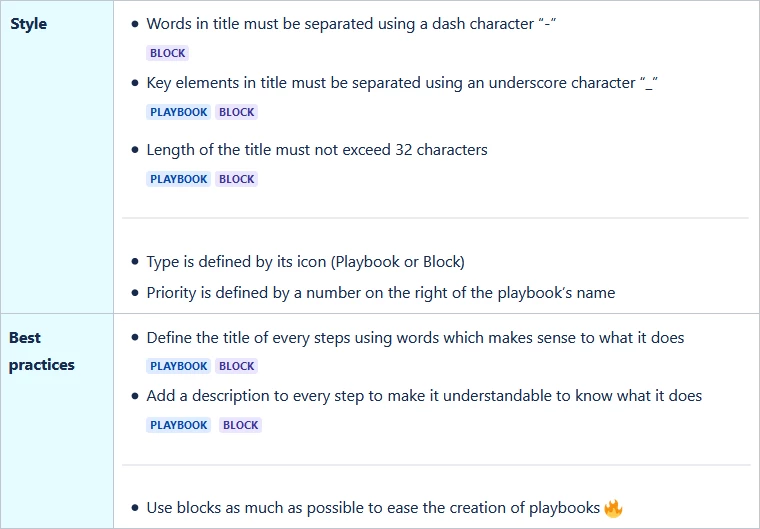
Thankfully, playbooks lay out consistent and repeatable processes for a given investigation type, no matter the analyst working the case.
We see everyday how teams of different sizes expand their playbooks knowledgebase with more use cases which creates a library that keeps growing over time.
Let’s hear some ideas on how to maintain an organized and flexible set of playbooks! What's working for you?
Share your thoughts below.