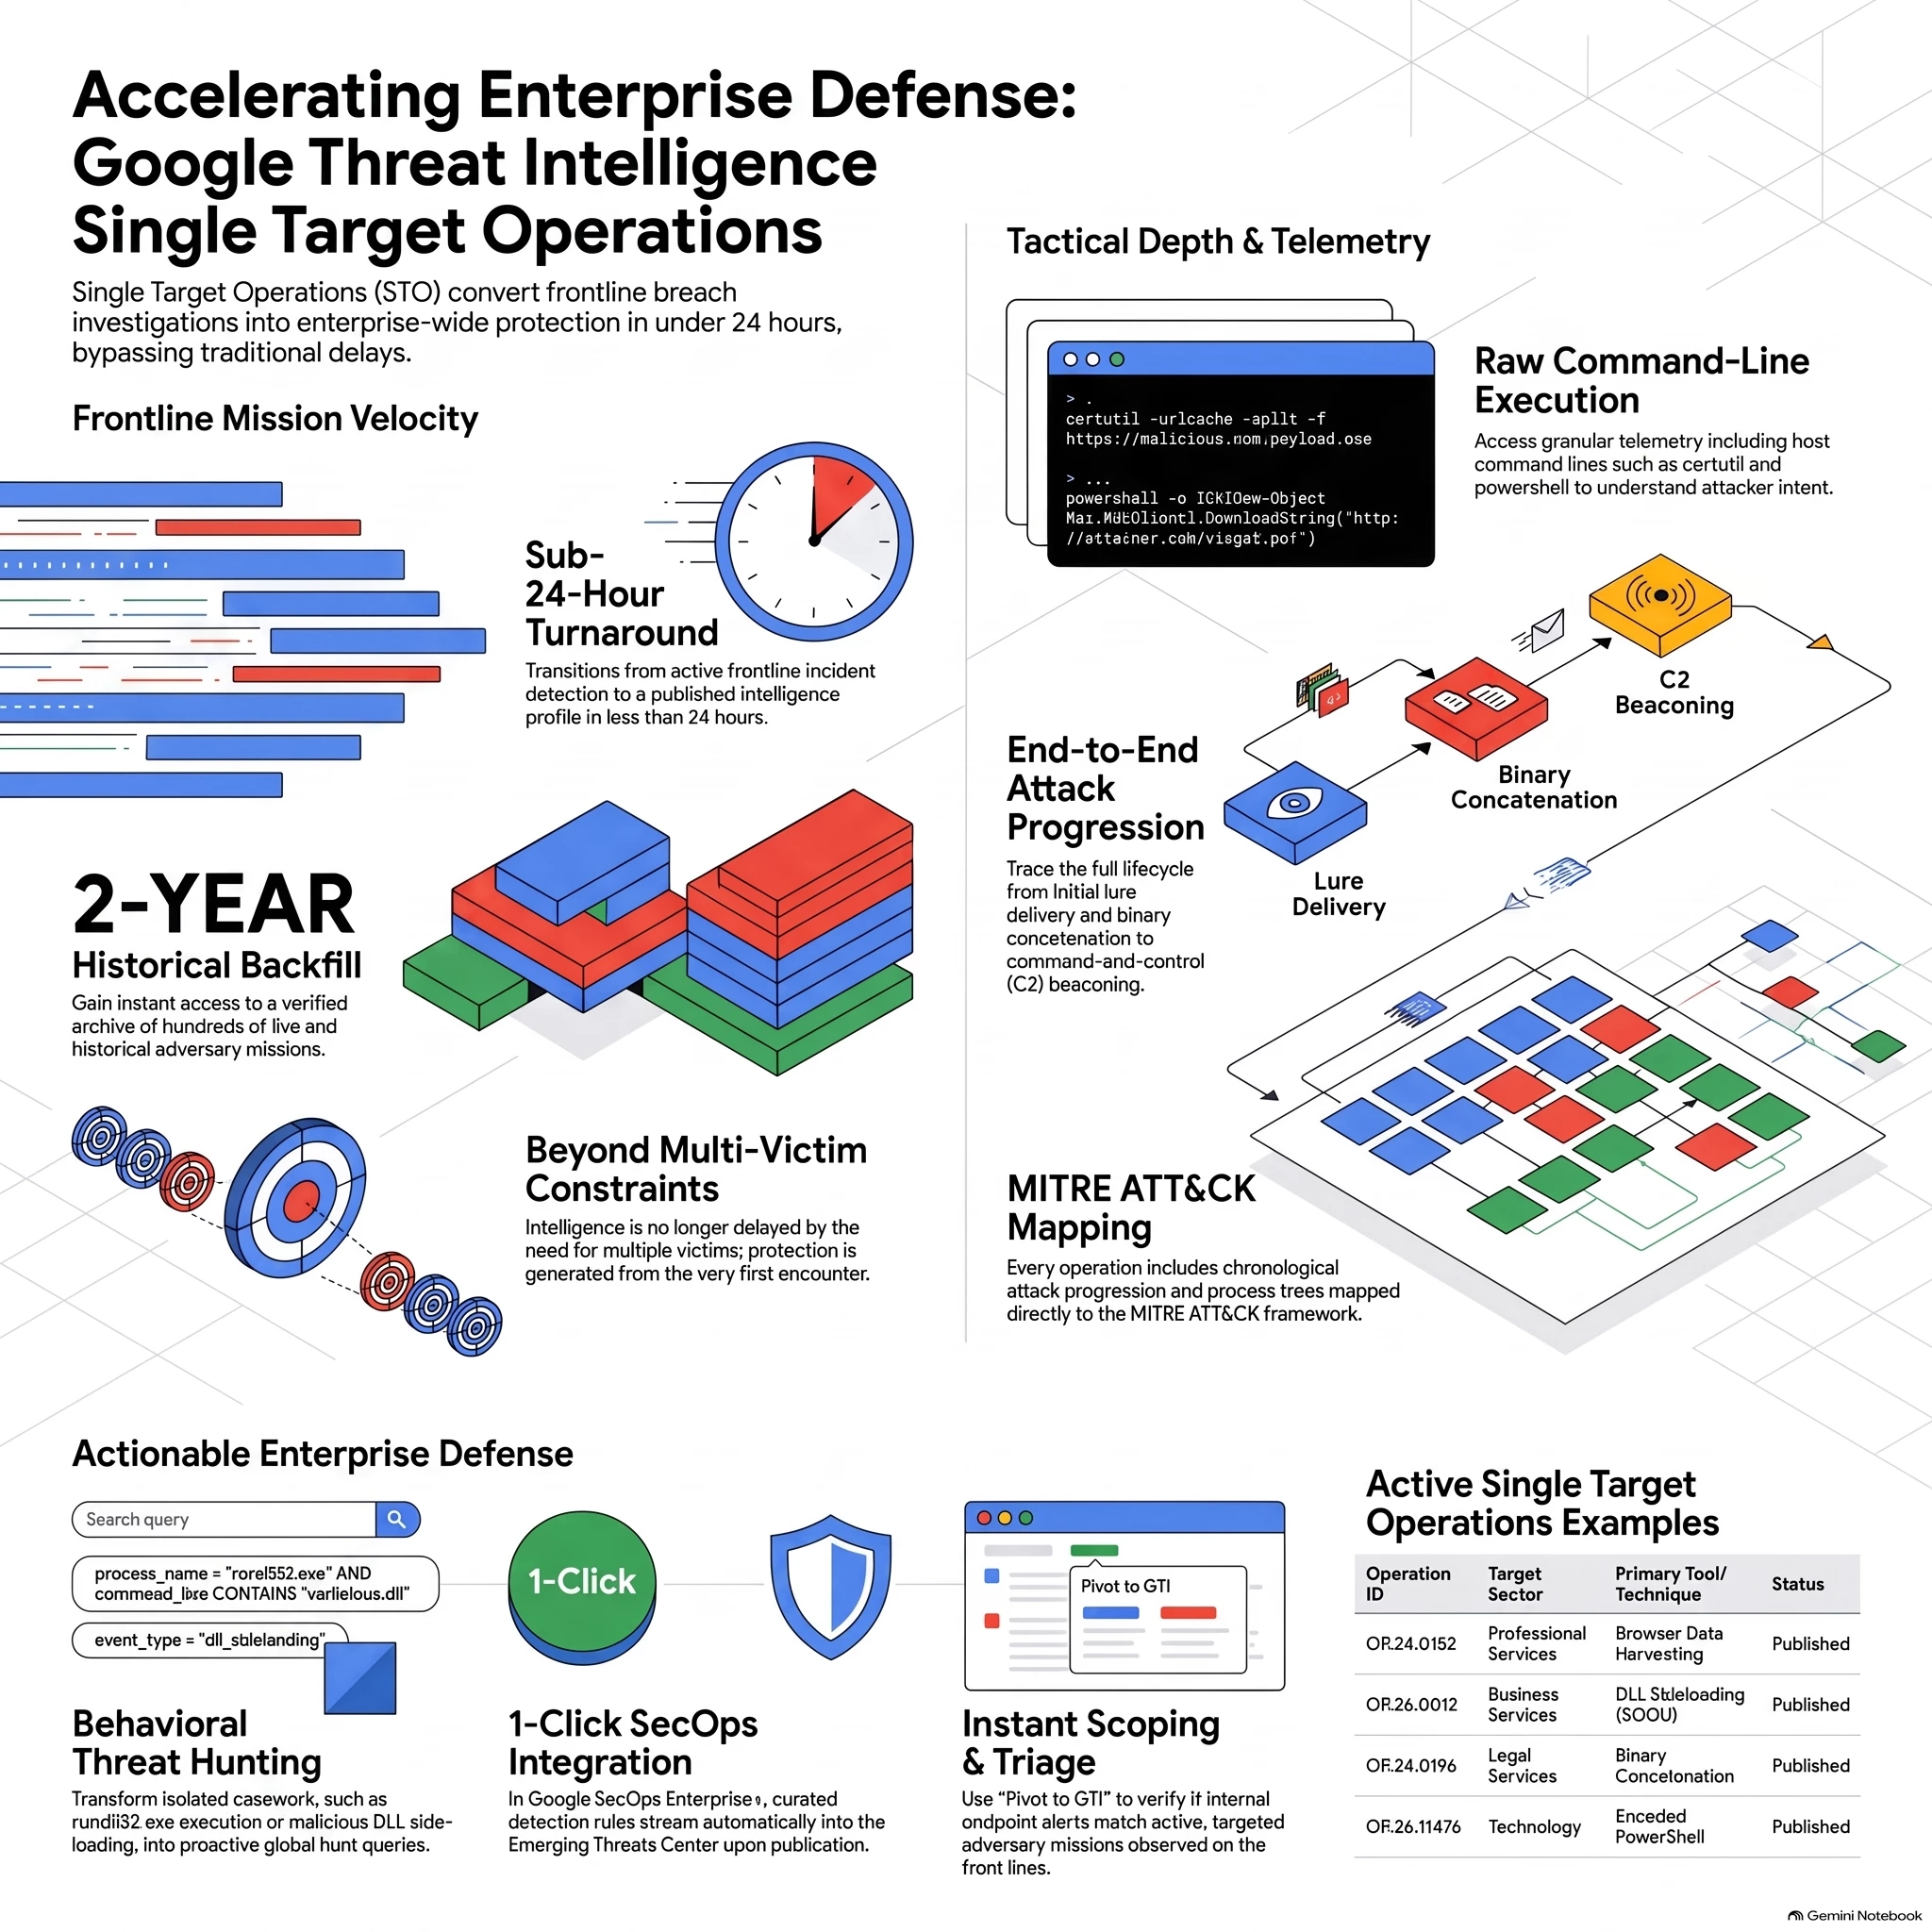

In modern cybersecurity, speed and precision are paramount. Traditional threat intelligence often waits until an adversary strikes multiple organizations before establishing a formal campaign profile. Google Threat Intelligence introduces Single Target Operations, an innovative capability that moves beyond multi-victim constraints to convert active frontline breach investigations into enterprise-wide protection in under twenty four hours.
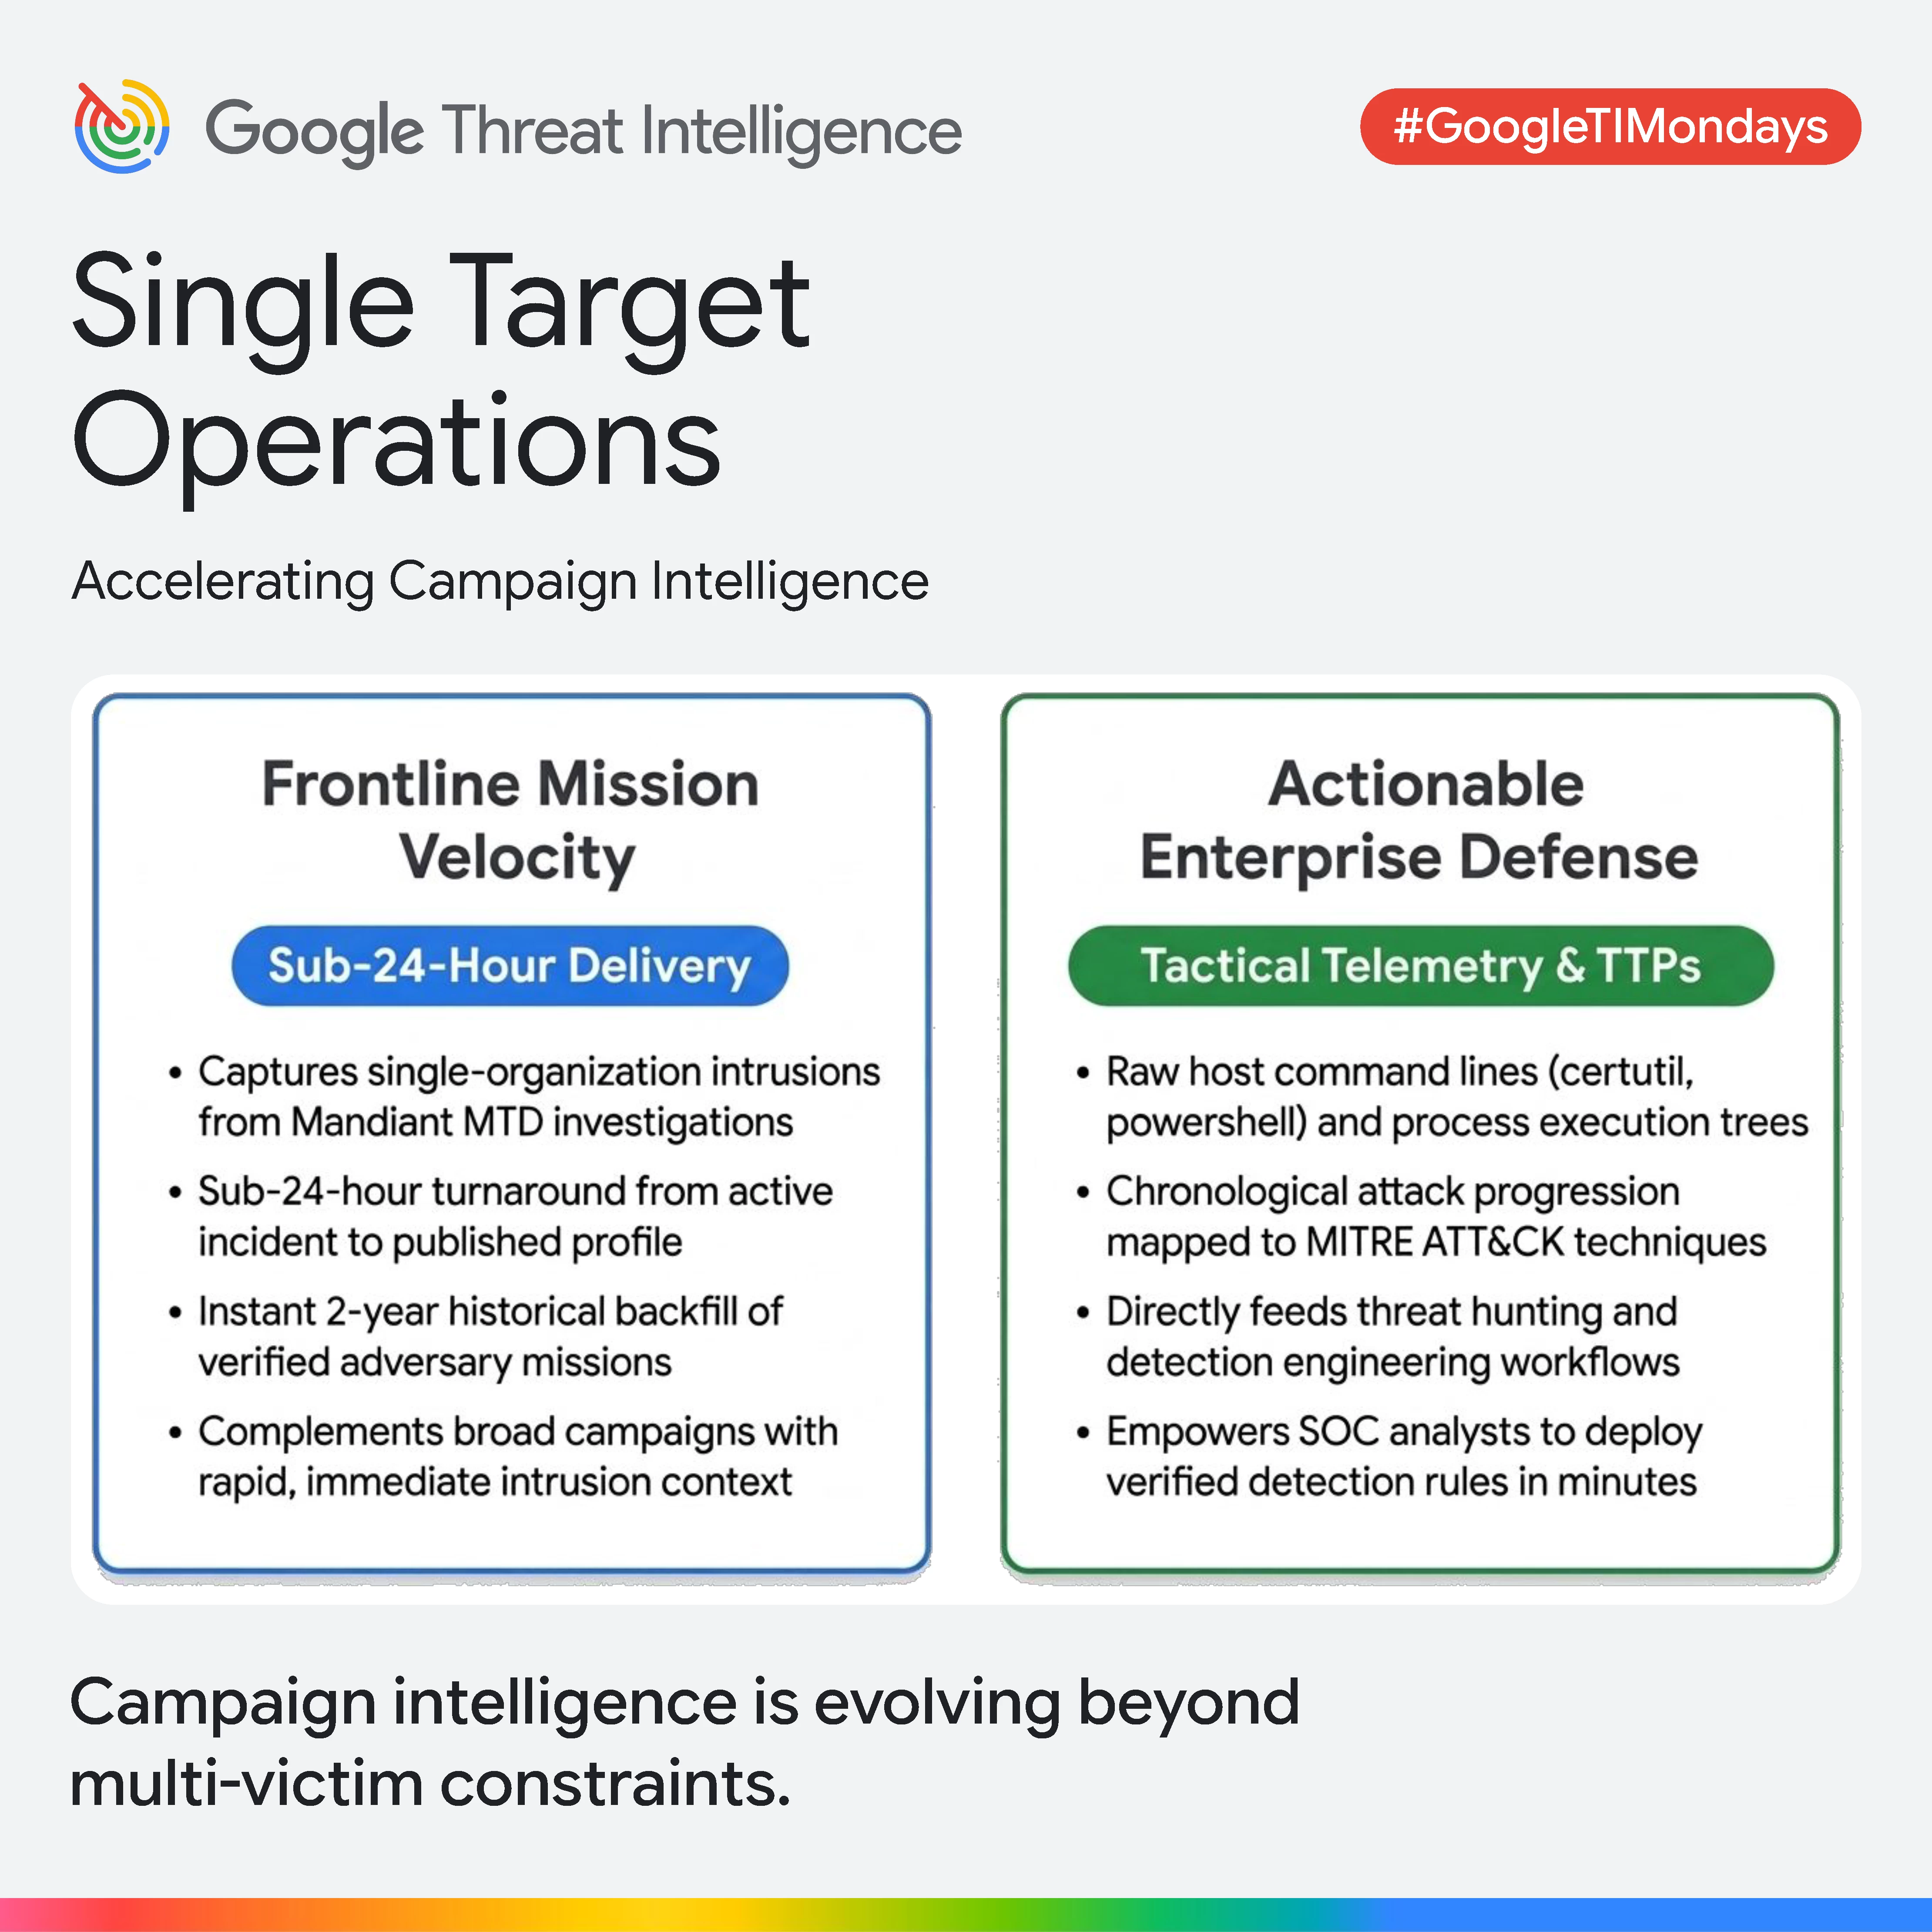
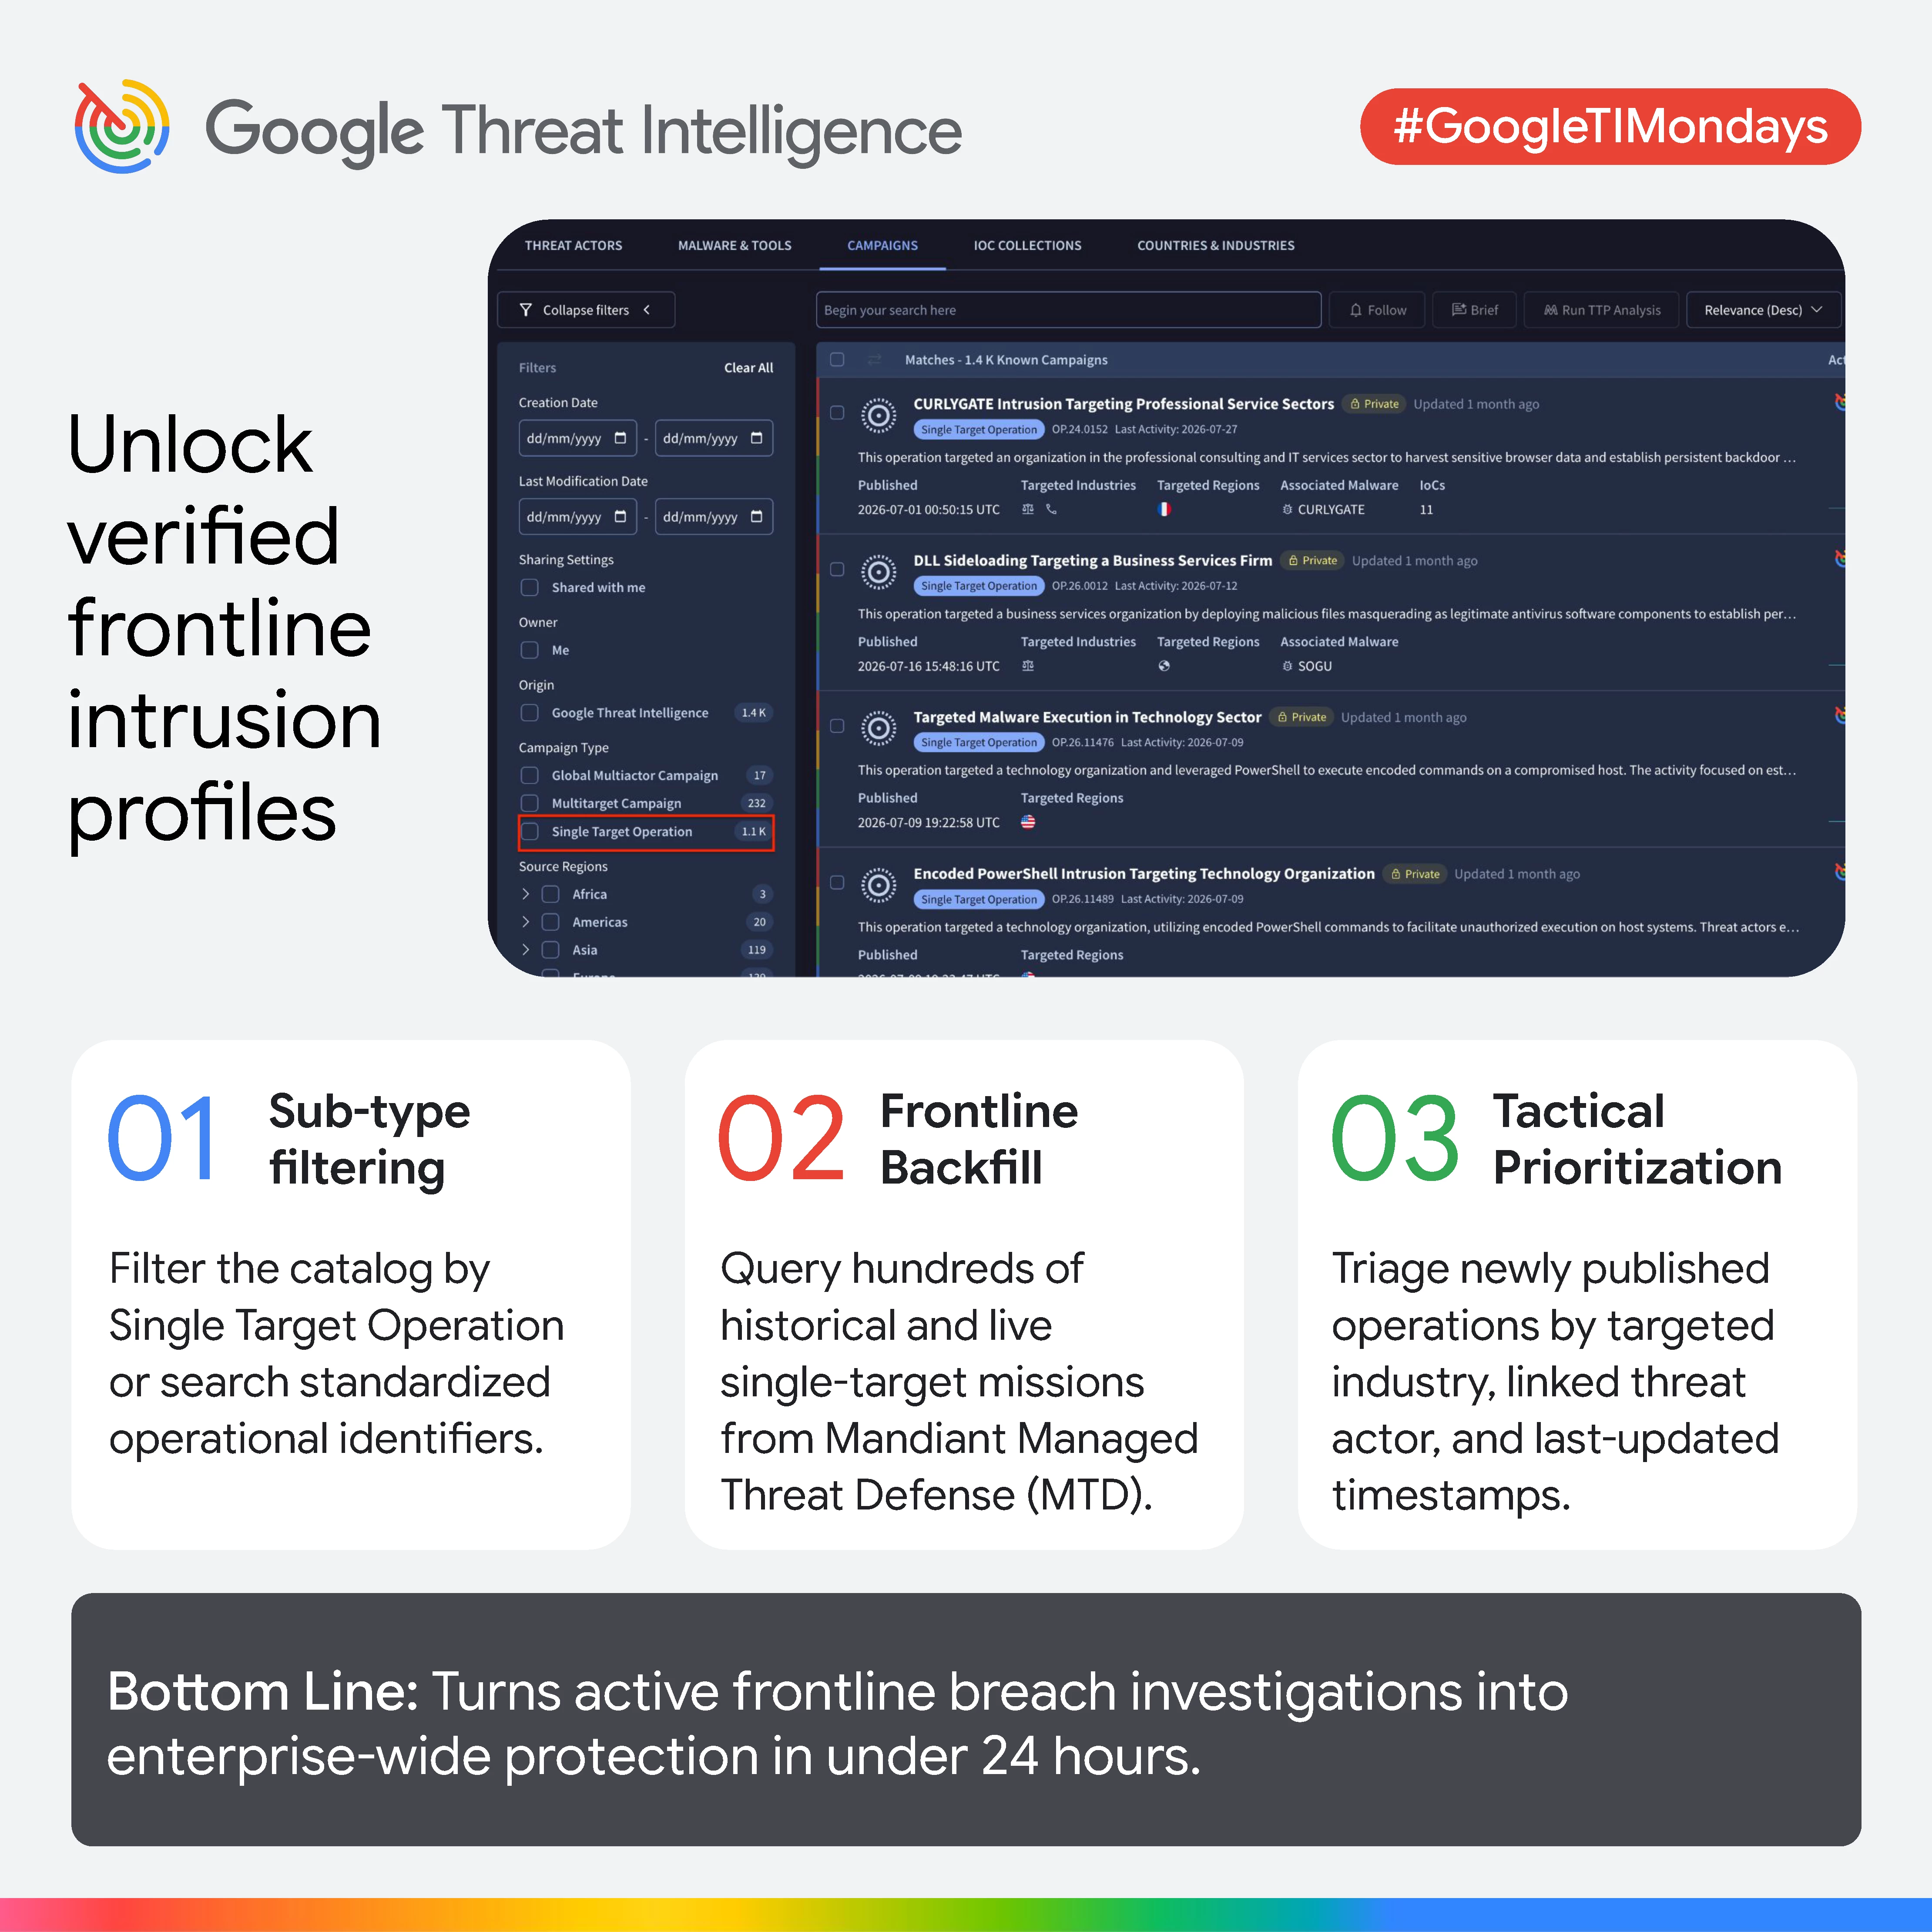
Powered by Mandiant Managed Threat Defense, Single Target Operations capture realtime, single organization intrusions with remarkable velocity. Rather than waiting days or weeks for comprehensive post-incident analysis, security operations centers gain sub twenty four hour delivery from an active frontline incident to a fully published intelligence profile. This capability also includes an instant two-year historical backfill of verified adversary missions, allowing security teams to query hundreds of live and historical investigations.
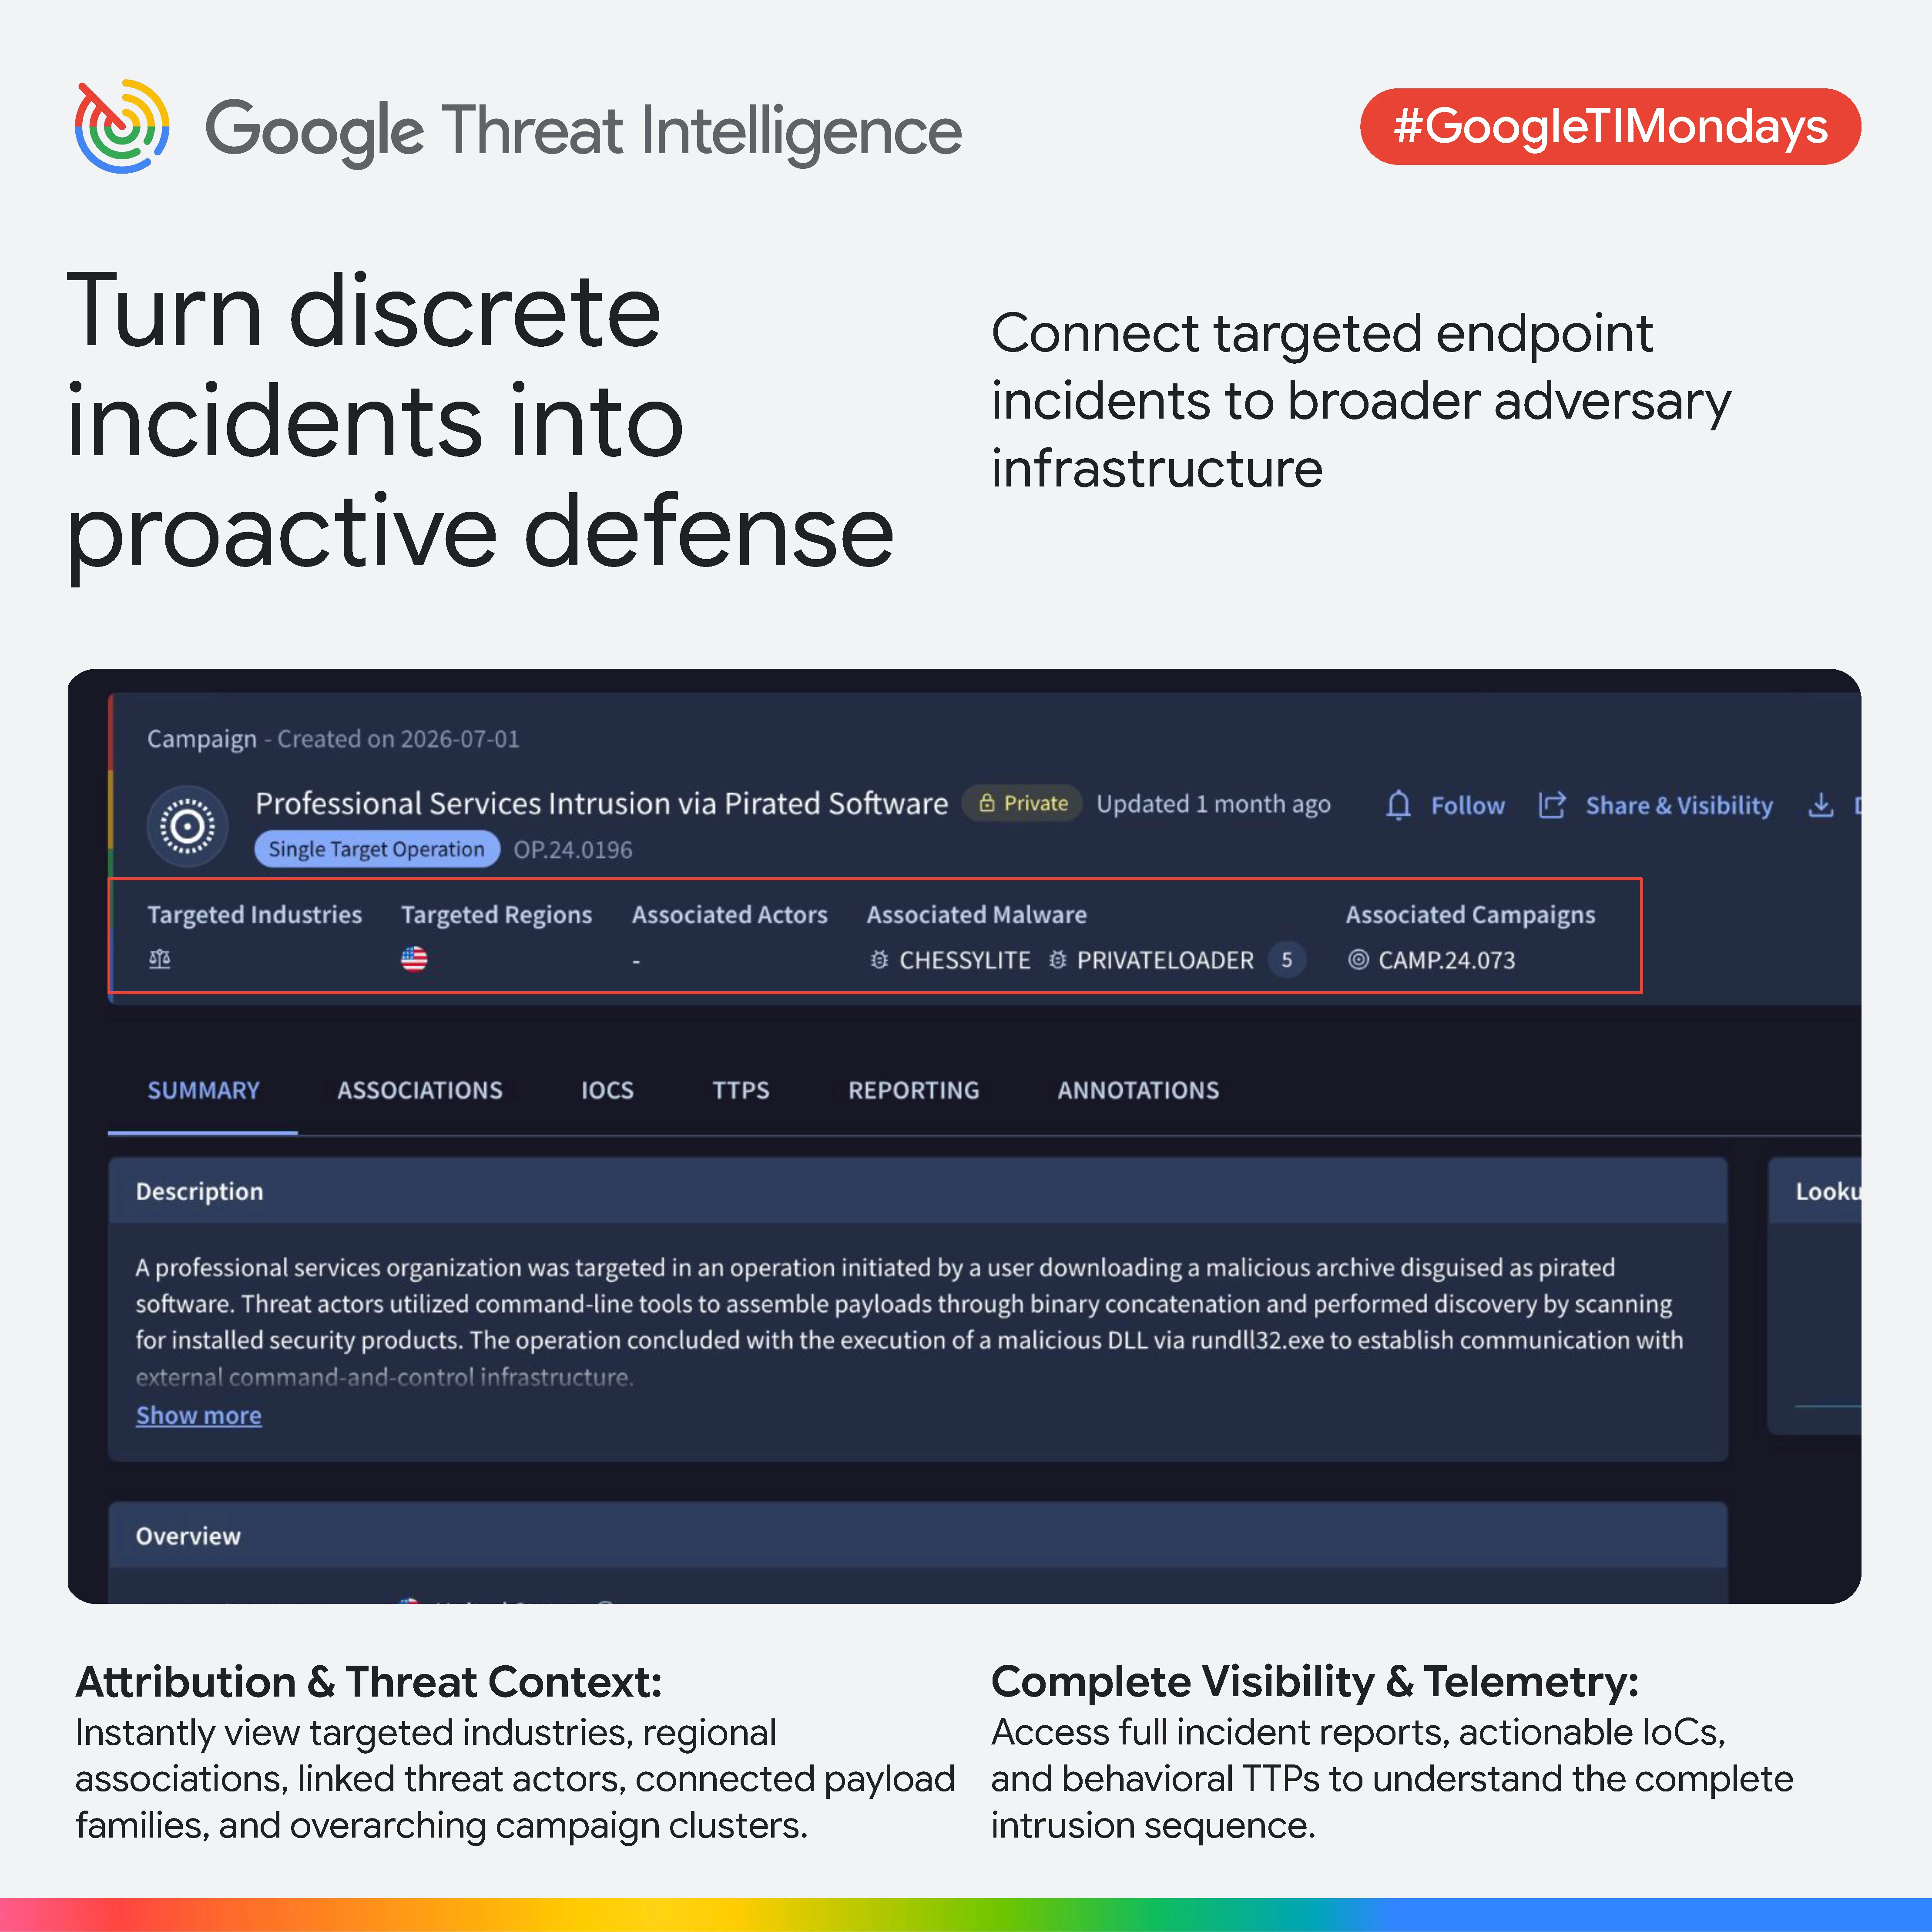
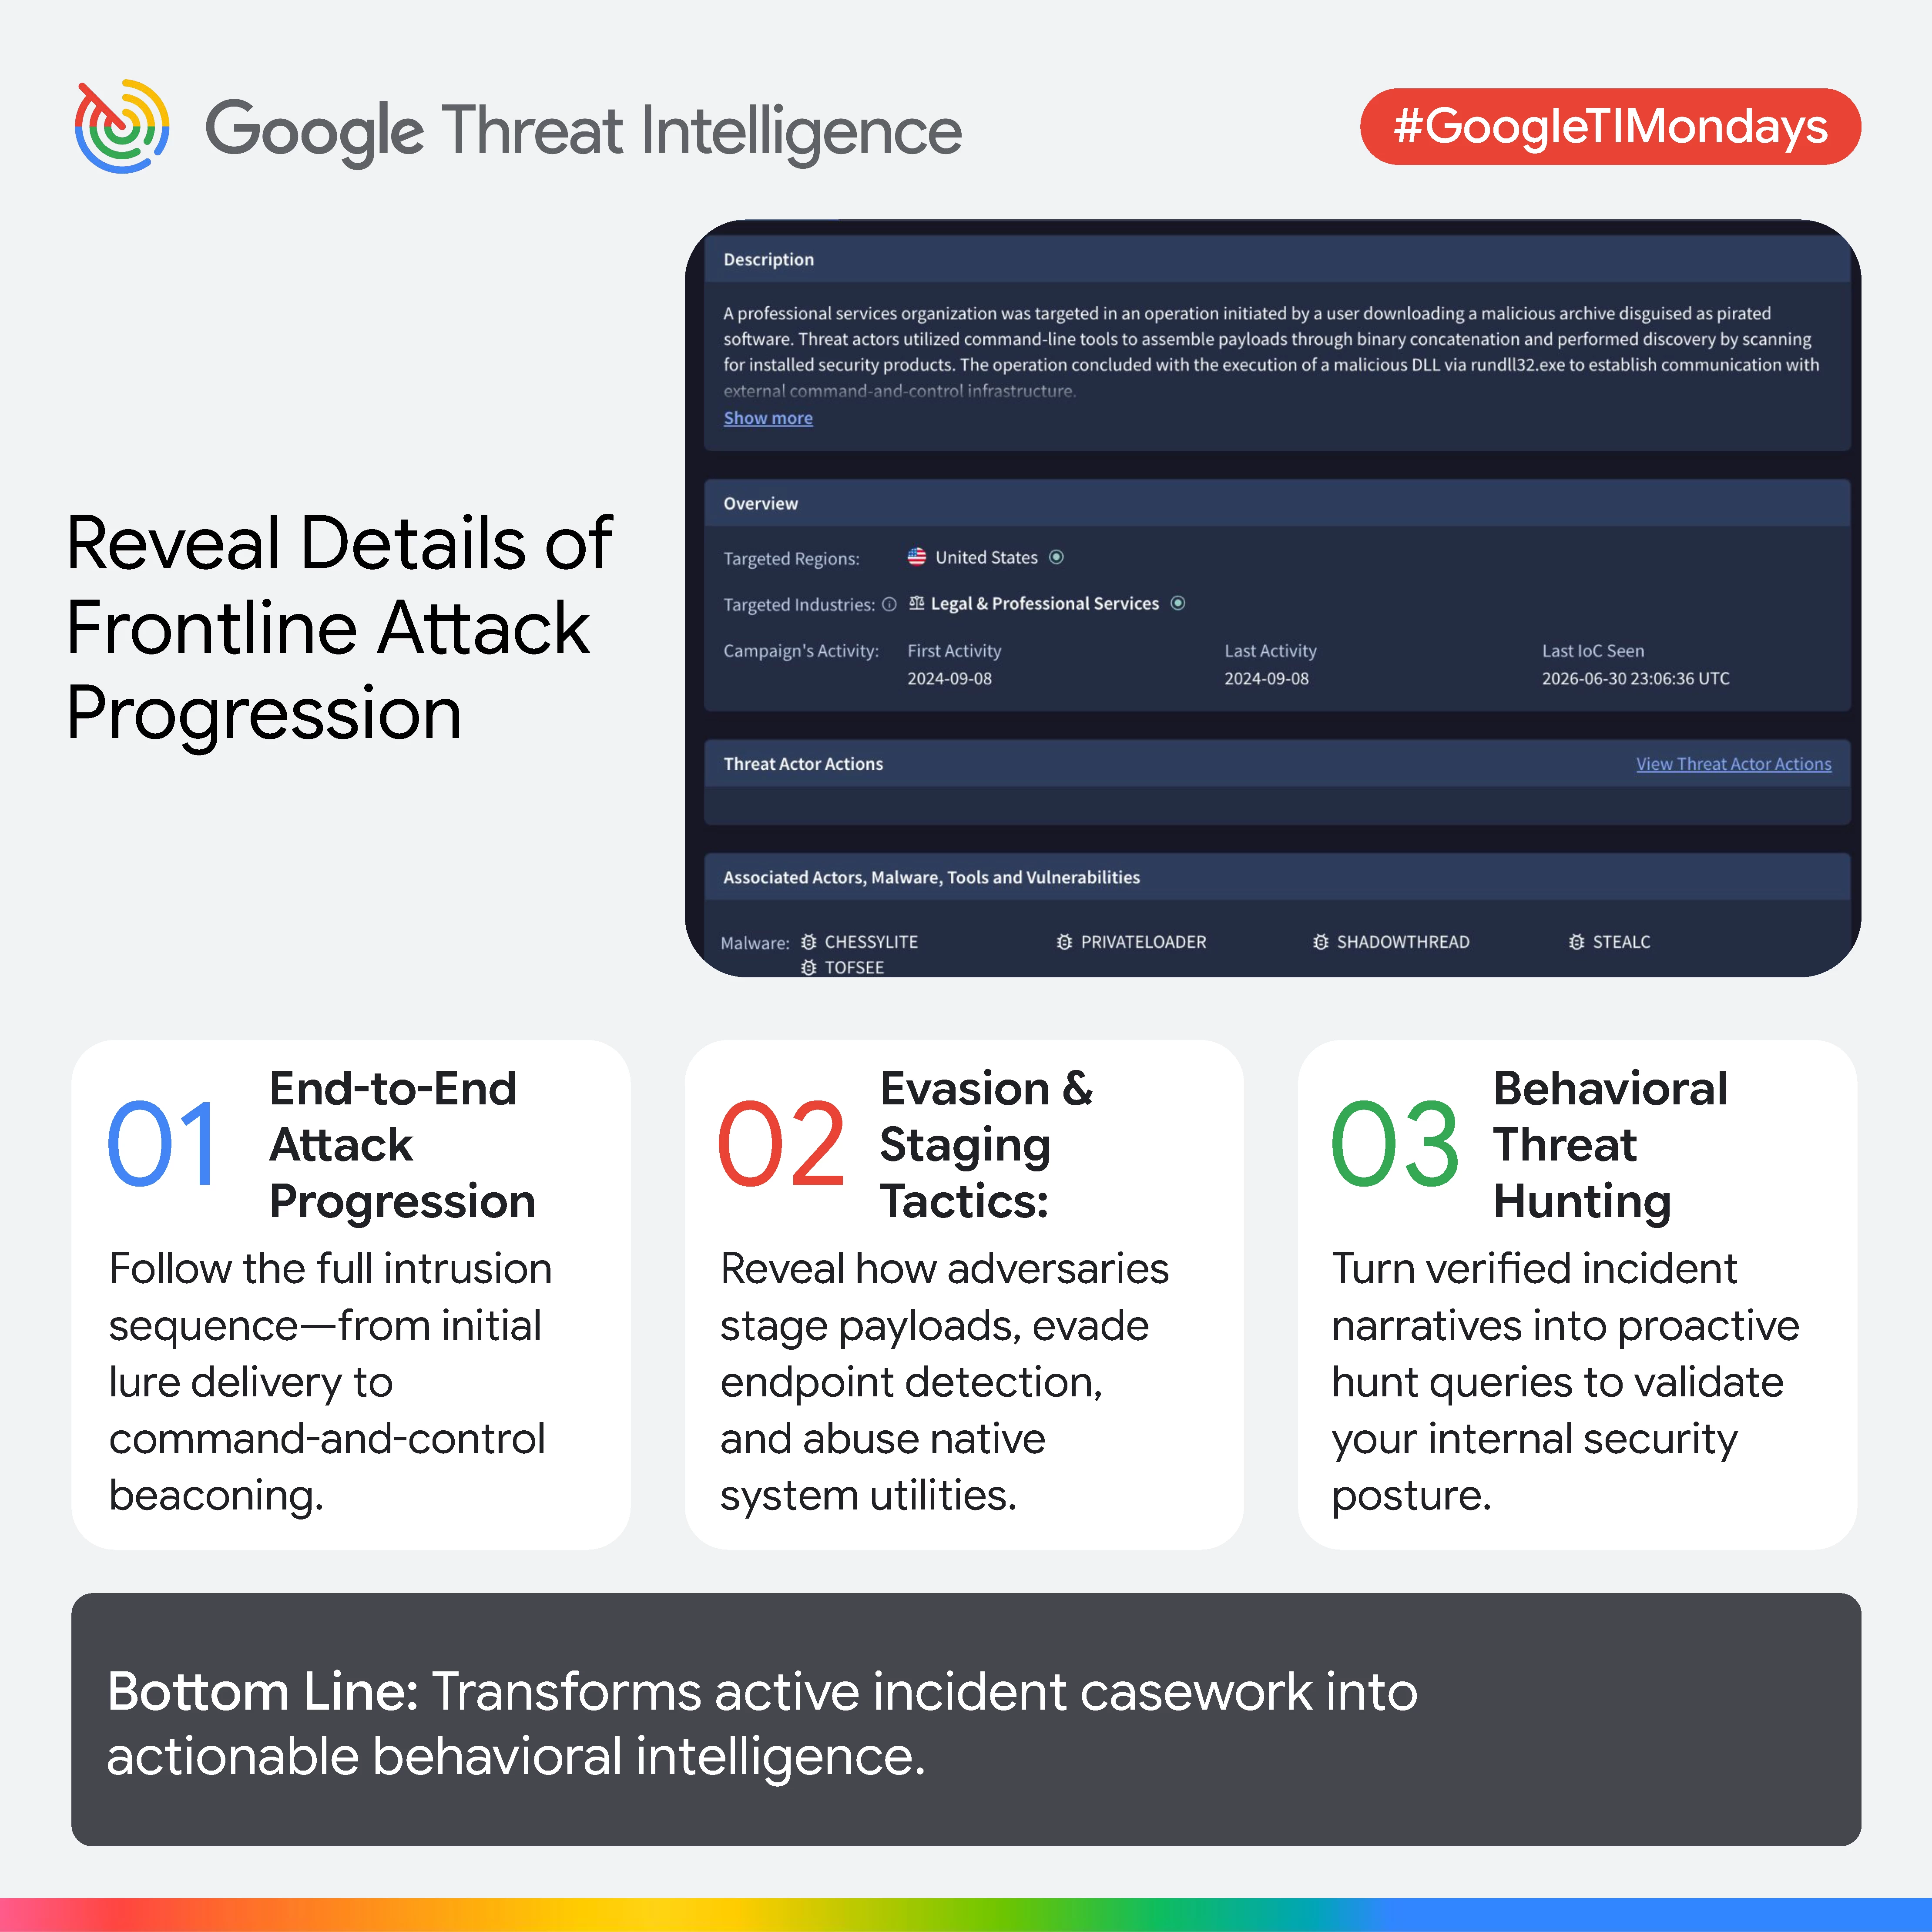
What makes this feature truly impactful is its tactical depth. Defenders receive end to end attack progression, granular telemetry, raw command-line executions, and process trees mapped directly to MITRE ATT&CK techniques. Security analysts can easily trace the full lifecycle of an intrusion, from initial lure delivery and payload staging to evasive living off the land techniques and command and control (C2) beaconing. By linking discrete endpoint incidents to broader adversary infrastructure, targeted industries, and associated malware families, teams can transform isolated casework into proactive behavioral threat hunting queries.
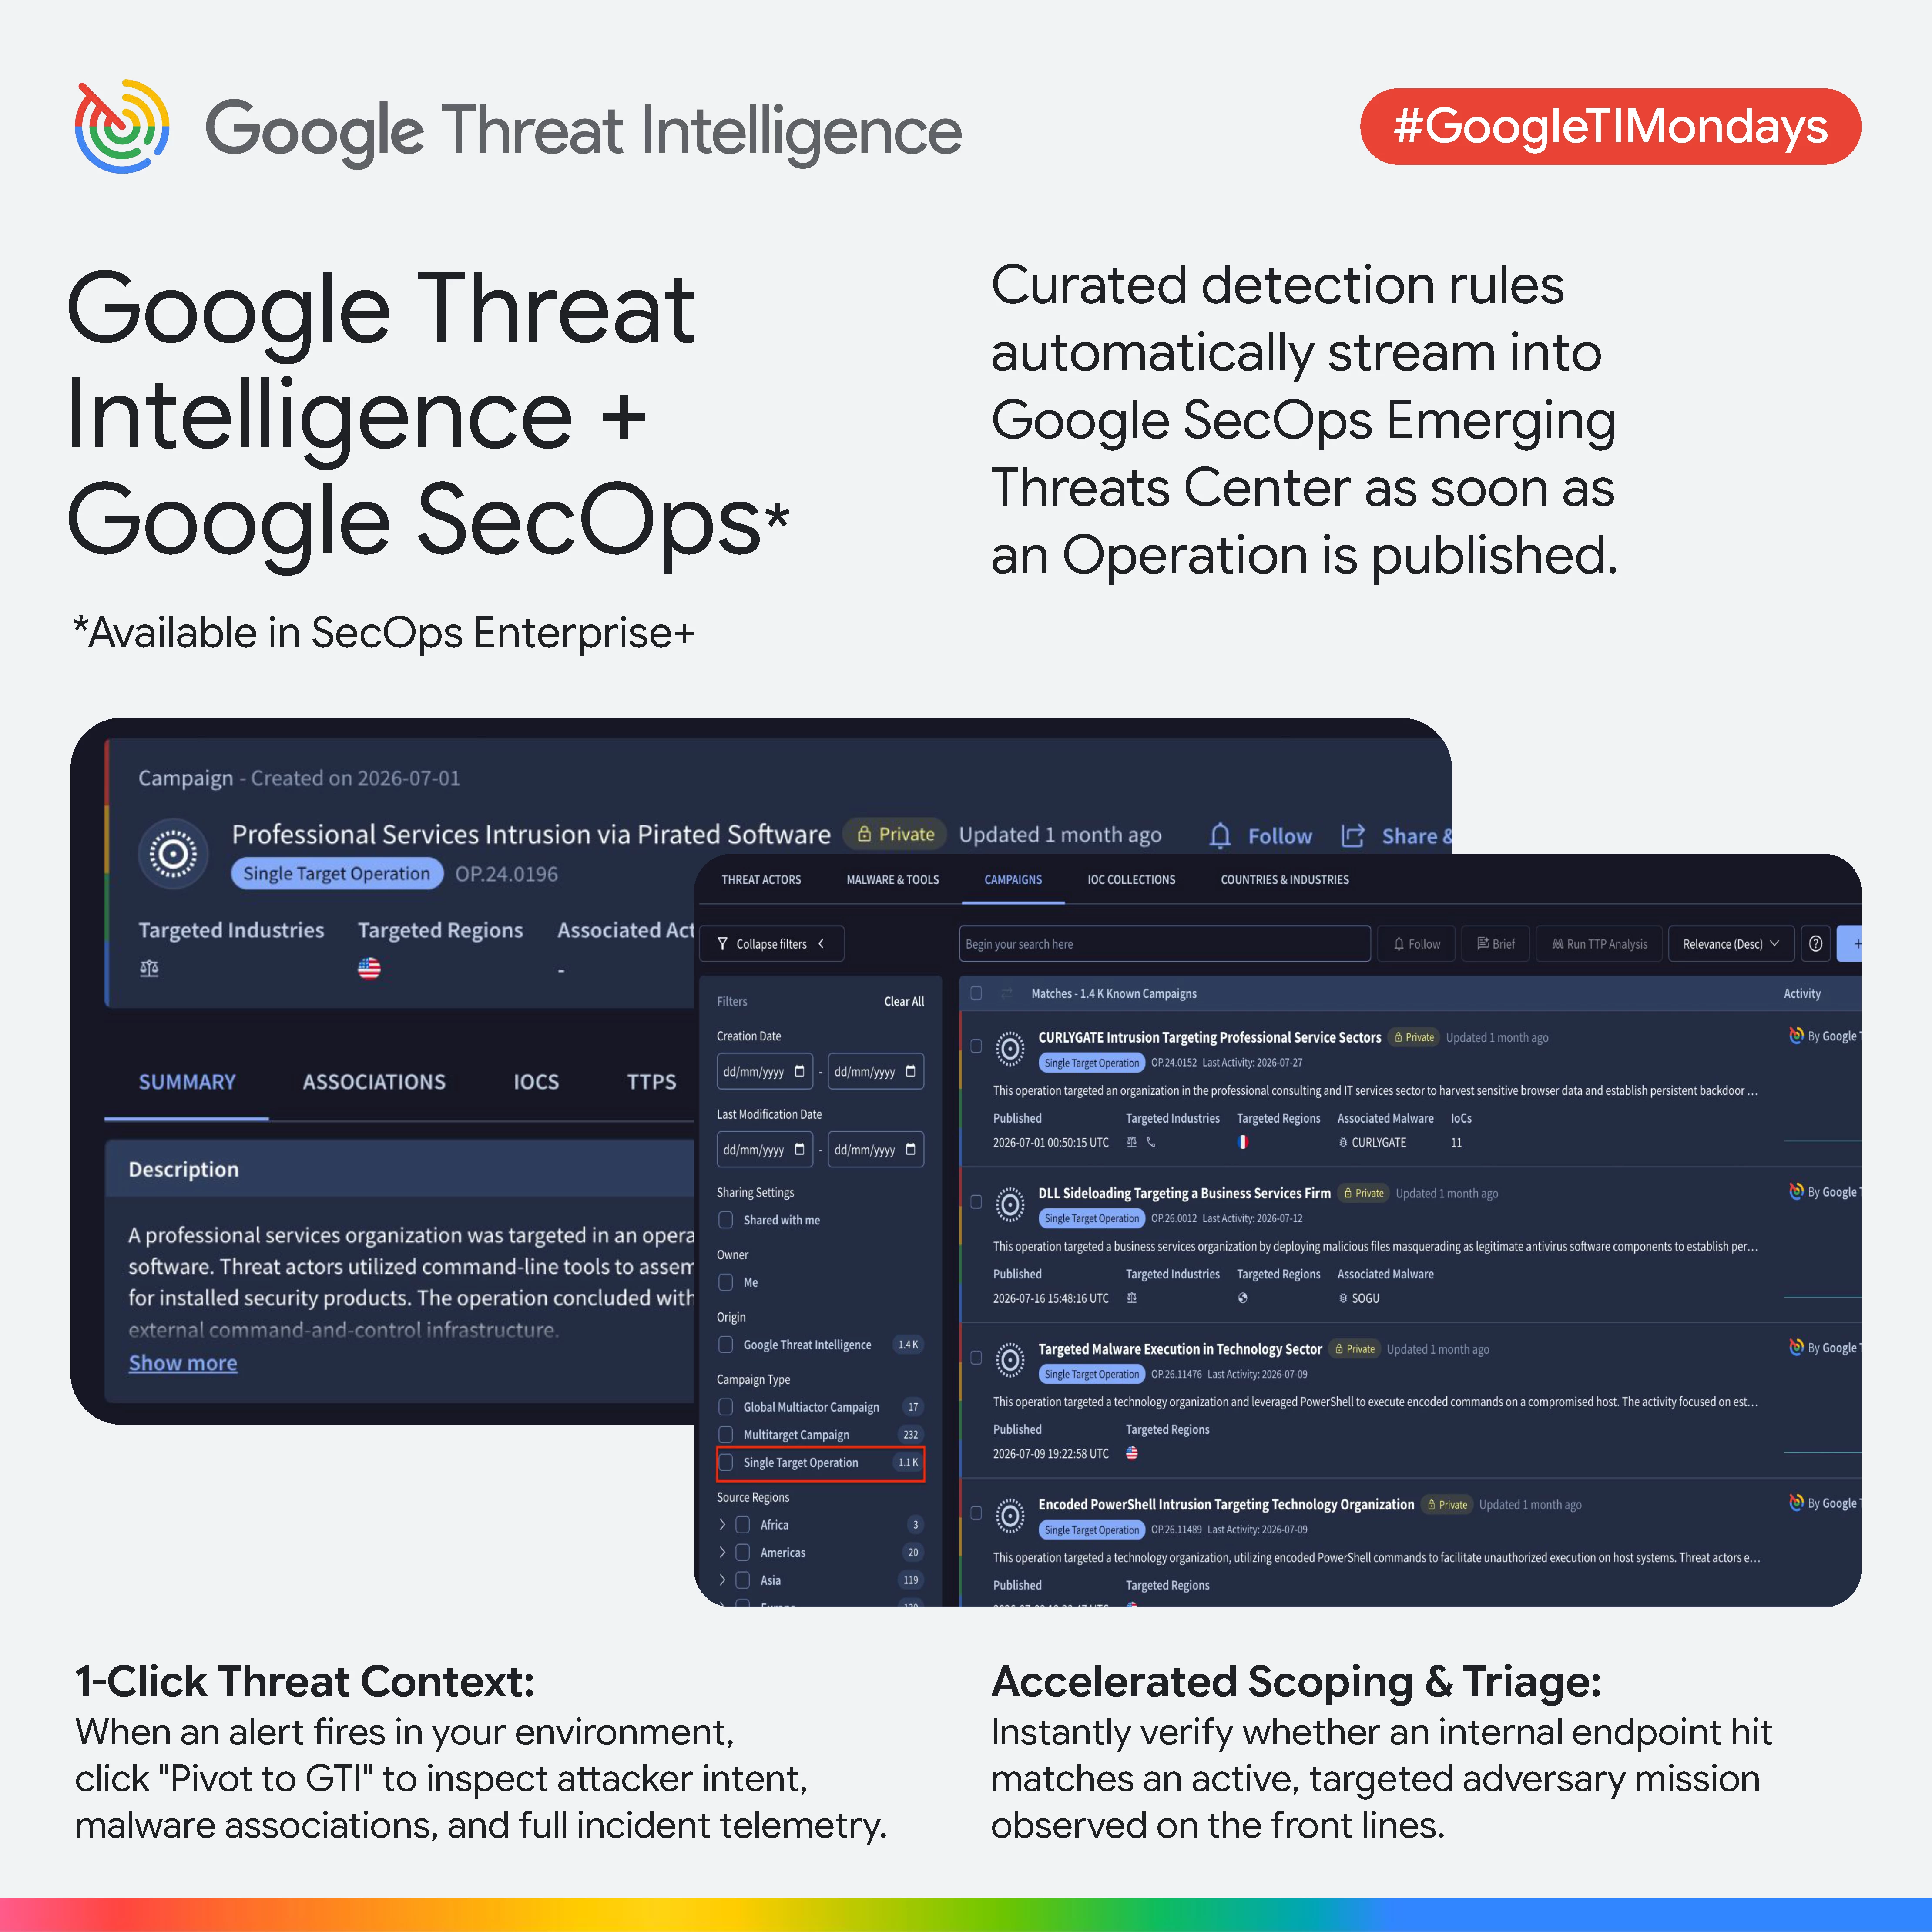
Integration with Google SecOps Enterprise+ allows curated detection rules to stream automatically into the Emerging Threats Center the moment an operation is published. Analysts investigating alerts can use one-click pivoting to inspect full threat context, verify attacker intent, and immediately determine whether an internal alert mirrors an active frontline campaign.
Single Target Operations bridge the critical gap between ongoing incident response and proactive defense, empowering security teams to deploy verified detections within minutes. We encourage you to explore Single Target Operations and experience how rapidly weaponized intelligence can safeguard your enterprise.