
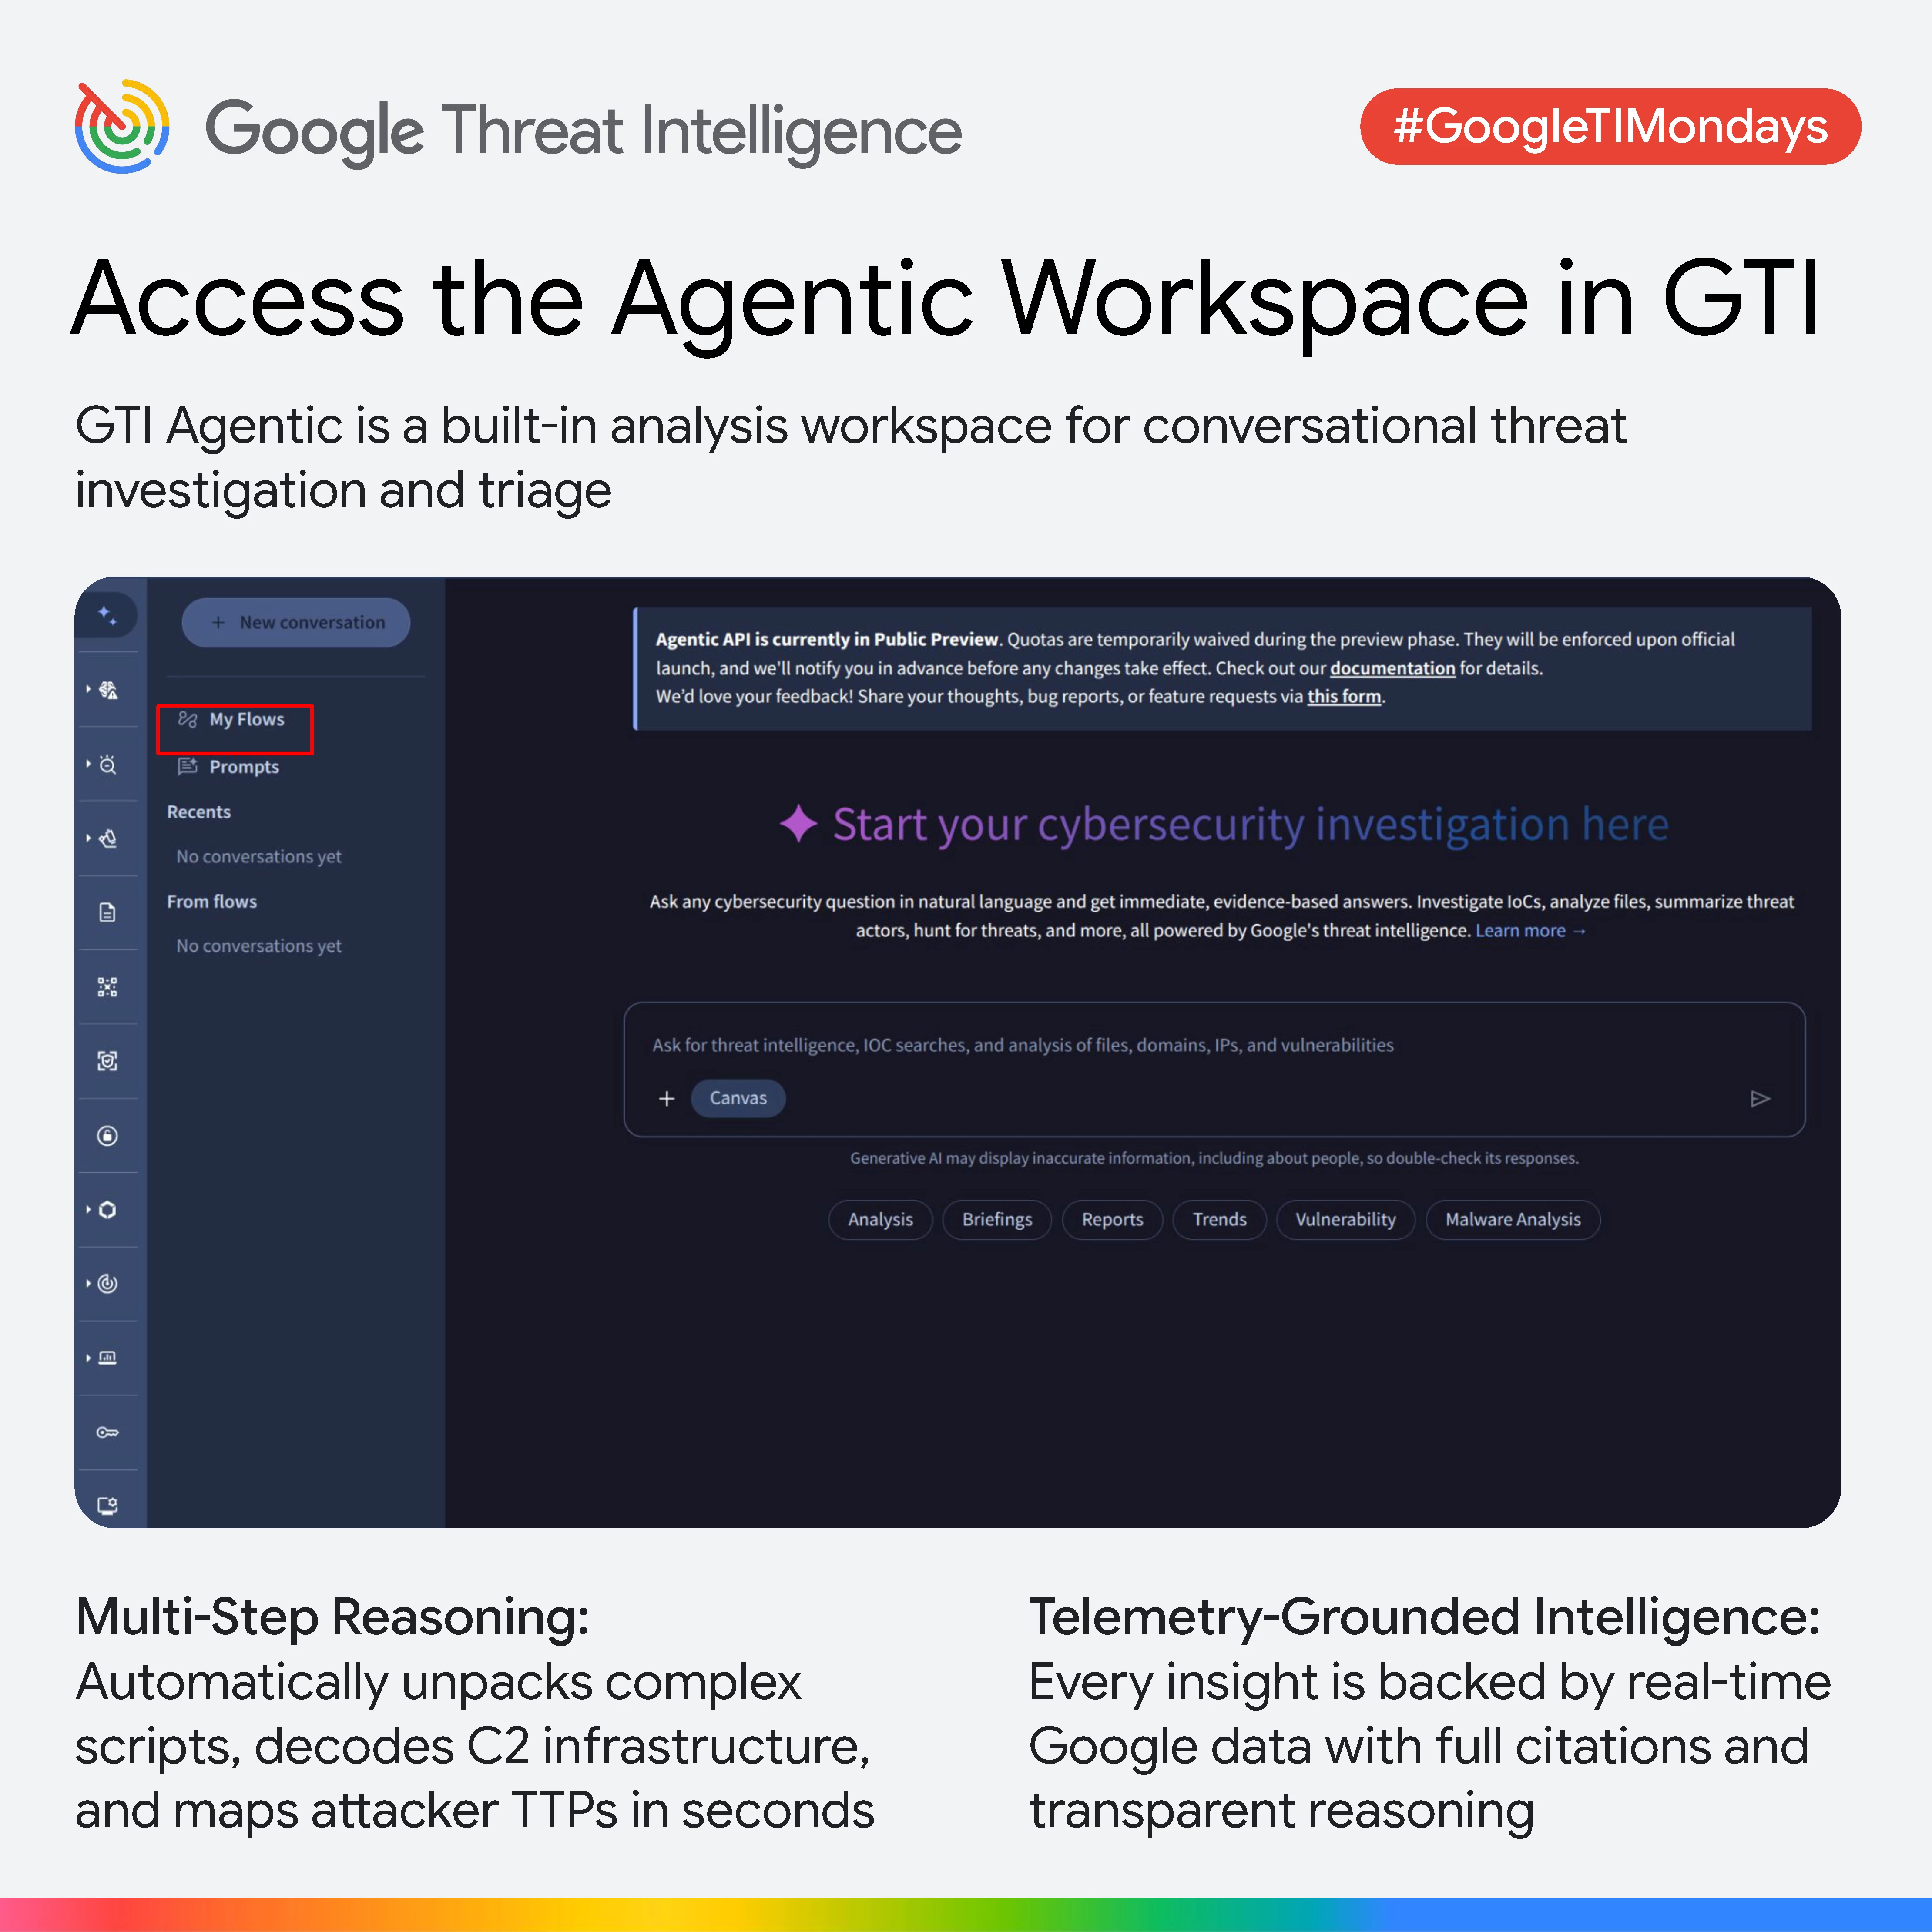
Security operations teams are constantly searching for innovative ways to streamline threat investigations and outpace sophisticated adversaries. To address this critical challenge, Google Threat Intelligence has introduced an exciting new feature called Agentic Flows. This powerful capability is designed to transform guided agentic workflows into highly scalable, automated solutions. Built directly within the Agentic Workspace, this built-in analysis platform is specifically optimized for conversational threat investigation and triage.
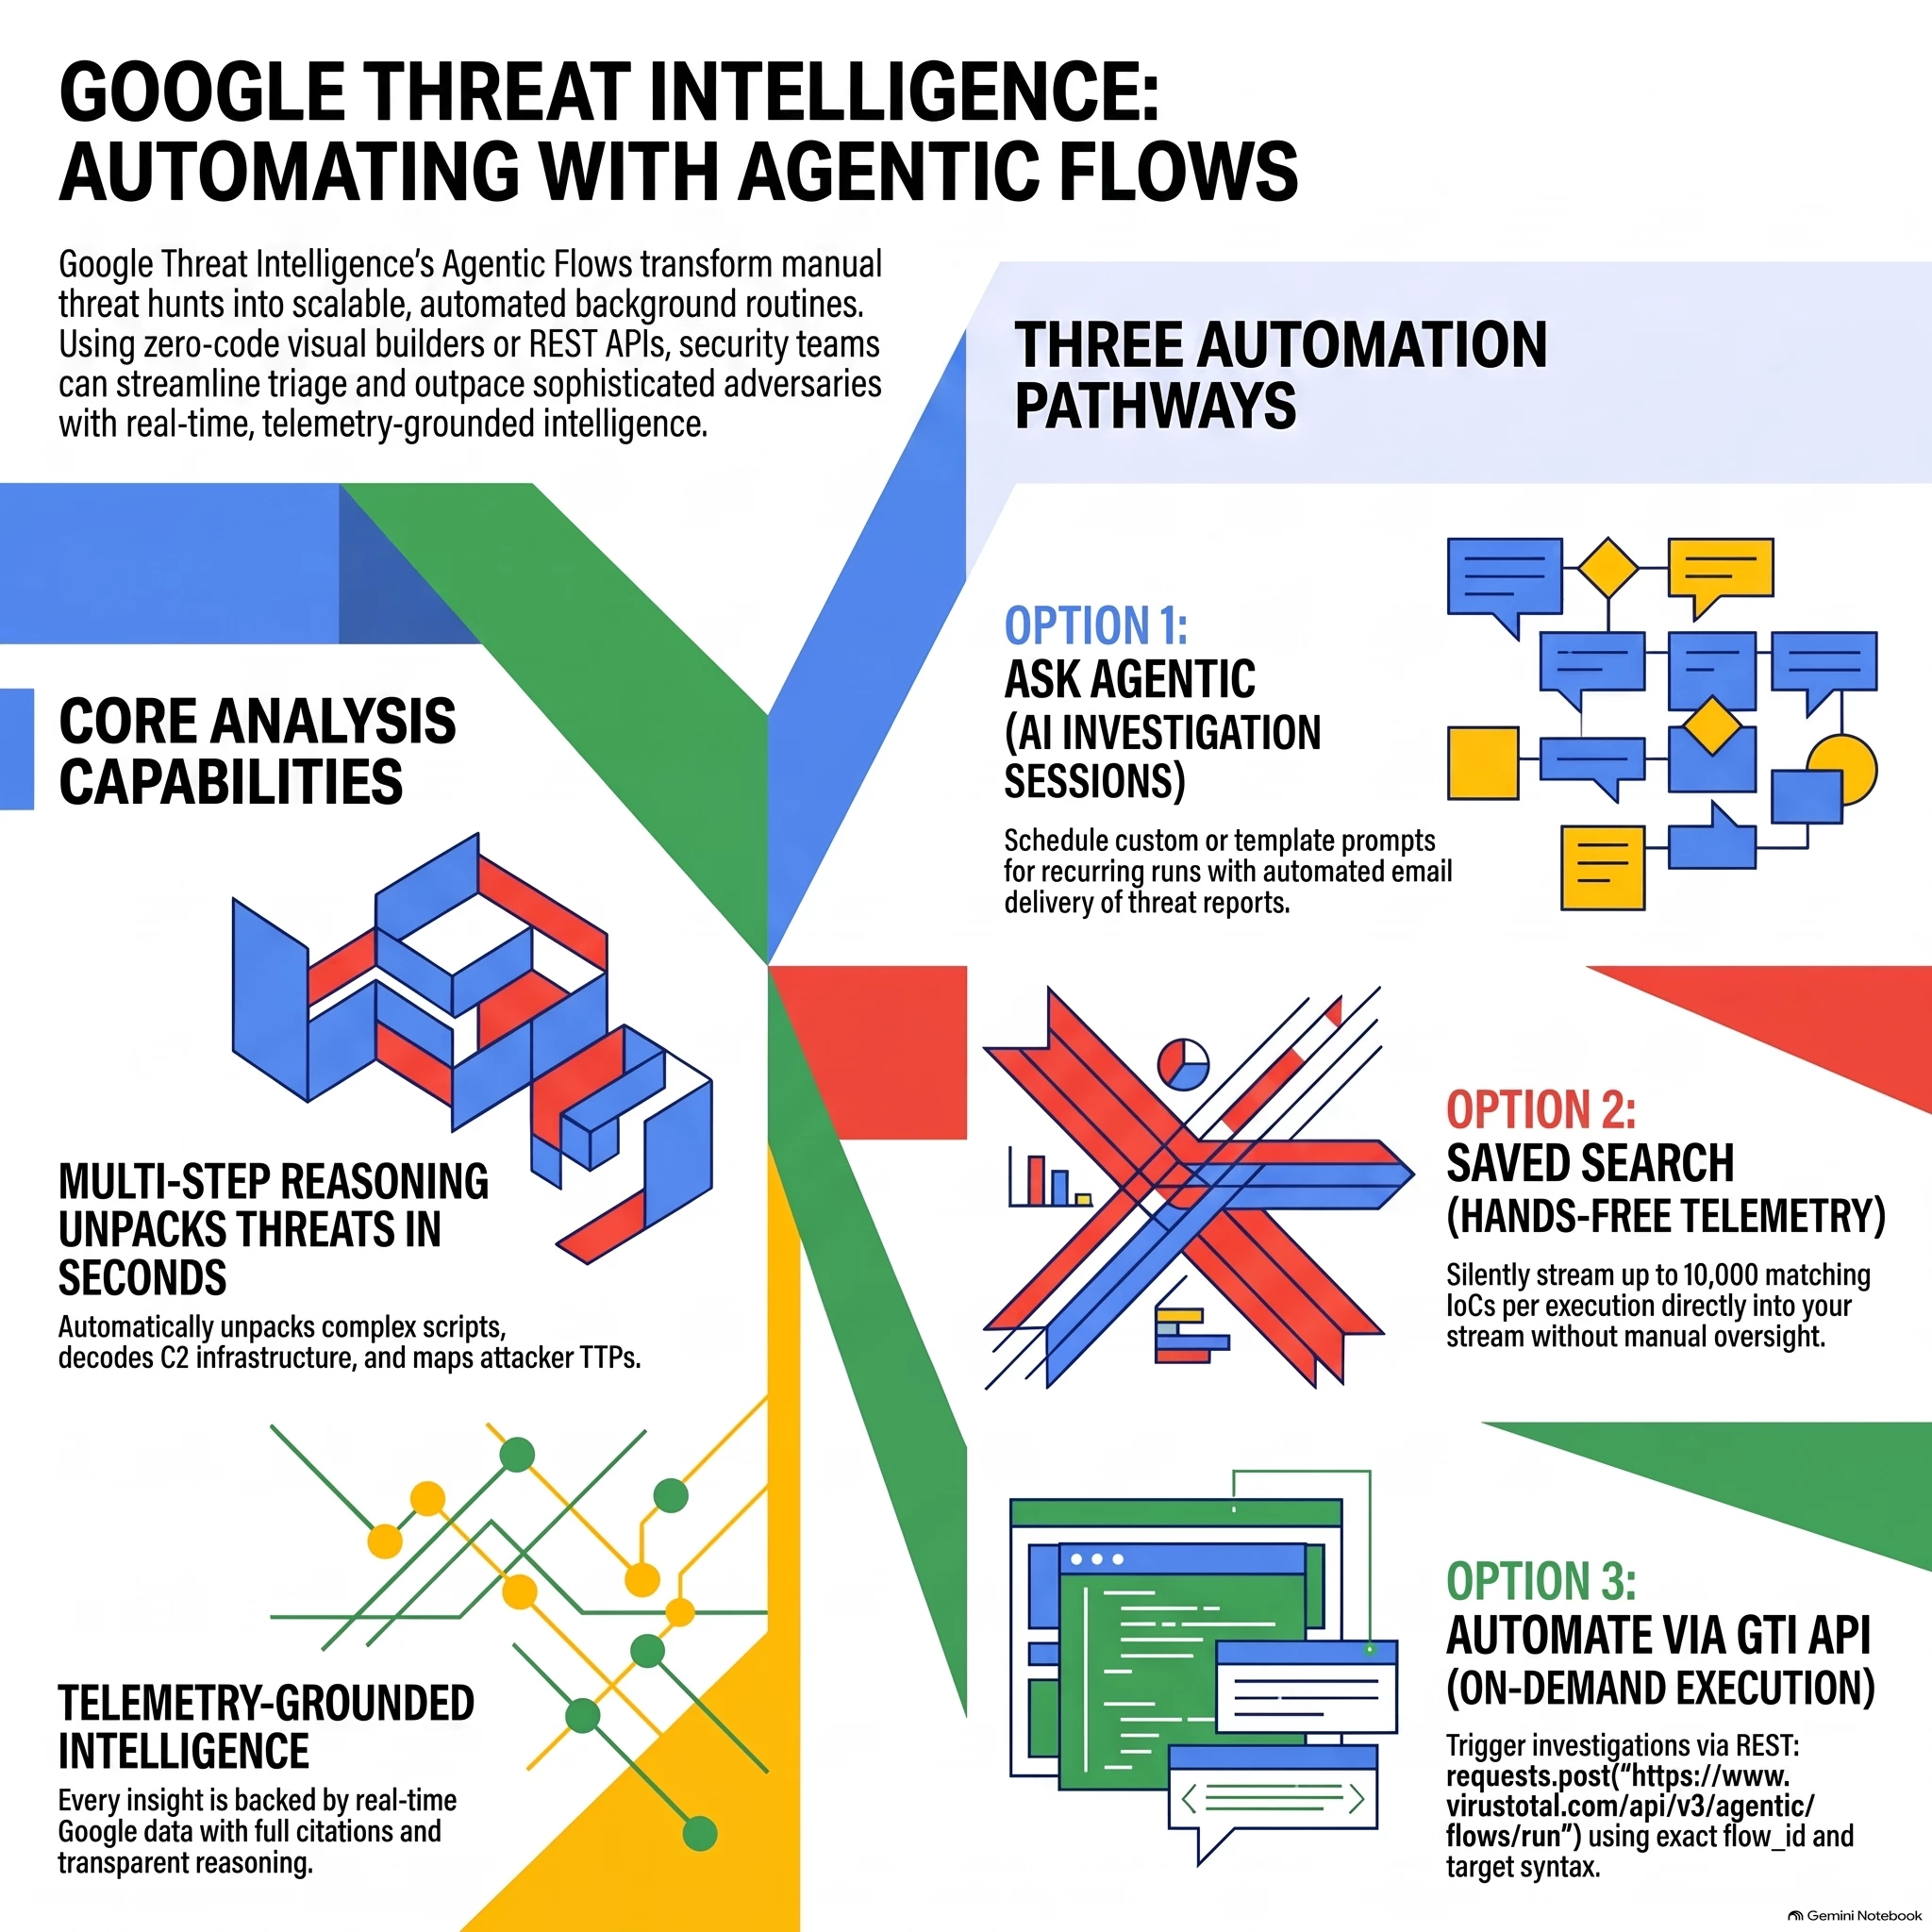
By combining multi-step reasoning with telemetry-grounded intelligence, Agentic Flows can automatically unpack complex scripts, decode command-and-control infrastructure, and map attacker techniques in seconds. Importantly, every single insight generated is backed by real-time Google data, complete with clear citations and transparent reasoning.
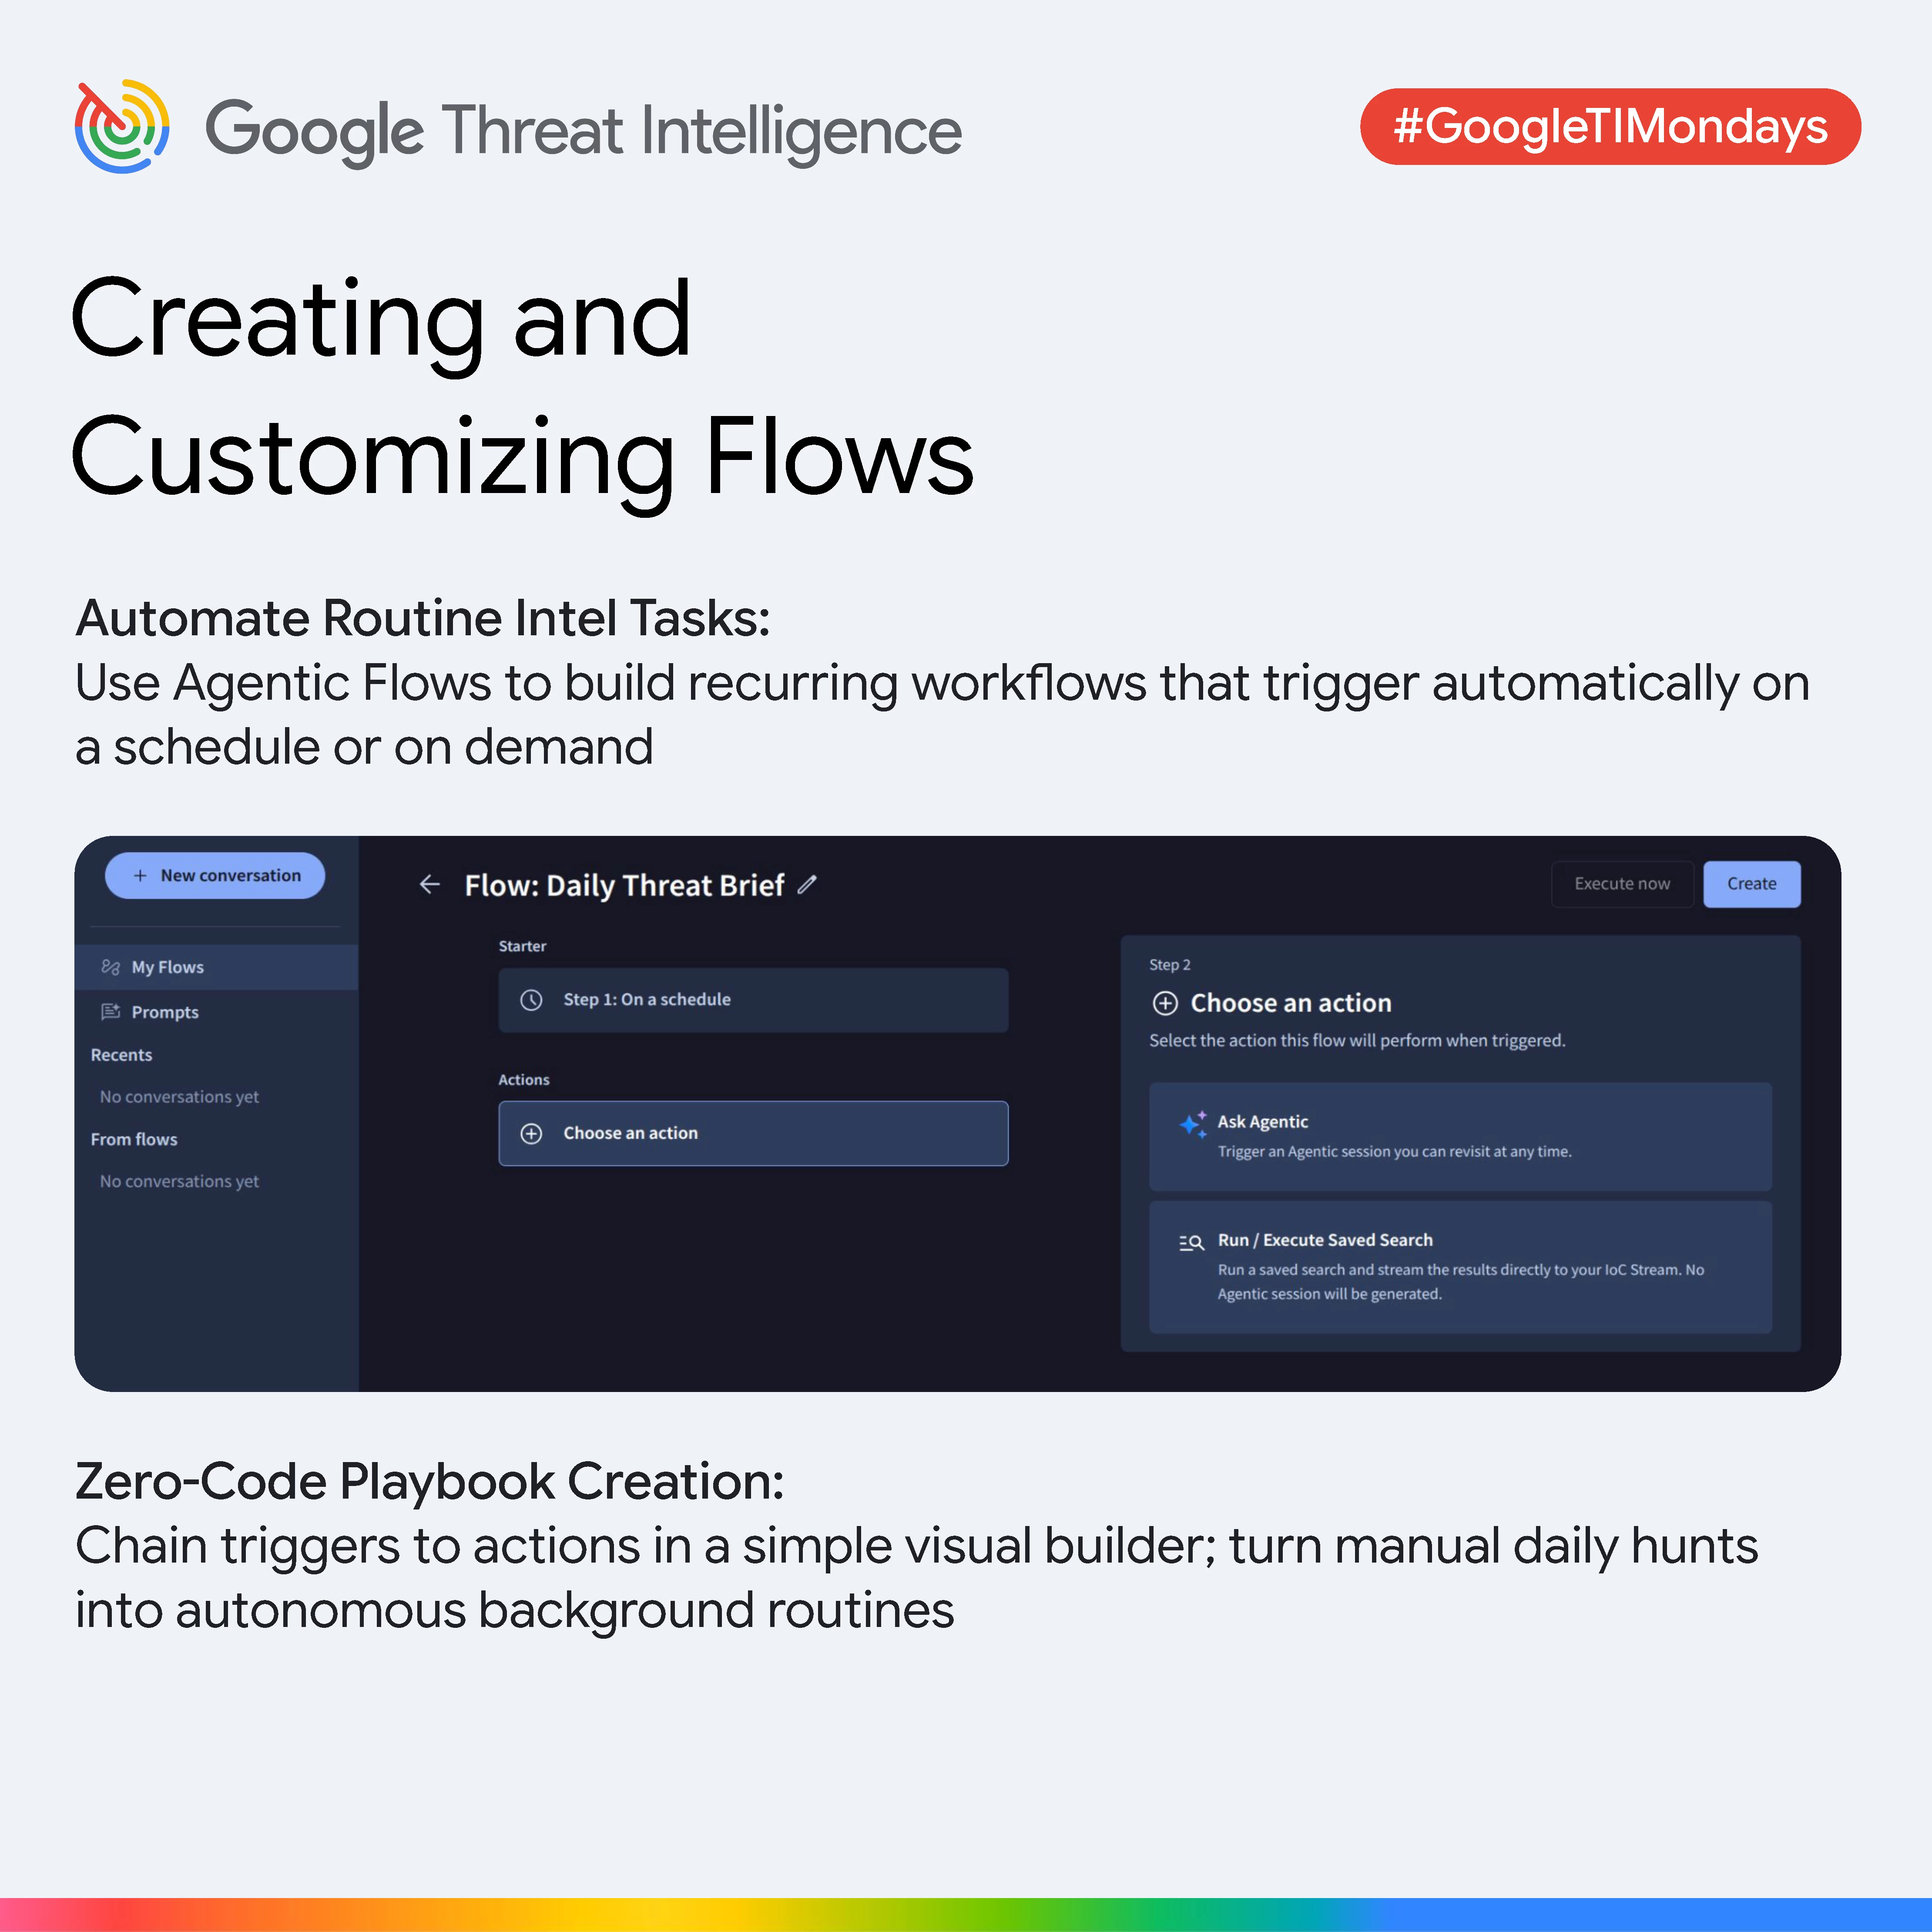
Organizations can leverage Agentic Flows through three distinct automation pathways:
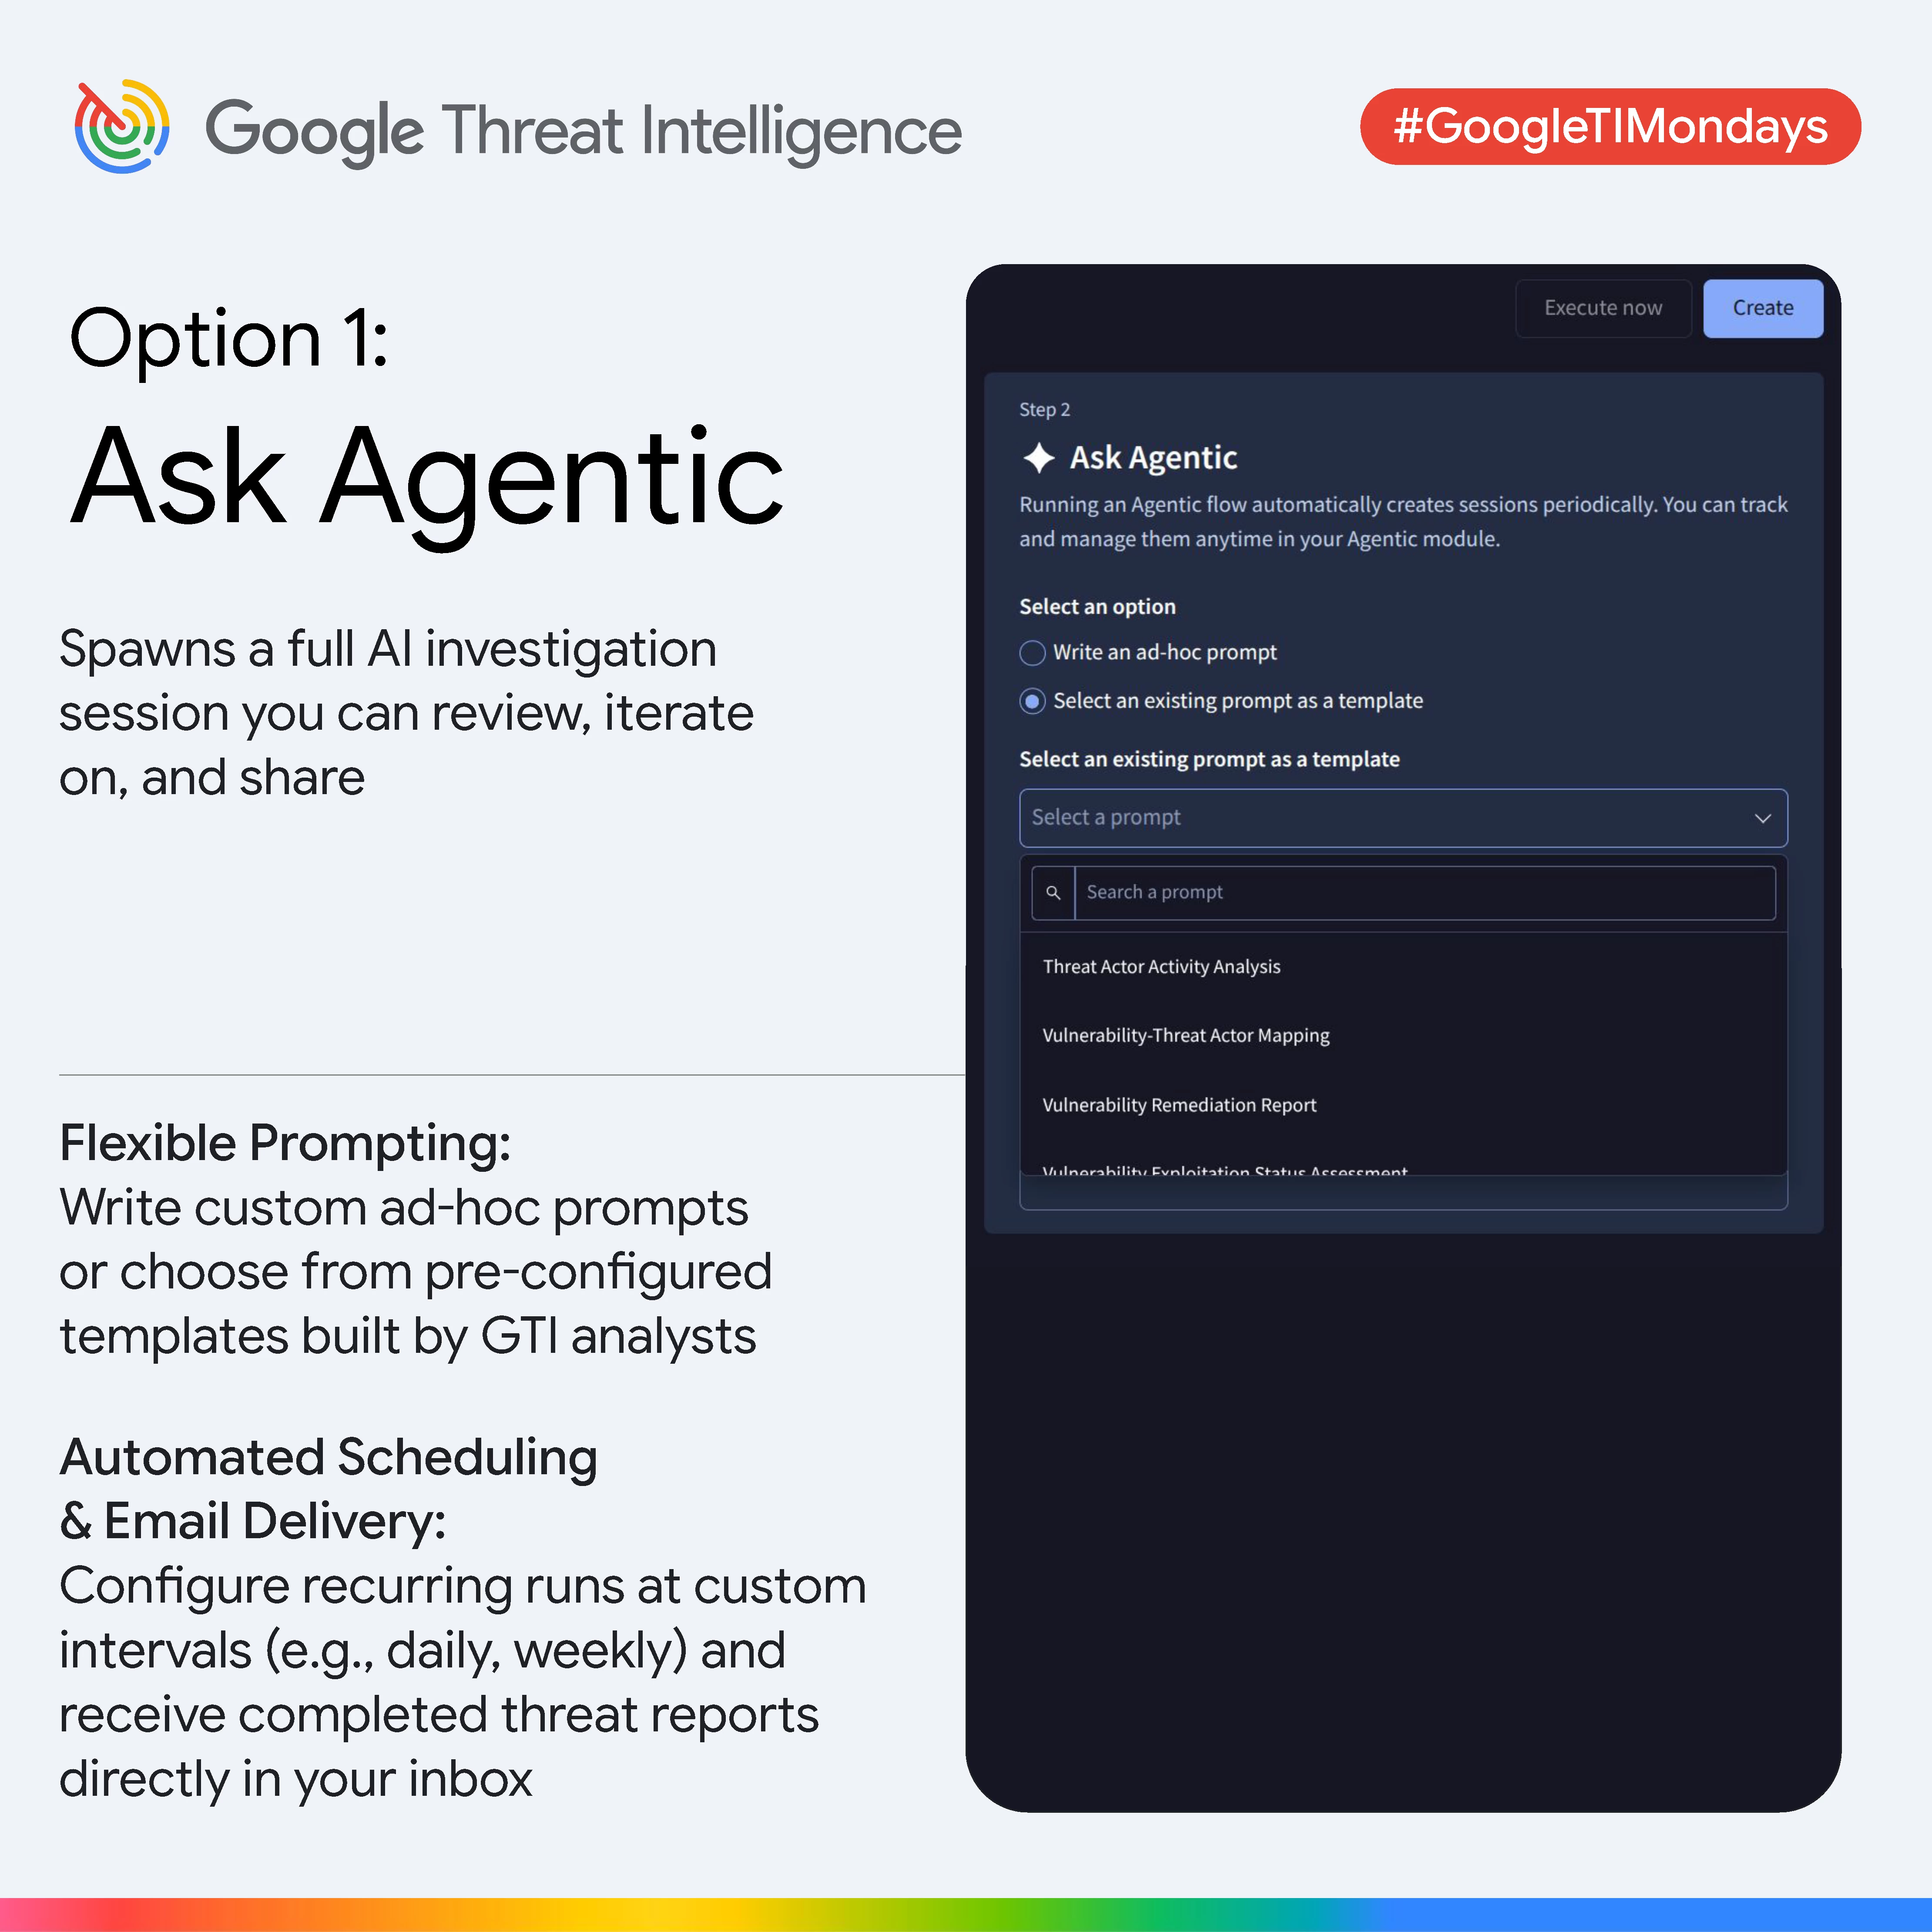
First, the Ask Agentic option allows teams to spawn complete, interactive AI investigation sessions. Security professionals can write custom prompts or choose from pre-configured templates designed by expert analysts, scheduling them to run periodically and deliver finished reports directly to their email inbox.
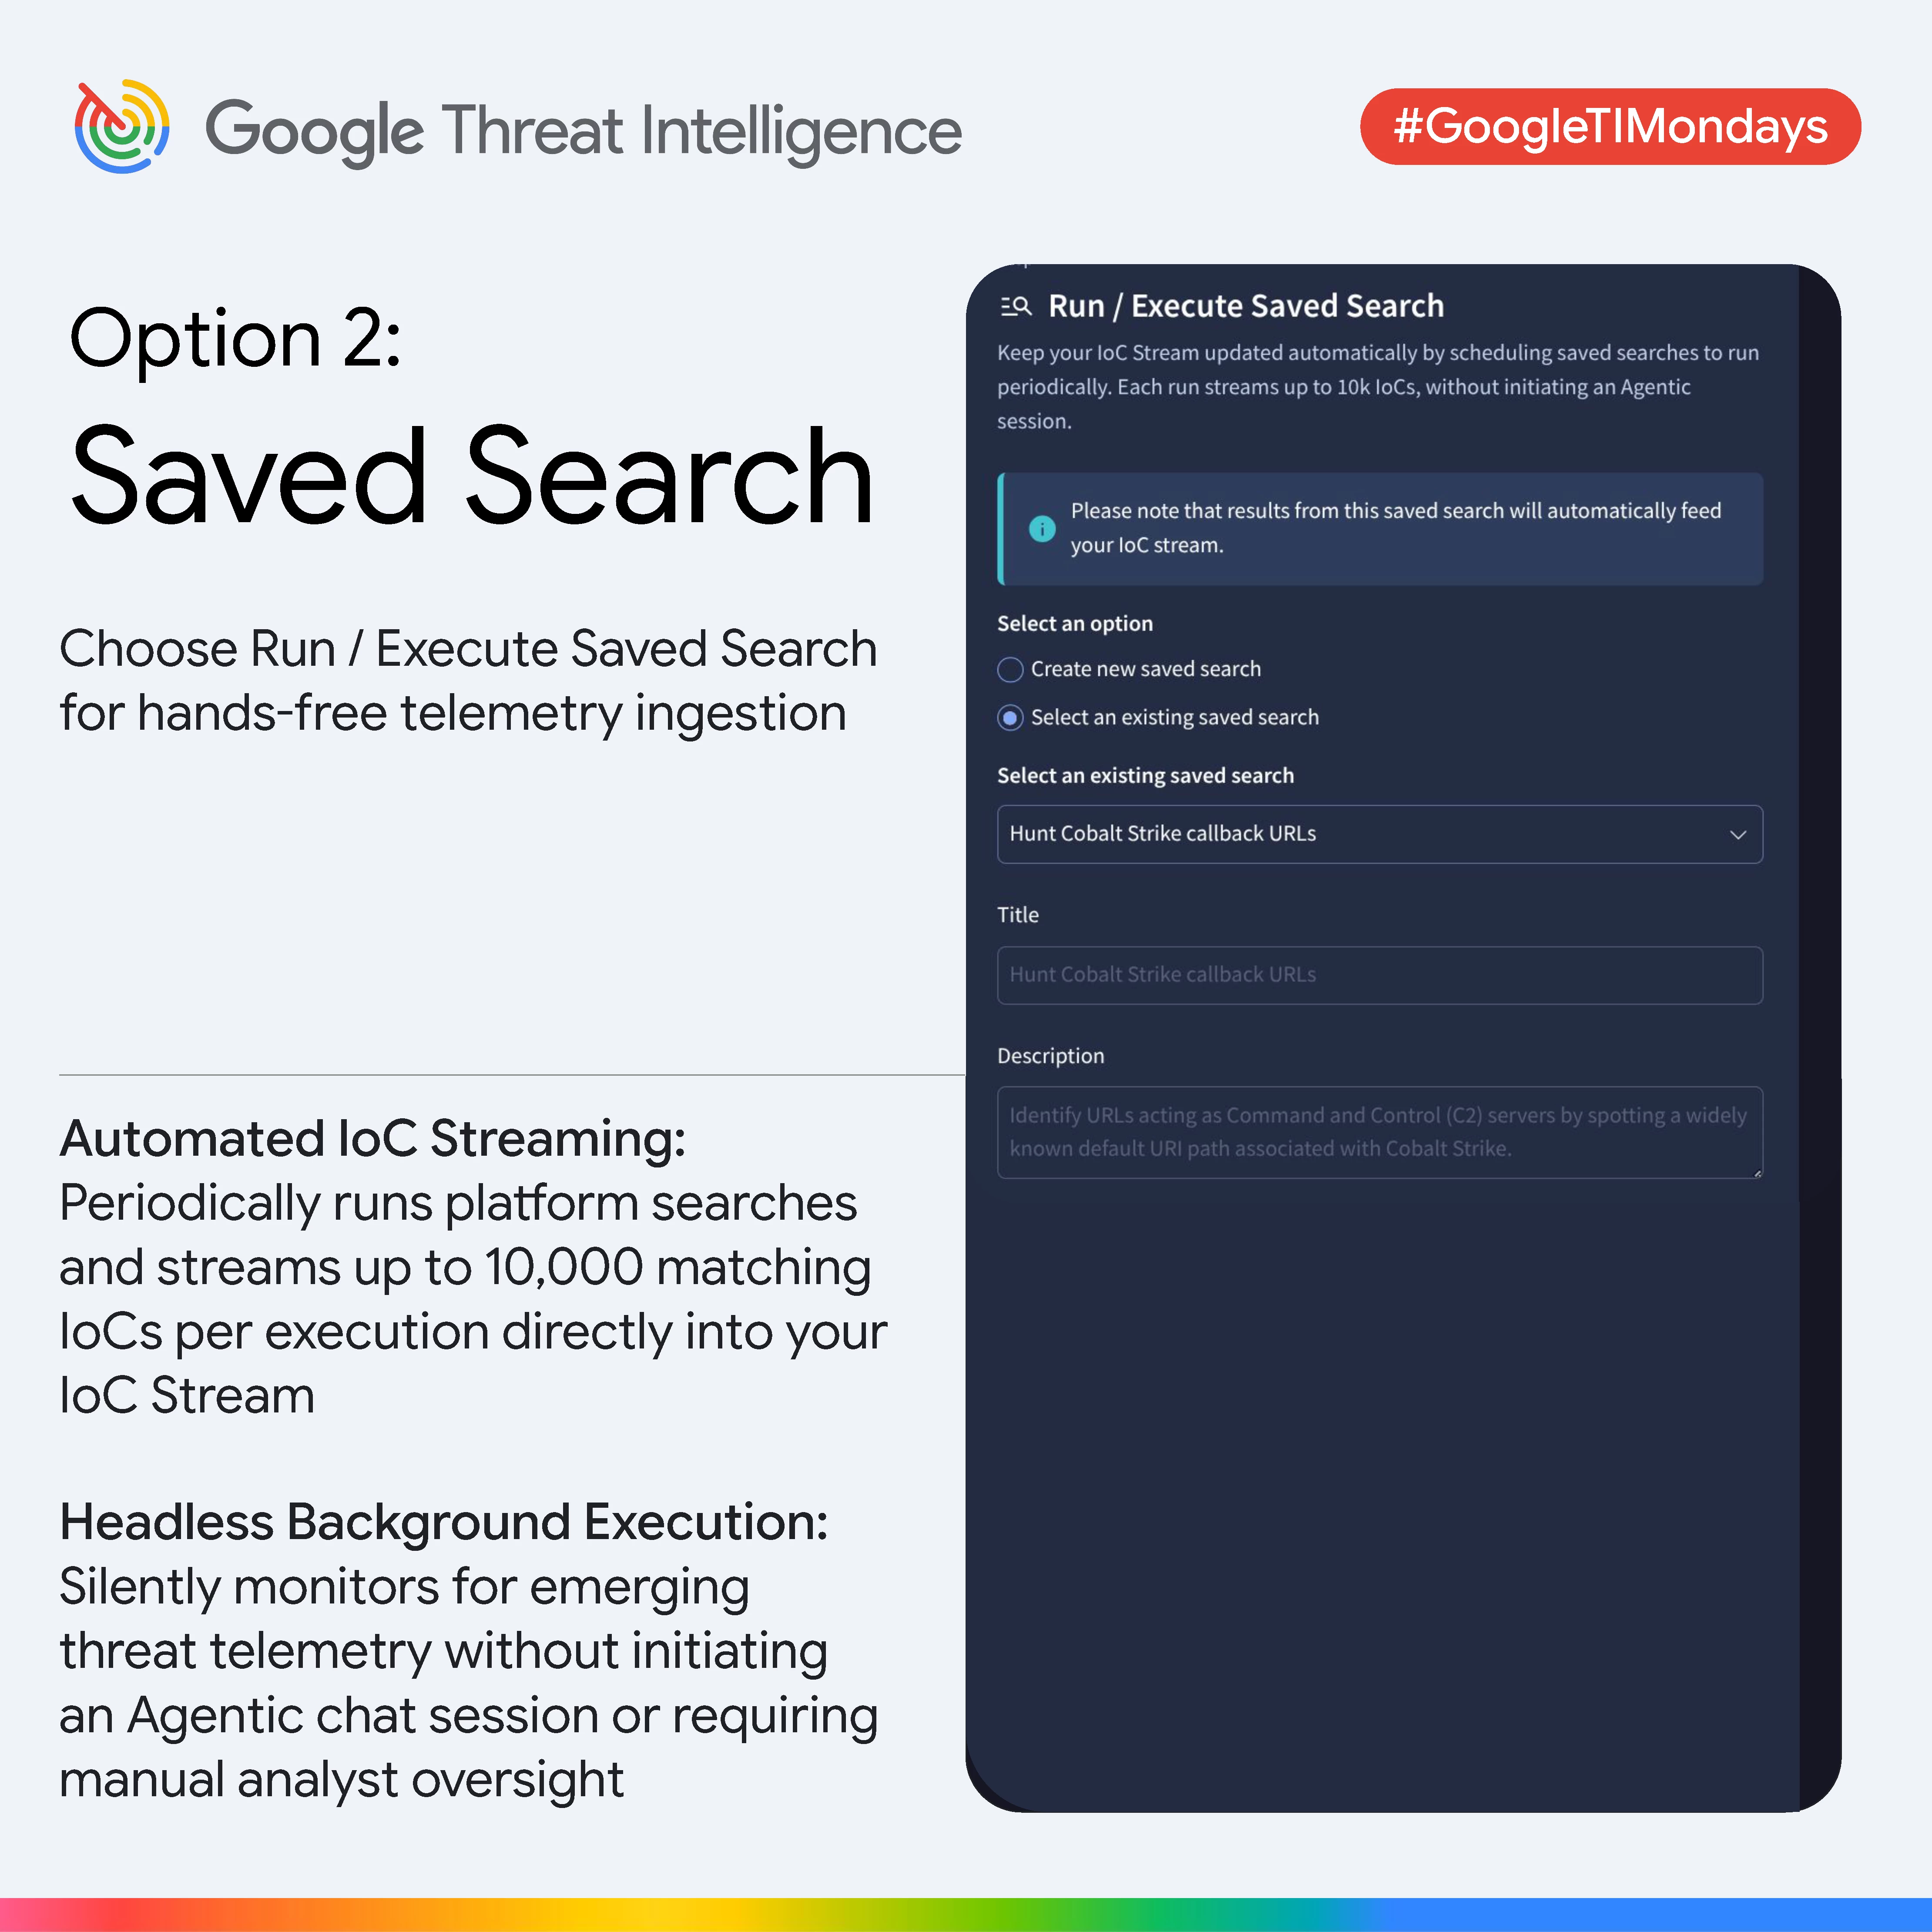
Second, the Saved Search feature offers hands free telemetry ingestion. It runs scheduled platform searches in the background, streaming up to ten thousand matching indicators of compromise per execution directly into an active stream without requiring manual oversight or starting active chat sessions.
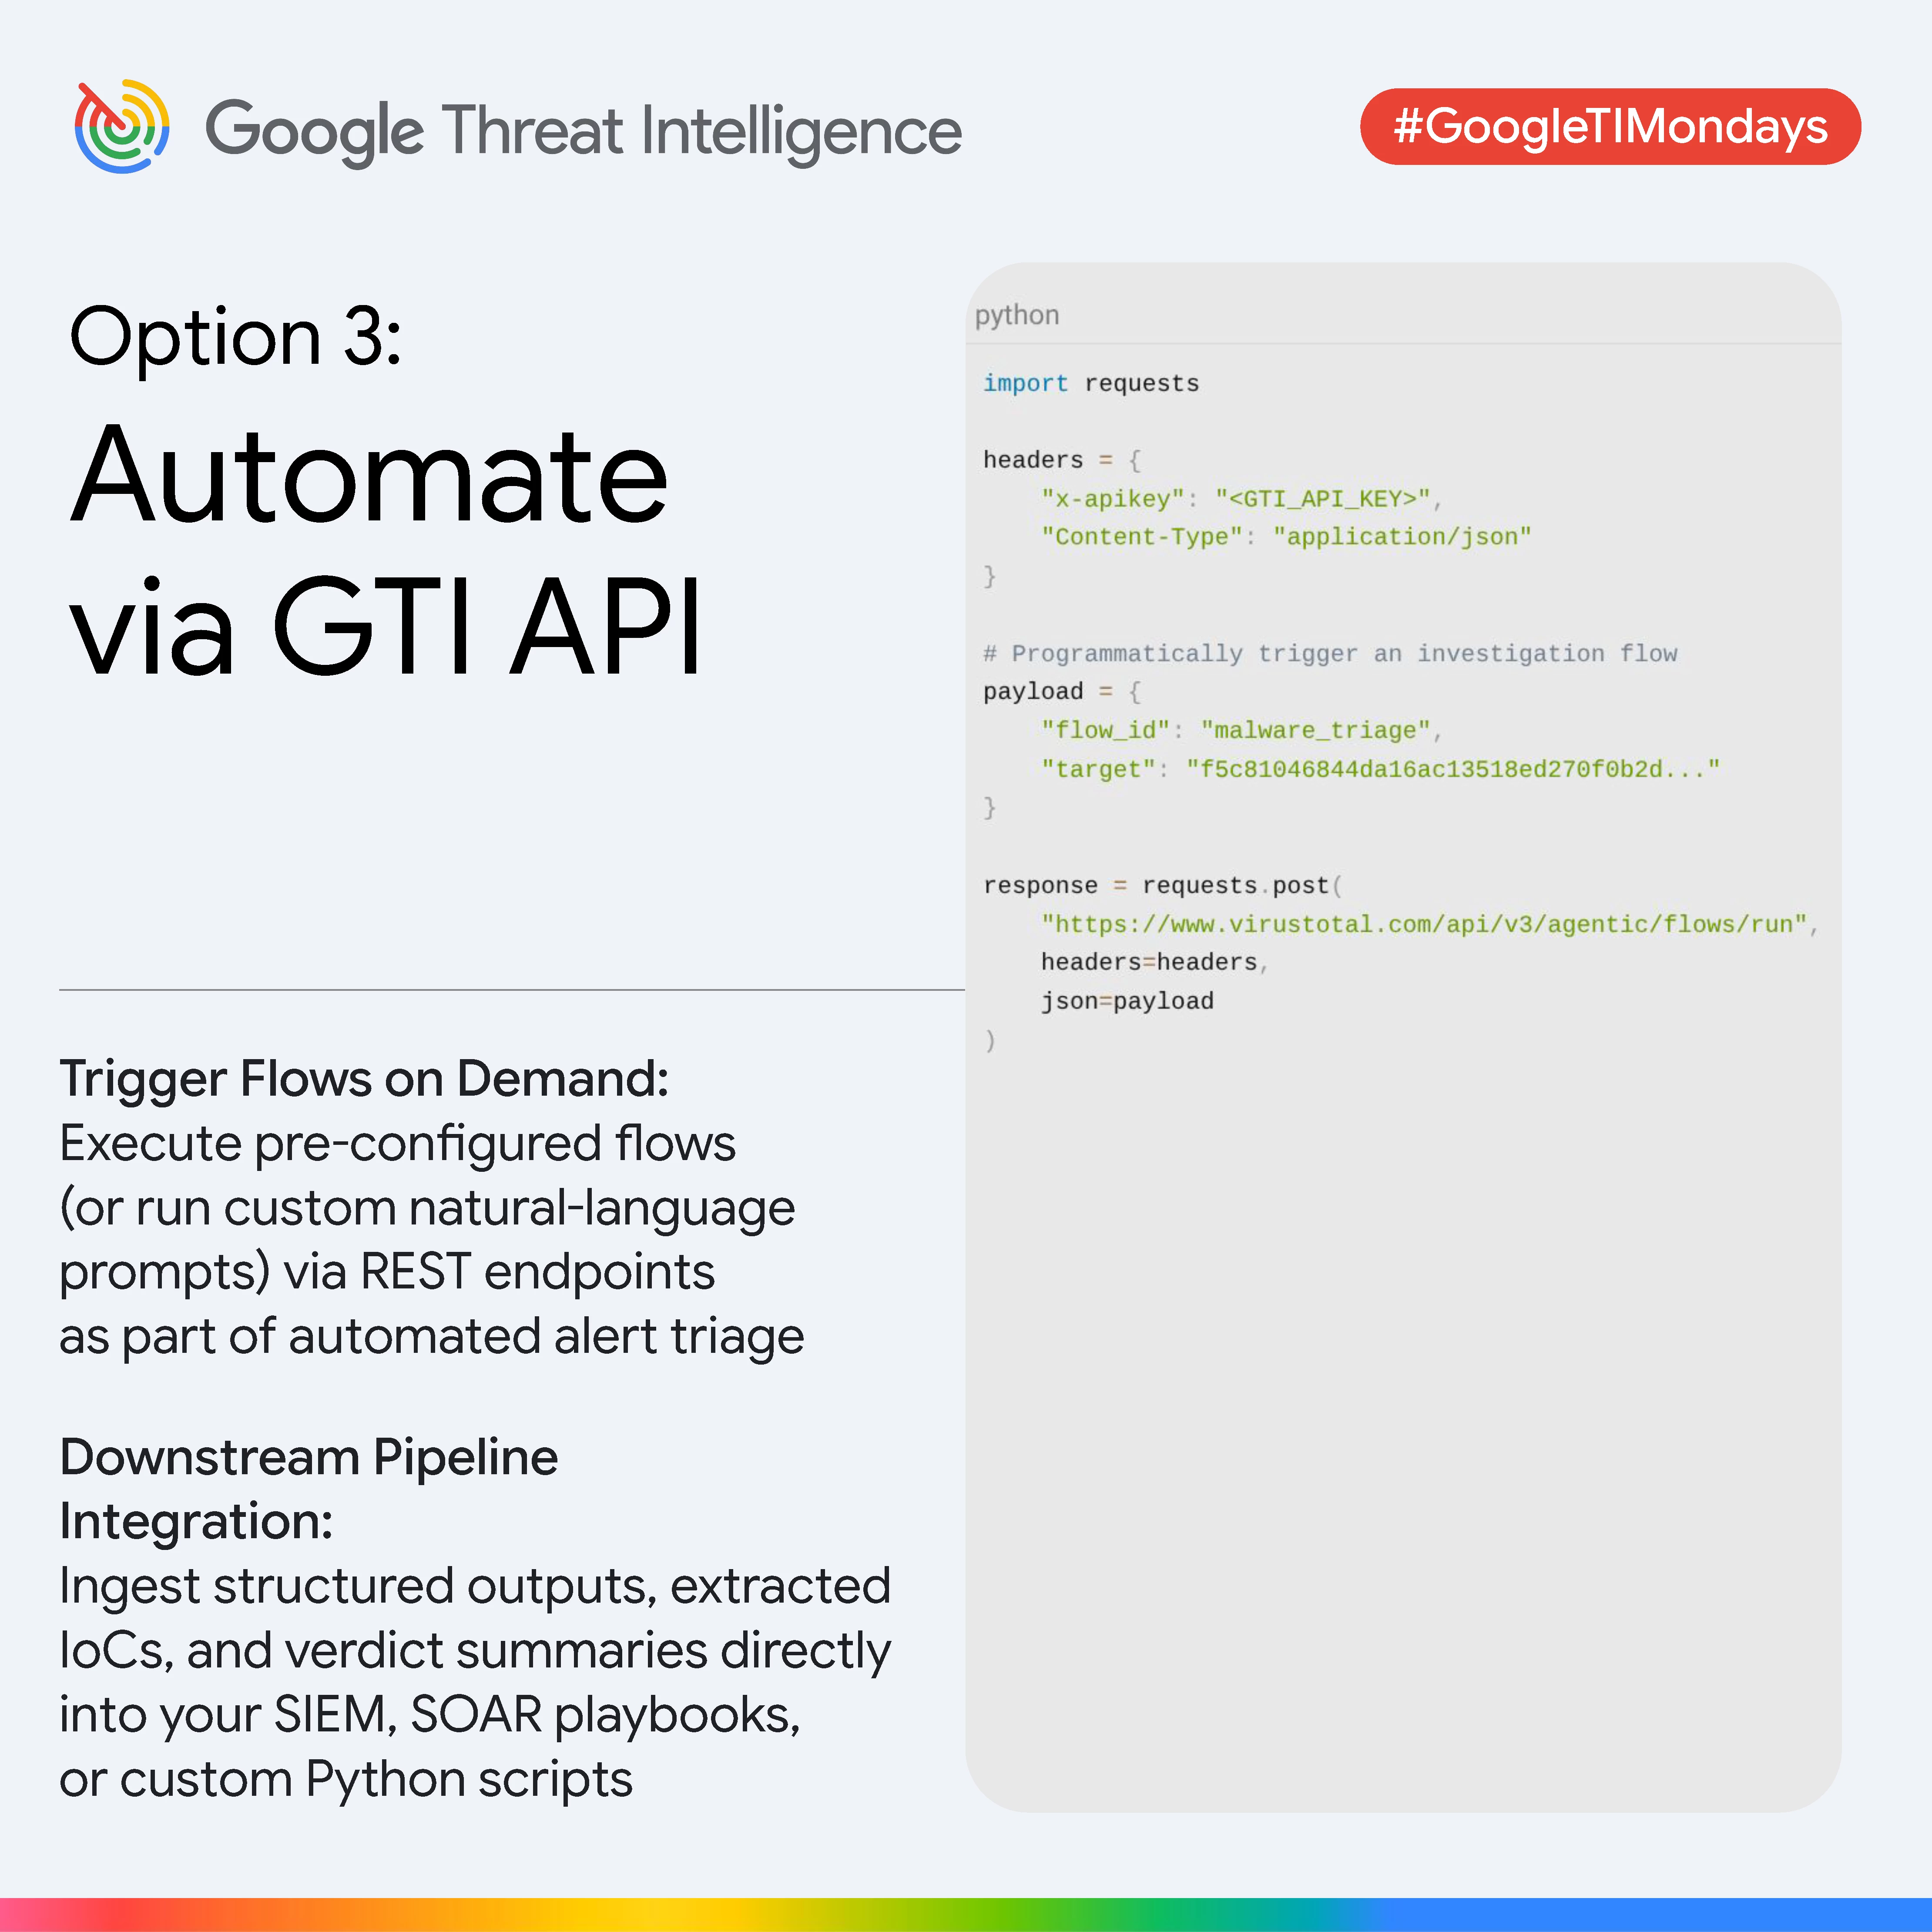
Third, the API option allows for on-demand programmatic execution. Teams can trigger workflows via REST endpoints during alert triage and feed structured results directly into existing tools like SIEM platforms, SOAR playbooks, or custom Python scripts.
By using a zero code visual builder to chain triggers to actions, security teams can easily convert manual daily threat hunts into efficient background routines, significantly accelerating their detection and response capabilities.
Additional Resources and Links:
