
We are excited to invite our Google Security Operations Enterprise Plus (E+) customers to enroll in the Private Preview of Mandiant Recommended rules in Google Security Operations.
Request Enrollment in the Private Preview Here
Establishing and maintaining a high-fidelity threat detection baseline is one of the toughest operational challenges for any Security Operations Center (SOC). Enable too many out-of-the-box detections at once, and analysts are quickly buried in false positives from noisy, single-event rules. Spend months manually reviewing, tuning, and enabling rules one by one, and critical coverage gaps remain open while threat actors evolve.
As part of our private preview, we are aiming to solve this trade-off by delivering an automated, curated threat detection baseline that you can subscribe to, and will automatically deploy curated rules that fit the right blend of precision and recall.
High-Fidelity Coverage Without the Alert Fatigue
Rather than relying on isolated, single-event signatures that generate high alert volume, the Mandiant Recommended baseline prioritizes composite detections (multi-event and multi-detection correlations) paired with high-precision Applied Threat Intelligence (ATI). By correlating multiple stages of attacker tradecraft before raising an alert, these detections deliver higher confidence by default and significantly reduce initial rule-tuning overhead.
Key Features and Capabilities
- Curated Composite & ATI Detection Baseline: Automatically deploy rules that focus on high-signal, multi-stage adversary behaviors.
- One-Click Tag Subscription (google.mandiant.recommended): Instead of manual rule-by-rule configuration, a background tag subscription service automatically populates, enables, and synchronizes recommended rules with their optimal detection and alerting settings.
- Flexible Overrides & Alignment Tracking: Need to tailor a rule for your environment? You can override alerting or detection settings on individual rules or apply rule exclusions.
Why Join the Private Preview? Shape the Future of SecOps Detections
This Private Preview is a collaborative partnership between enrolled customers and the Google SecOps product and engineering teams.
What We Are Looking For
During the private preview, we are seeking active feedback from SecOps Enterprise Plus (E+) detection engineers and SOC leaders in two core areas:
- Rule Quality & Signal-to-Noise: Deep operational feedback on True Positive (TP) and False Positive (FP) alert rates across your live production telemetry.
- Detection Relevance: Honest assessment of whether the detections recommended in this baseline align with the threat models, attack surfaces, and priorities that matter most to your organization.
We have high confidence in our initial set of rules, but want to partner with customers to understand how we can extend the scope of rules that meet the right mix of precision and recall.
What You Gain by Enrolling
Private Preview participants will receive early access to upcoming capabilities being launched as part of this initiative:
- Log-Type-to-Detection Mapping: Intelligent recommendation mapping that analyzes the log types you are already ingesting to deliver precise, actionable detection recommendations tailored to your active telemetry footprint.
- Automated Rule Baselining: Streamlined, automated baselining workflows specifically built for Mandiant Recommended rules to further reduce tuning toil before alerts hit the SOC queue. While tracking configuration drift and resetting to Mandiant defaults at any time using View diff and align .
How to Enroll (Private Preview)
This capability is currently in Private Preview for Google Security Operations Enterprise Plus (E+) customers.
Important Note: Because this feature is in Private Preview, it cannot be enabled via the self-service Settings > Preview Features (Public Preview feature flags) page in the console. To have this feature enabled for your tenant, please submit the enrollment form below:
Complete the Mandiant Recommended Rules Private Preview Enrollment Form
Getting Started Once Your Tenant Is Enabled
Once our team confirms that your tenant has been enabled for the Private Preview, you can explore the rules and manage your tag subscription directly from the Unified Rules page:
- Locate Mandiant Recommended Rules: Navigate to Rules & Detections > Rules in the Google SecOps console. In the search bar on the right, enter: tags:google.mandiant.recommended
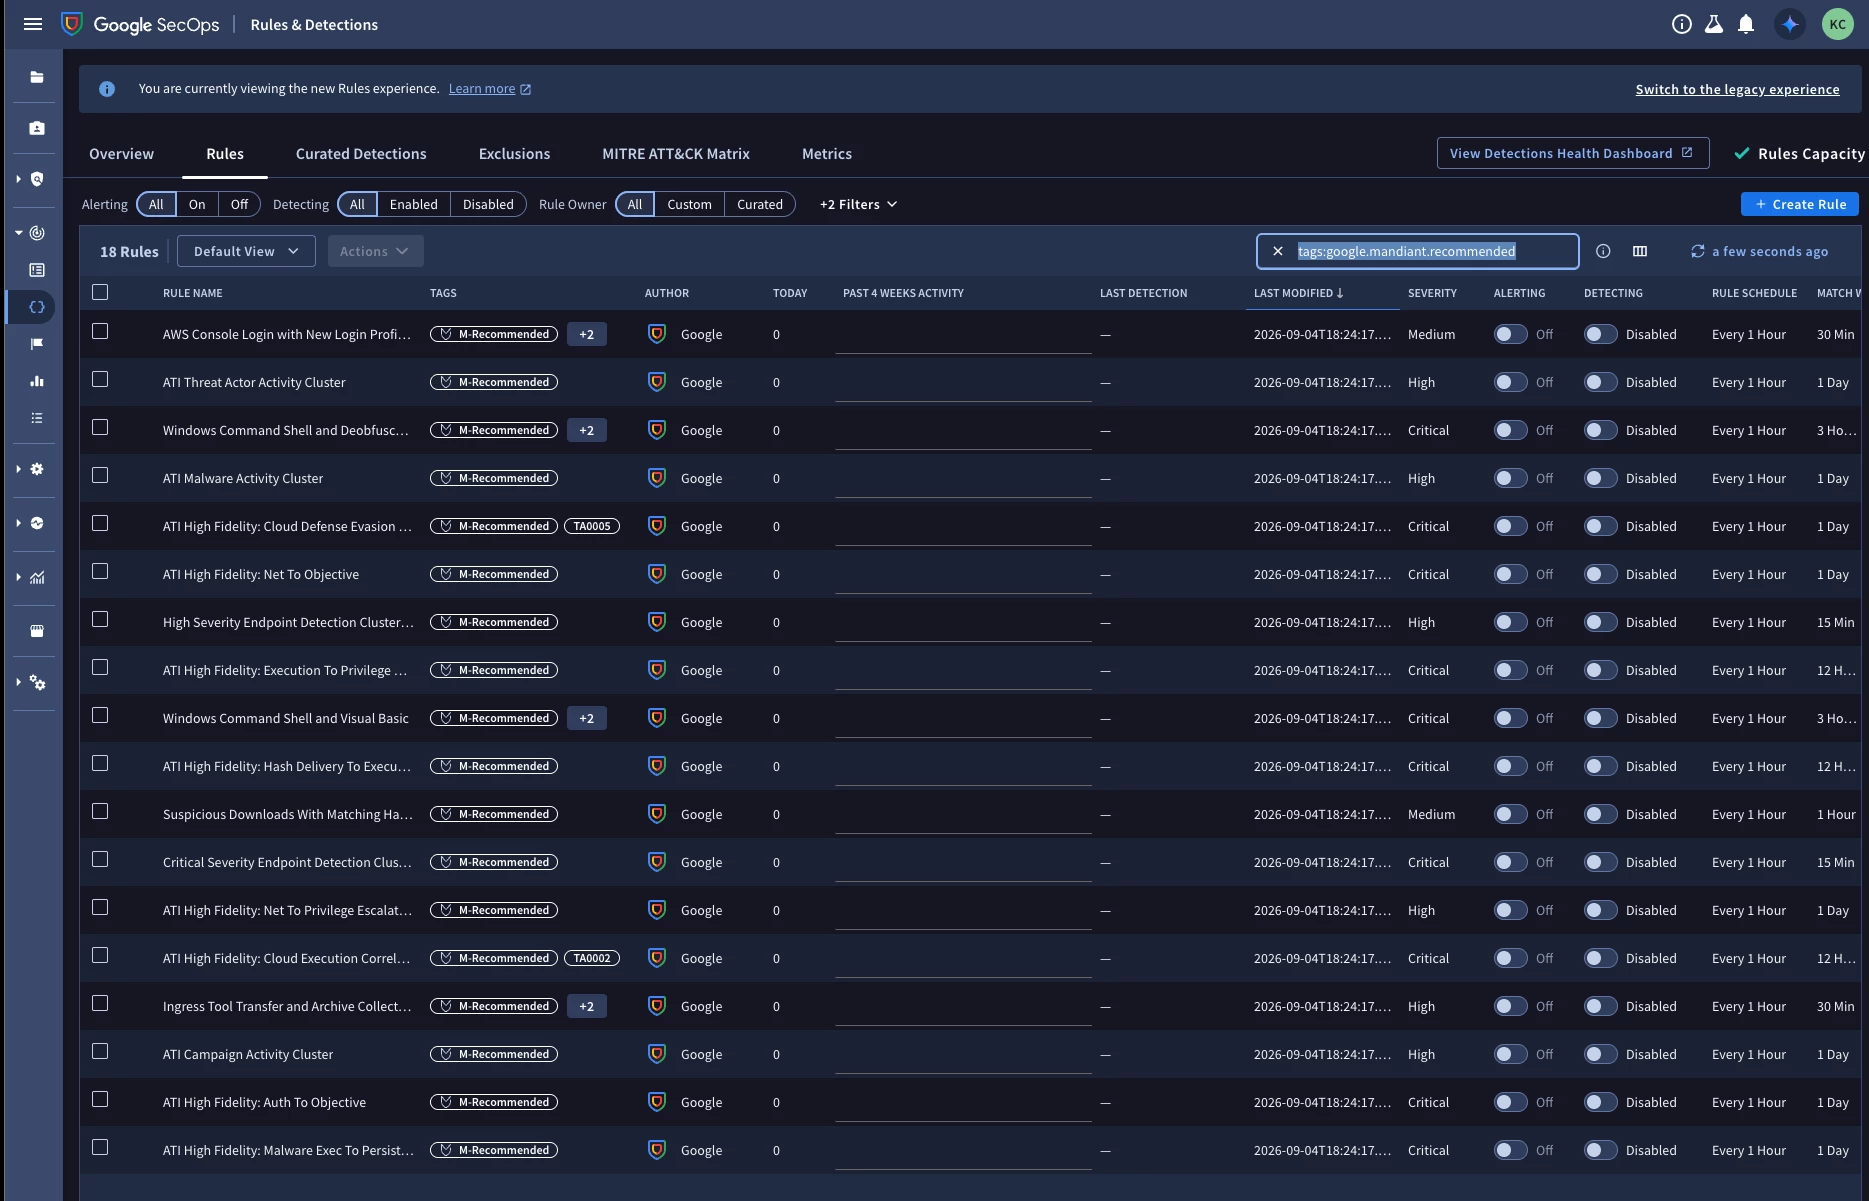
- Enable the Tag Subscription: Select the checkbox next to any rule in the list, click the Actions dropdown menu, and select Assign Tags > Manage Tags. This opens the Manage Tags drawer on the right rail, where you will see the M-Recommended tag (Author: Google) and can toggle Subscription is on for this tag to automatically enable and synchronize the baseline. (Tip: You can also view and toggle tag subscriptions from Rules & Detections > Overview by clicking Manage tag subscriptions in the Mandiant Recommended Rules widget).
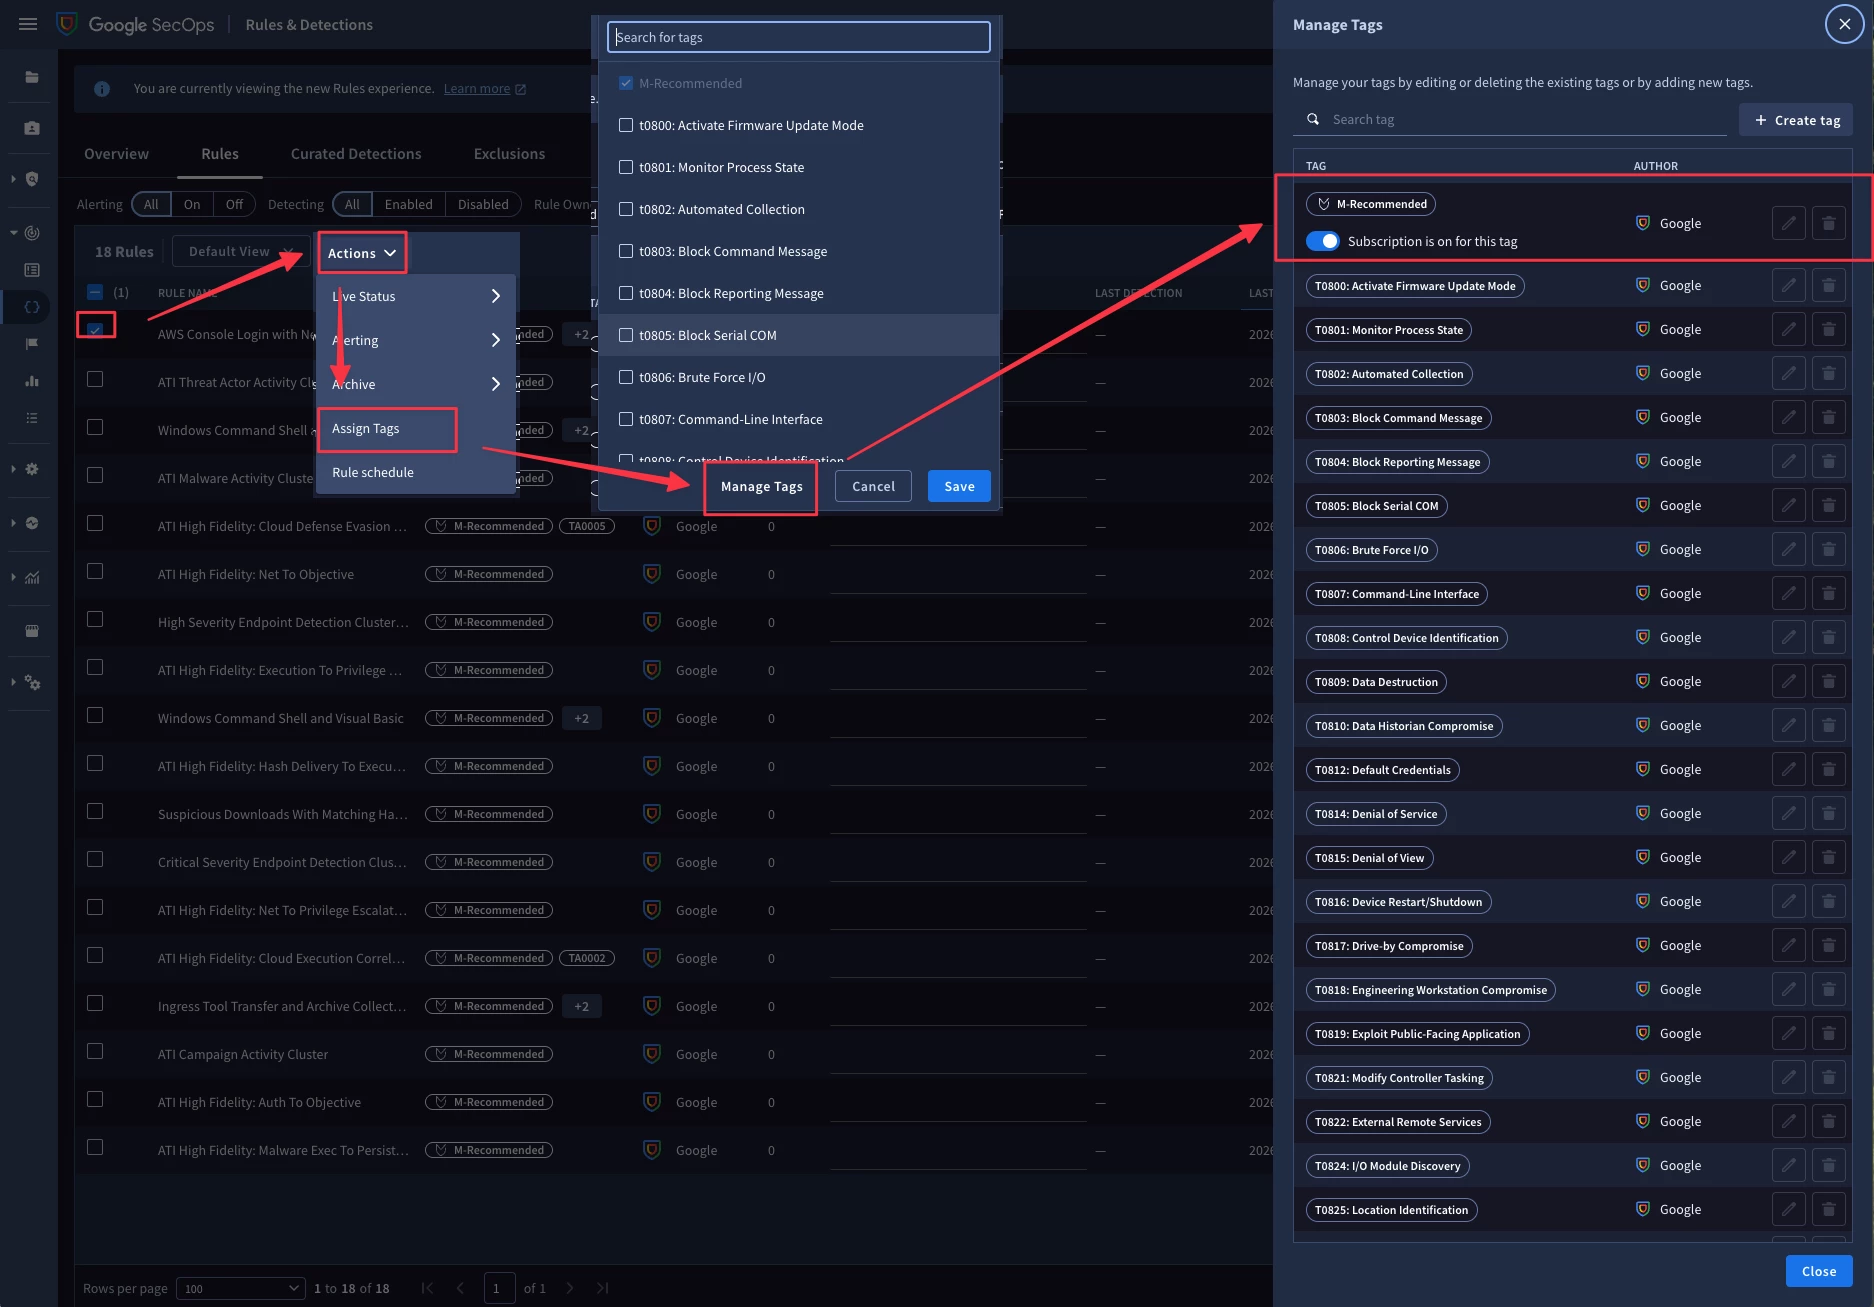
(Note: Ensure your role includes the chronicle.tagSubscriptions.* IAM permissions—such as chronicle.tagSubscriptions.list, chronicle.tagSubscriptions.get, chronicle.tagSubscriptions.create, and chronicle.tagSubscriptions.update—required to view and modify tag subscriptions).
Resources & Documentation
We look forward to partnering with you to build the next generation of high-precision, low-toil threat detection in Google Security Operations!
