
Hello SecOps Community!
We wanted to send out a quick post to y’all highlighting some SecOps curated content relevant to PHP2SHELL disclosures on 2026.10.21. In addition to an excellent writeup by our colleagues at Wiz (which you should check out here: https://www.wiz.io/blog/php2shell-php-rce), we did a long form writeup on the Google Cloud blog, which alluded to a set of new curated detections, but didn’t provide direct guidance on how to find them:
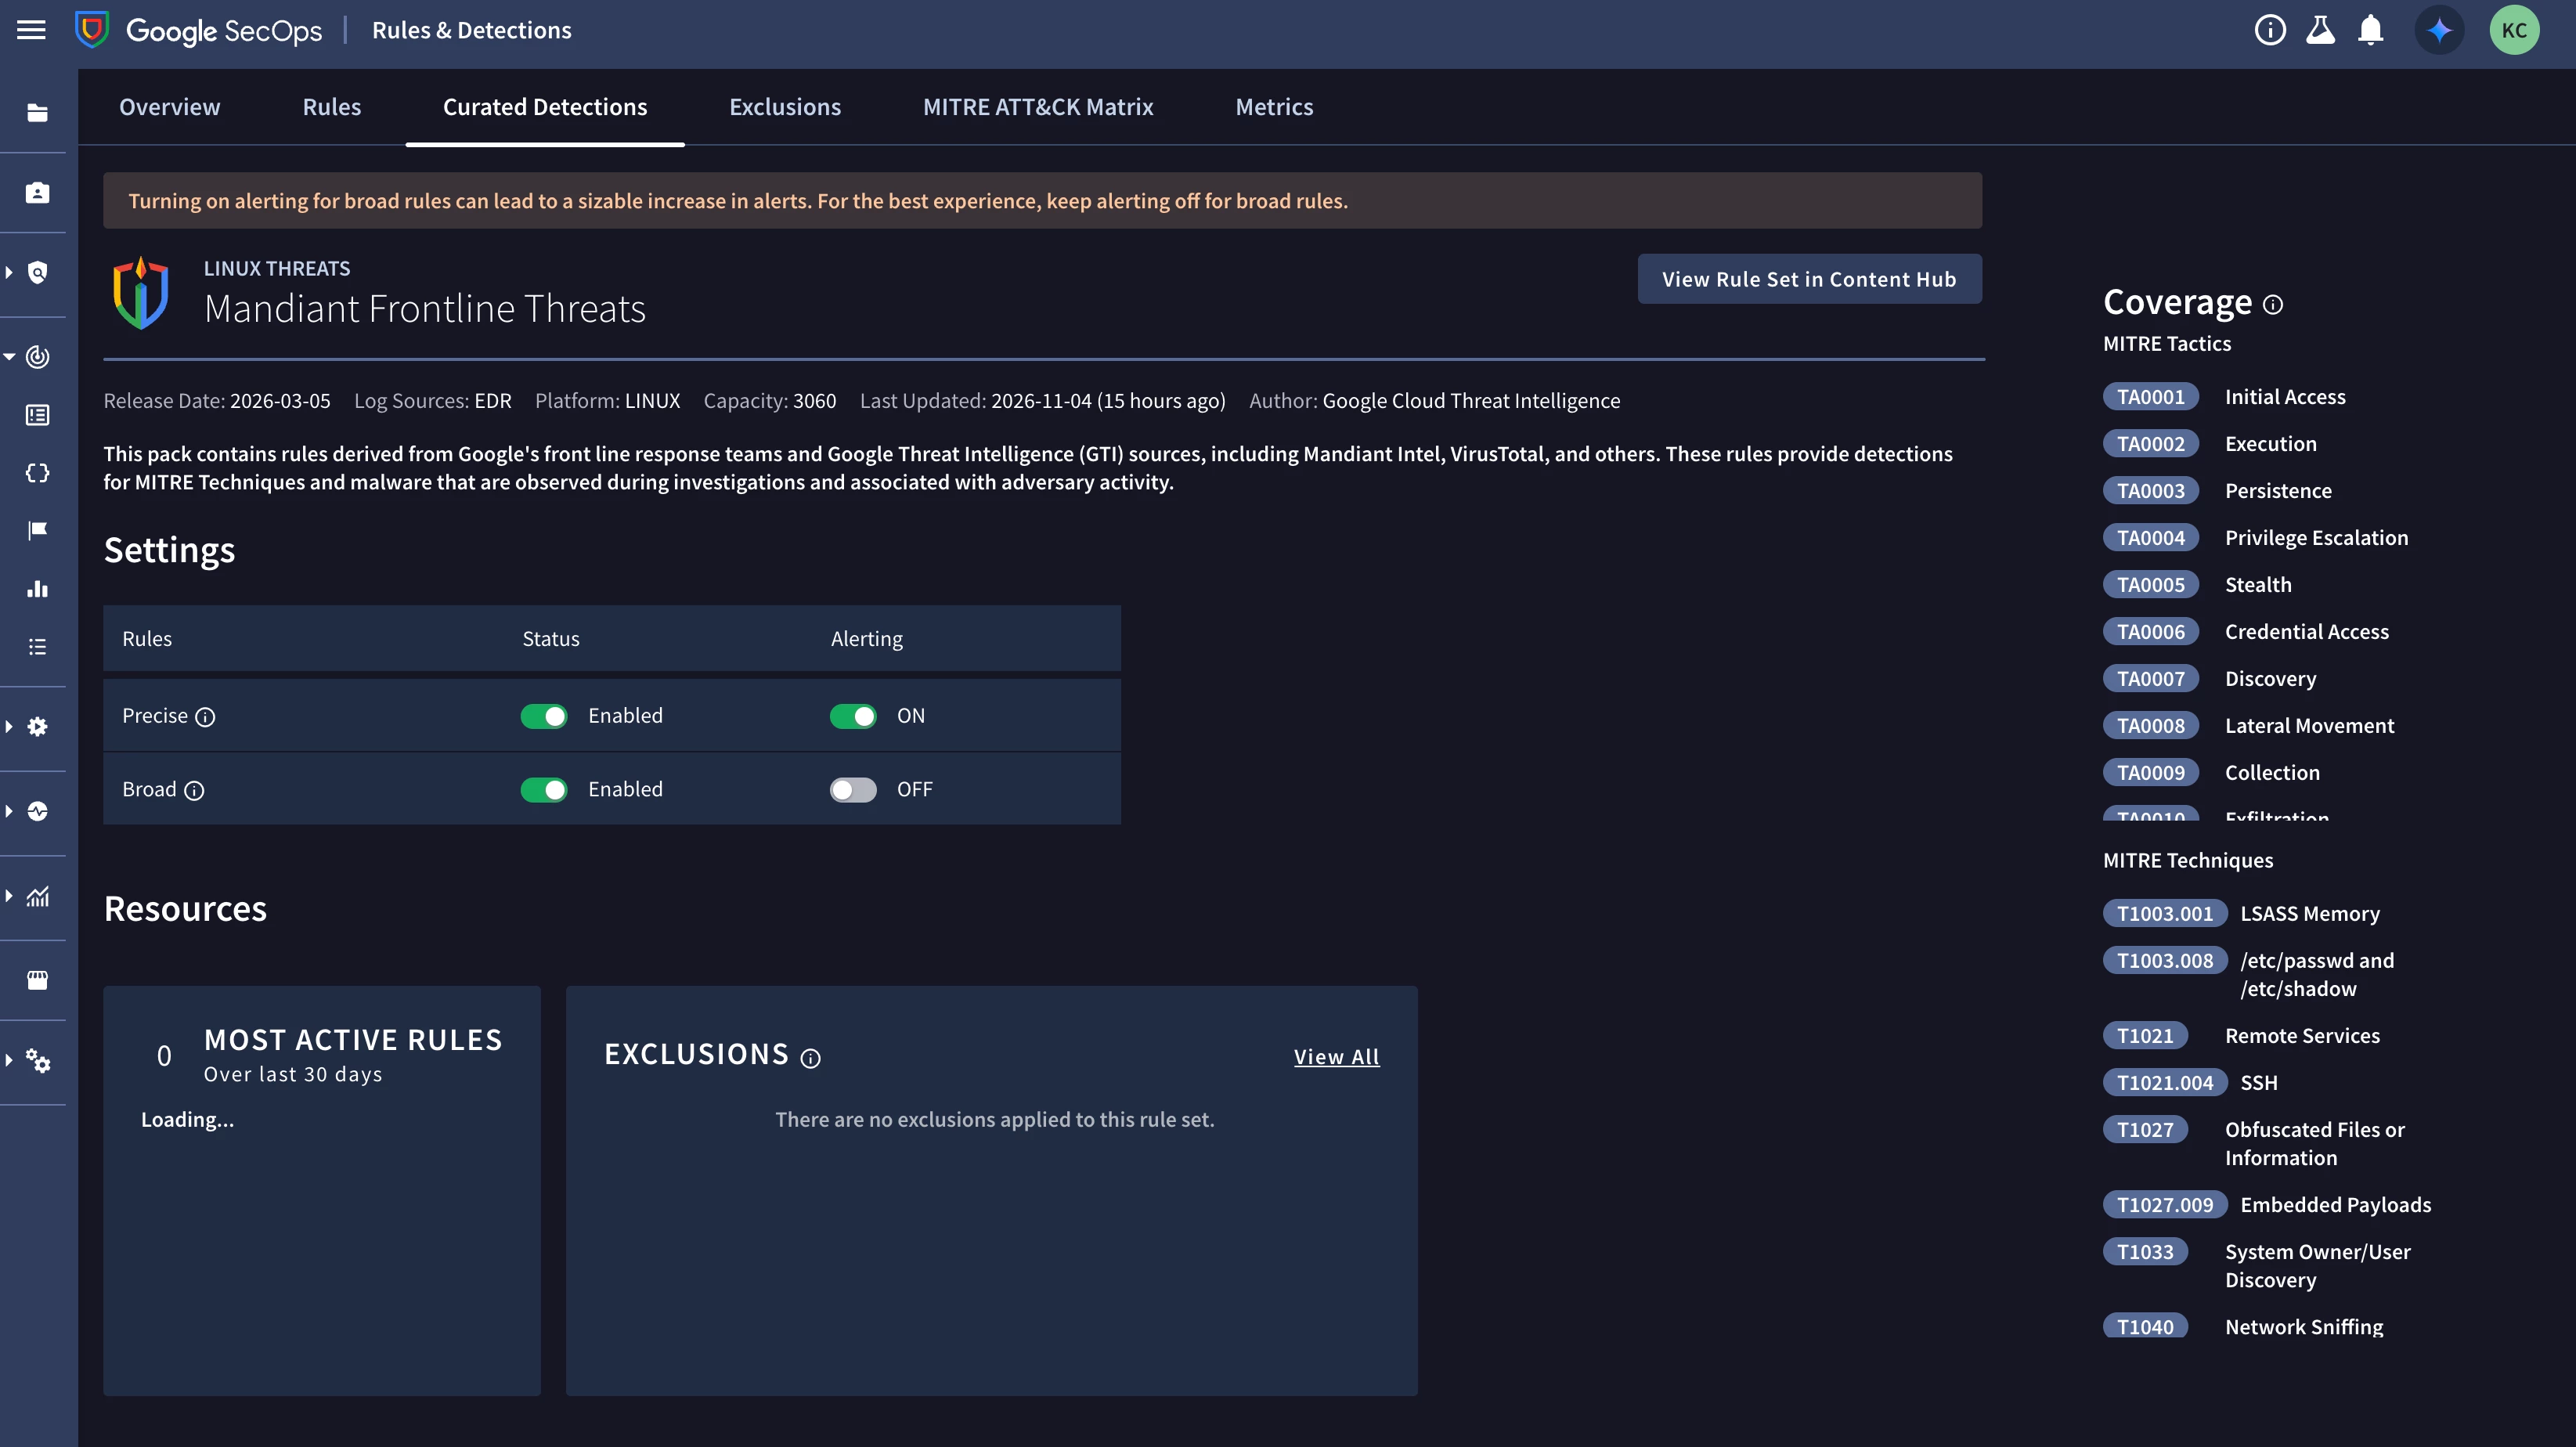
>Google Security Operations now has 23 new curated detections added to the Mandiant Frontline Threats rule pack. We recommend verifying that this rule pack is enabled and reviewing your detections to assess any potential impact to your environment.
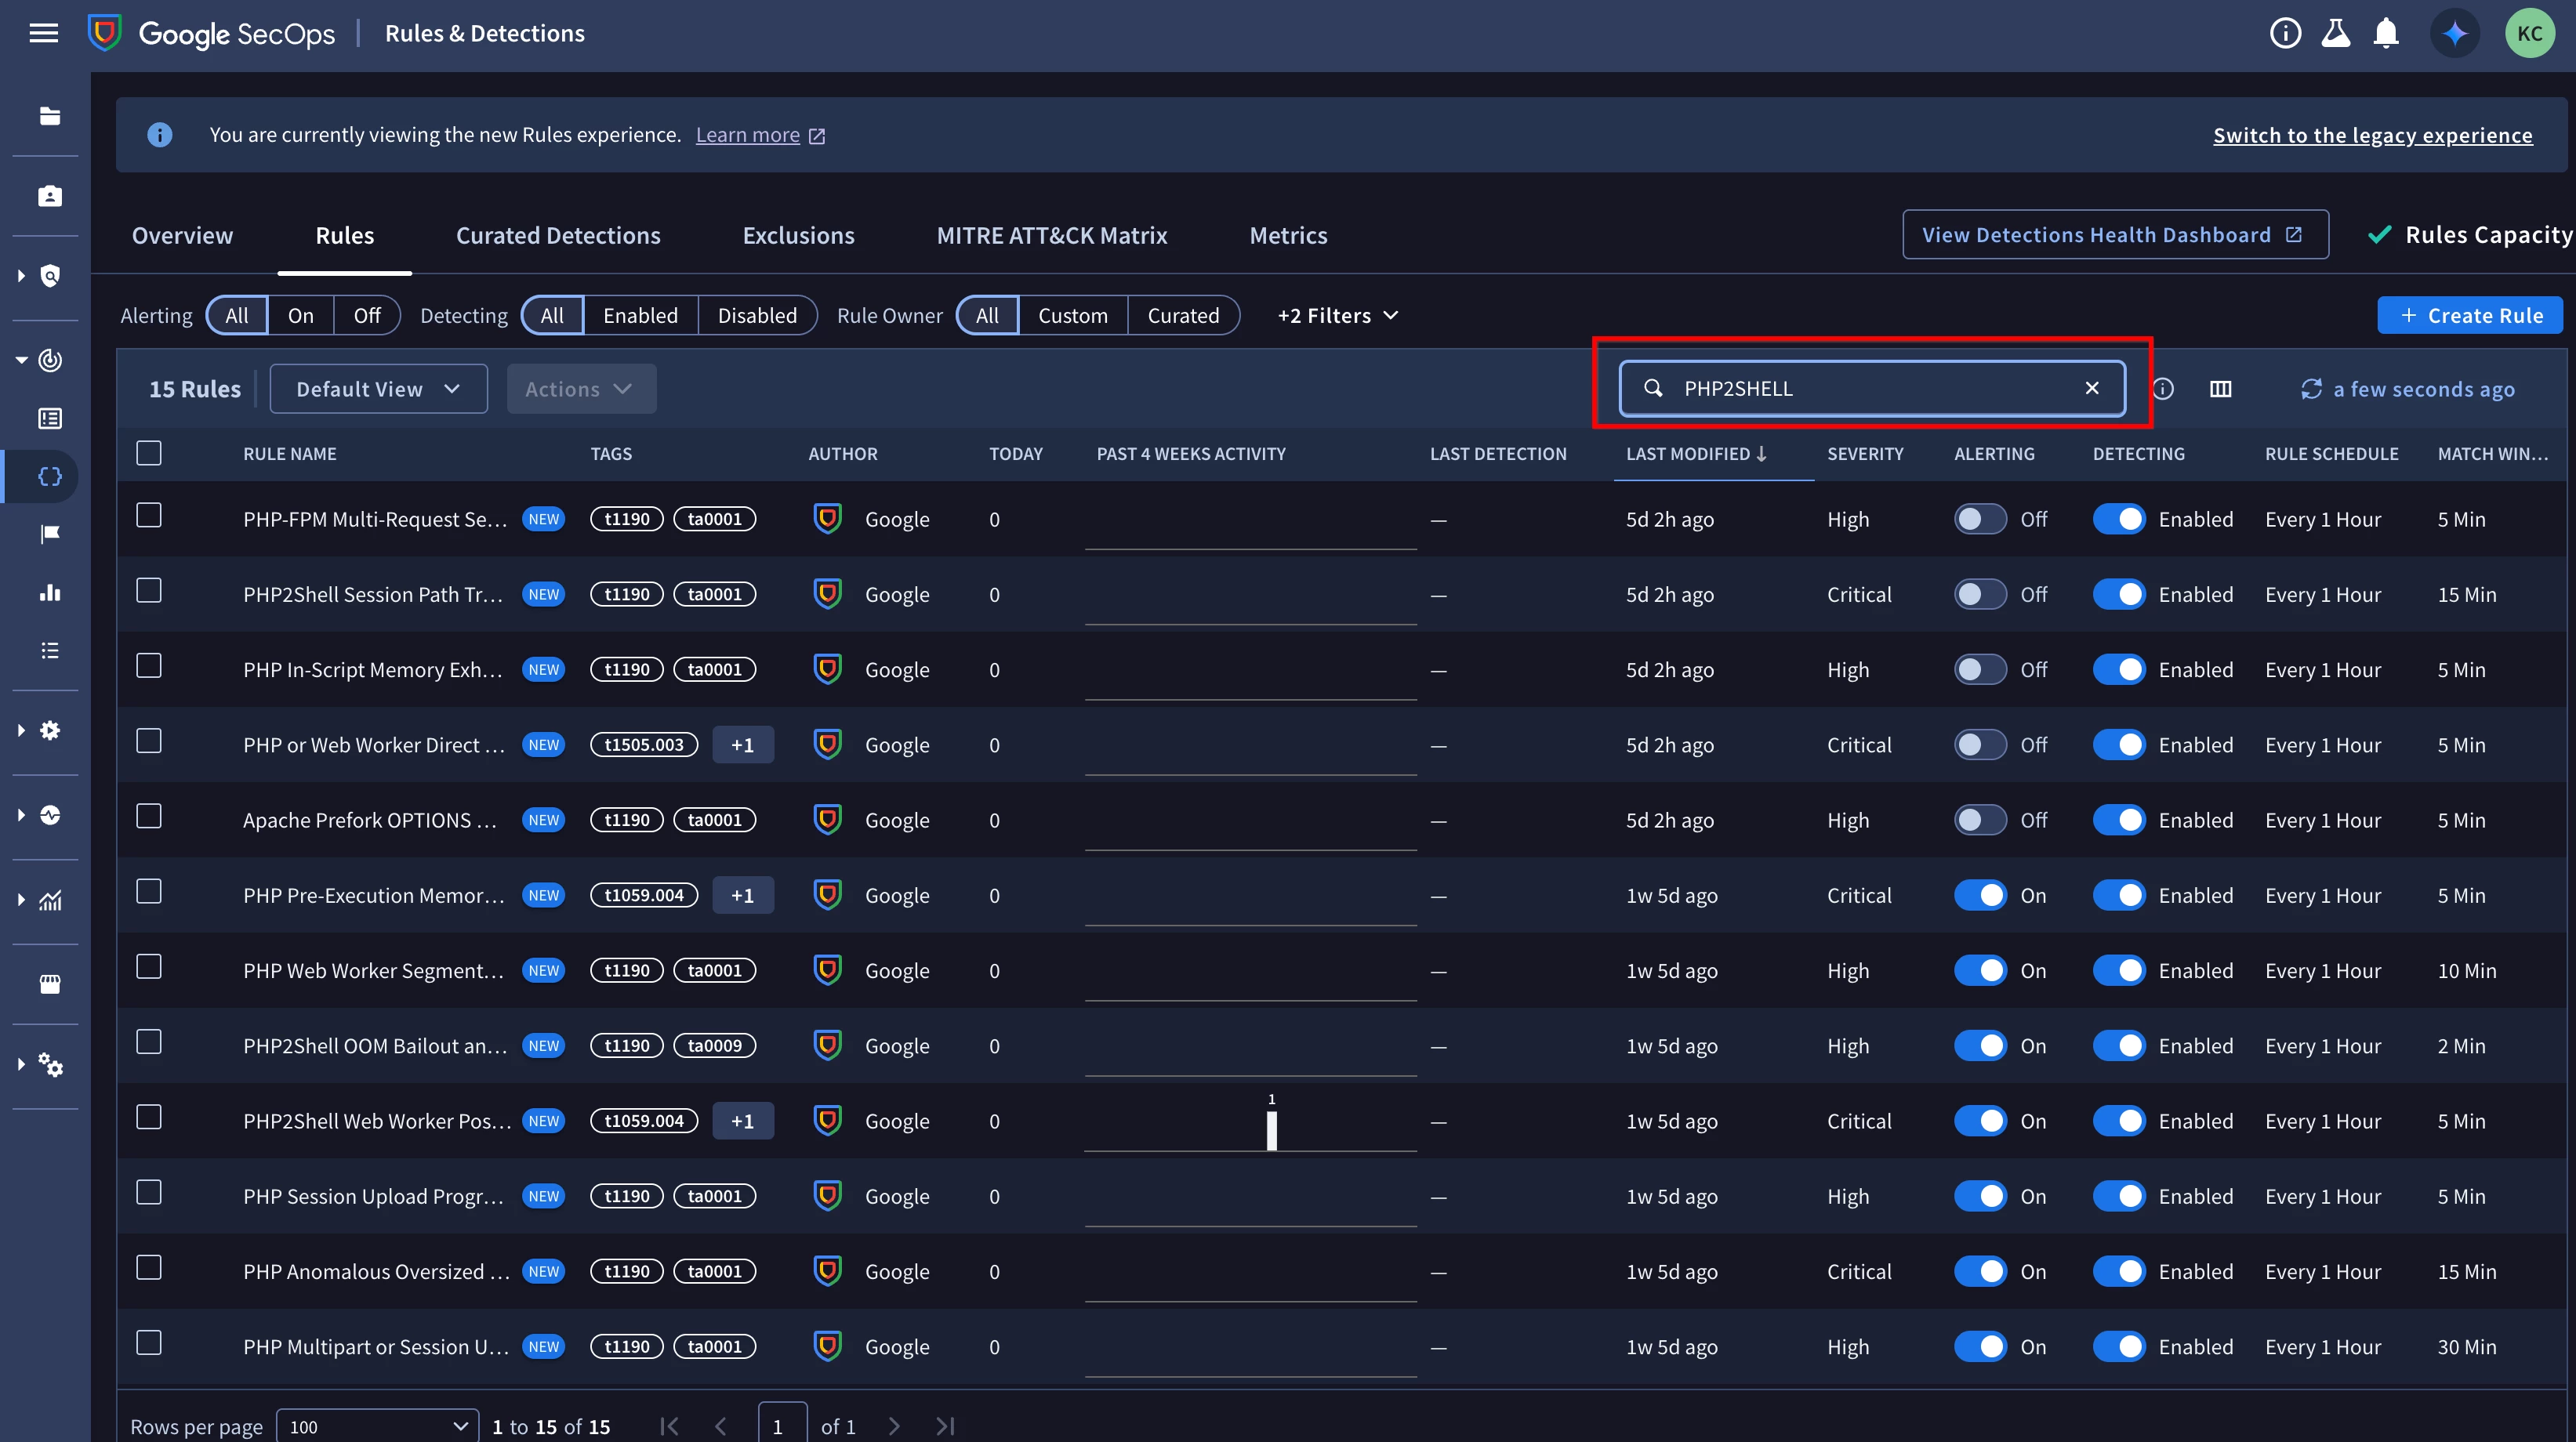
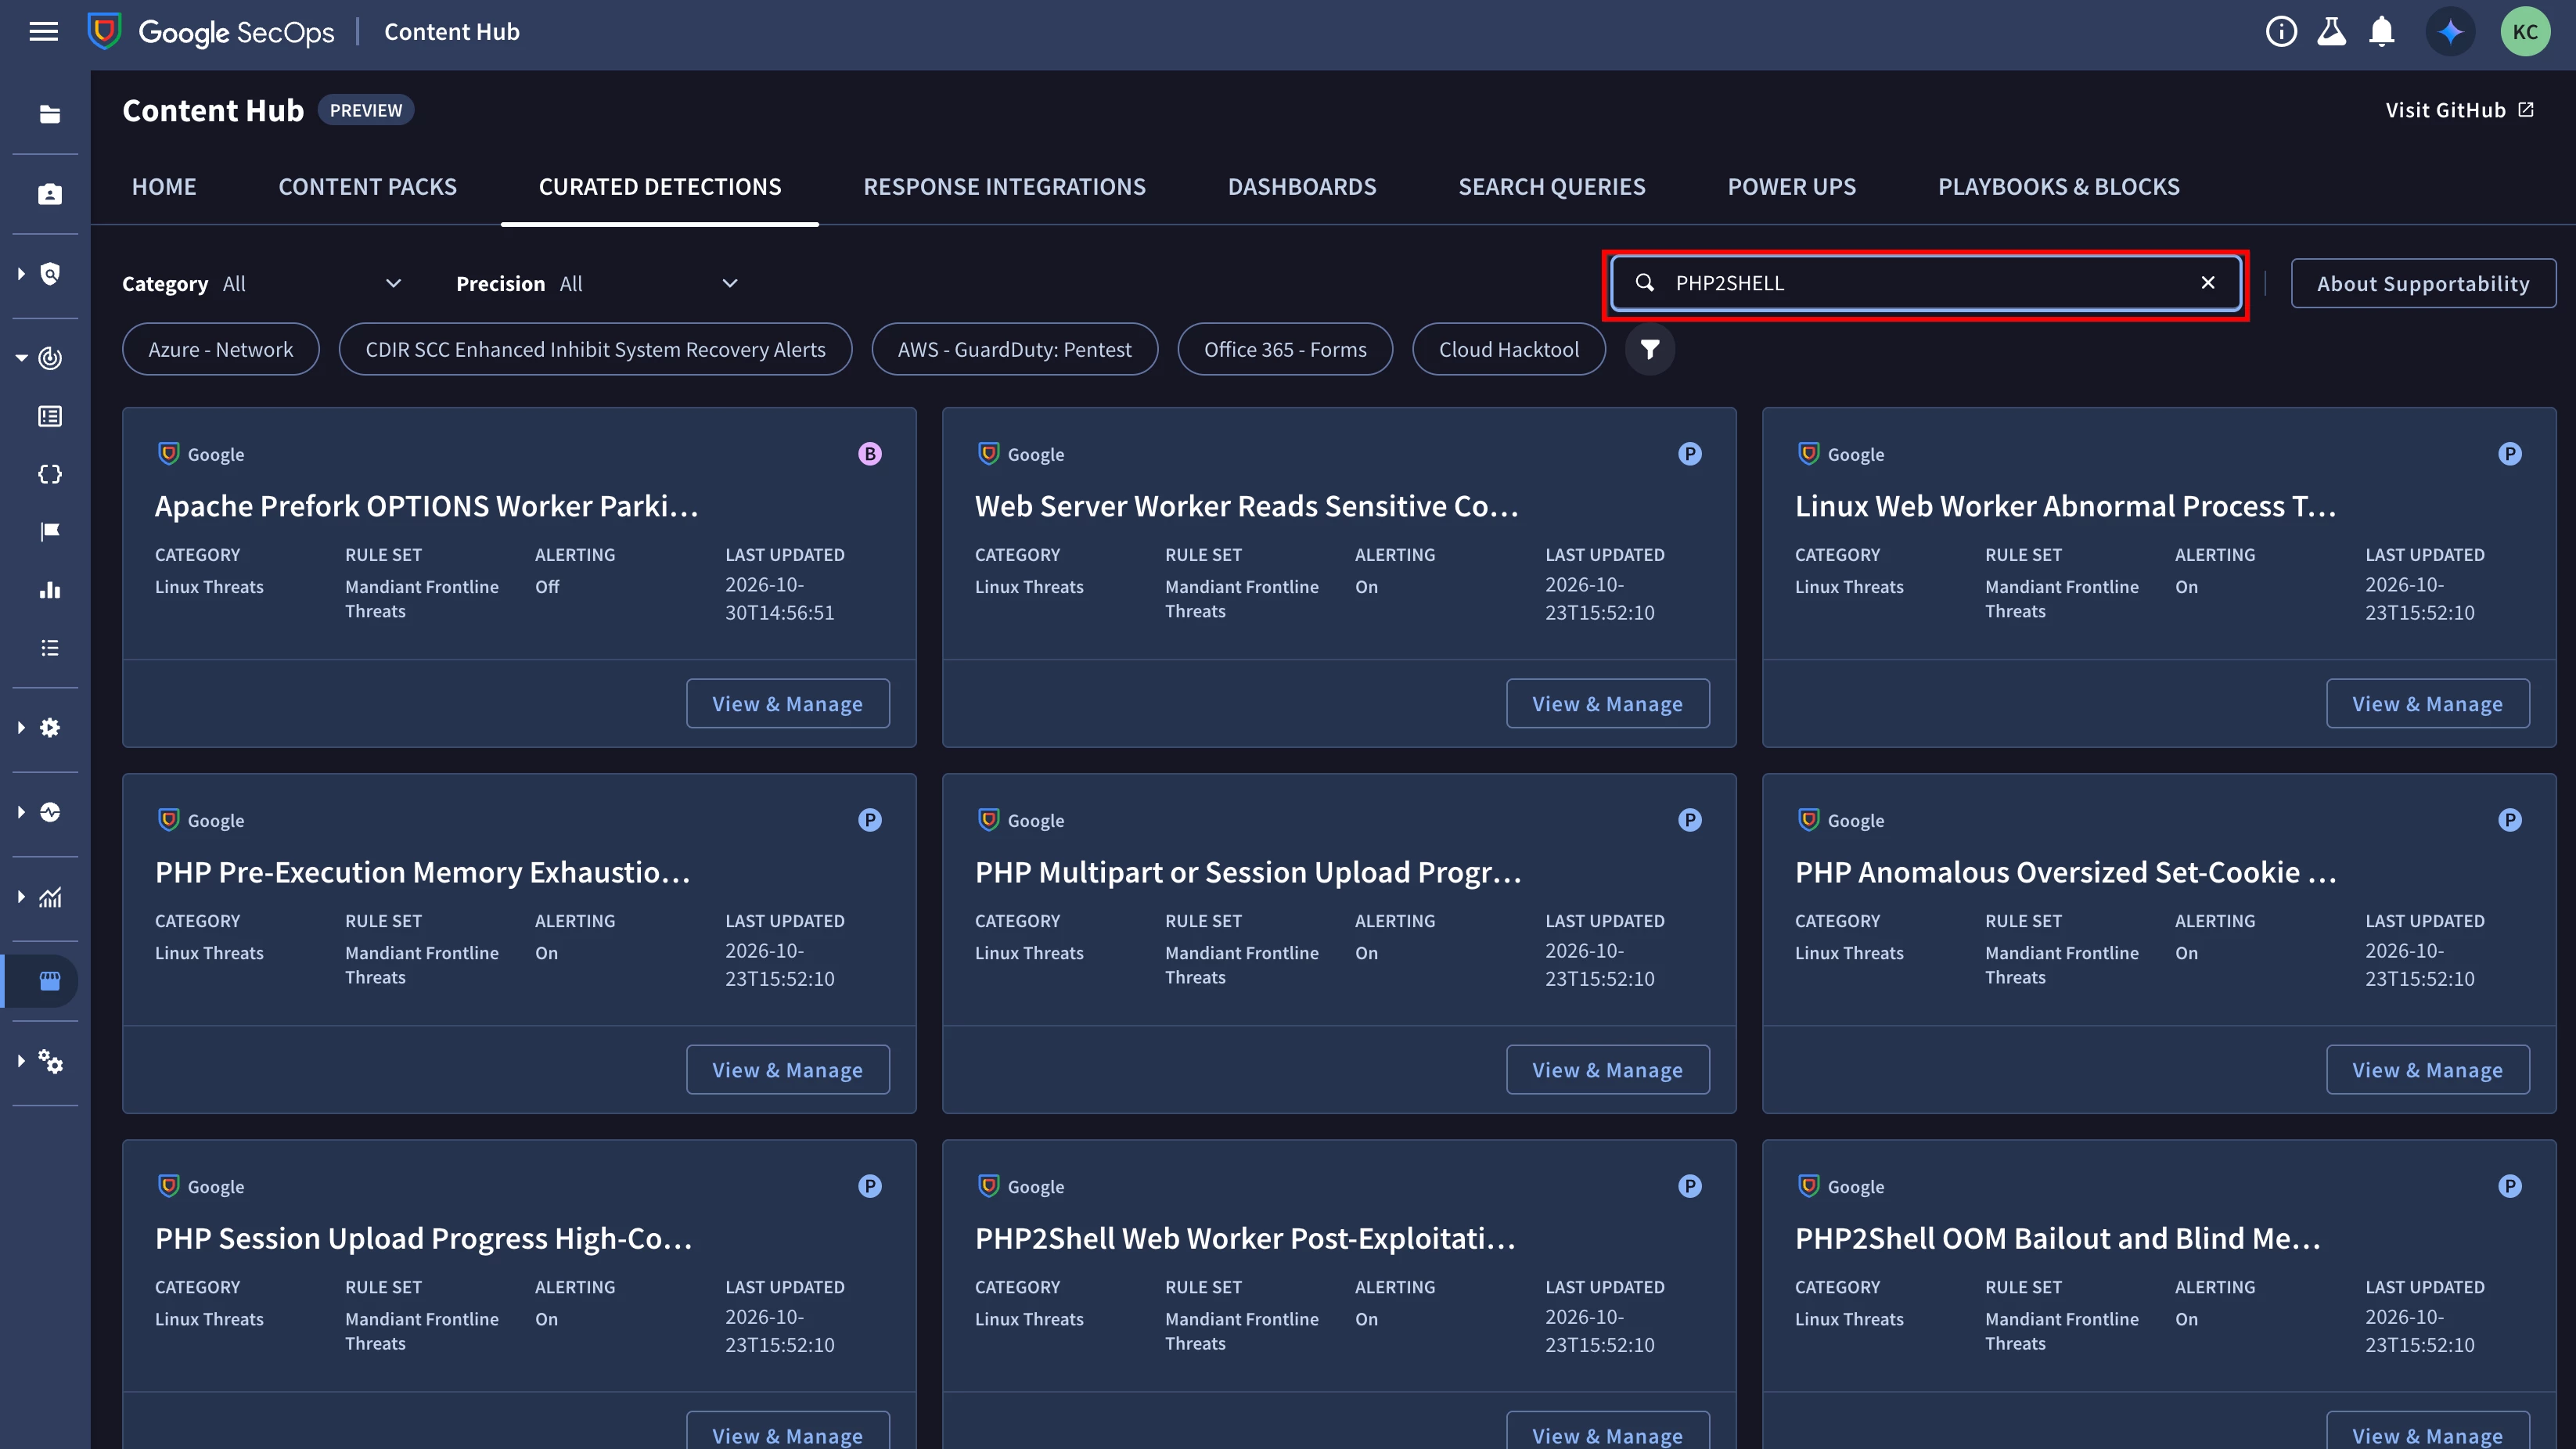
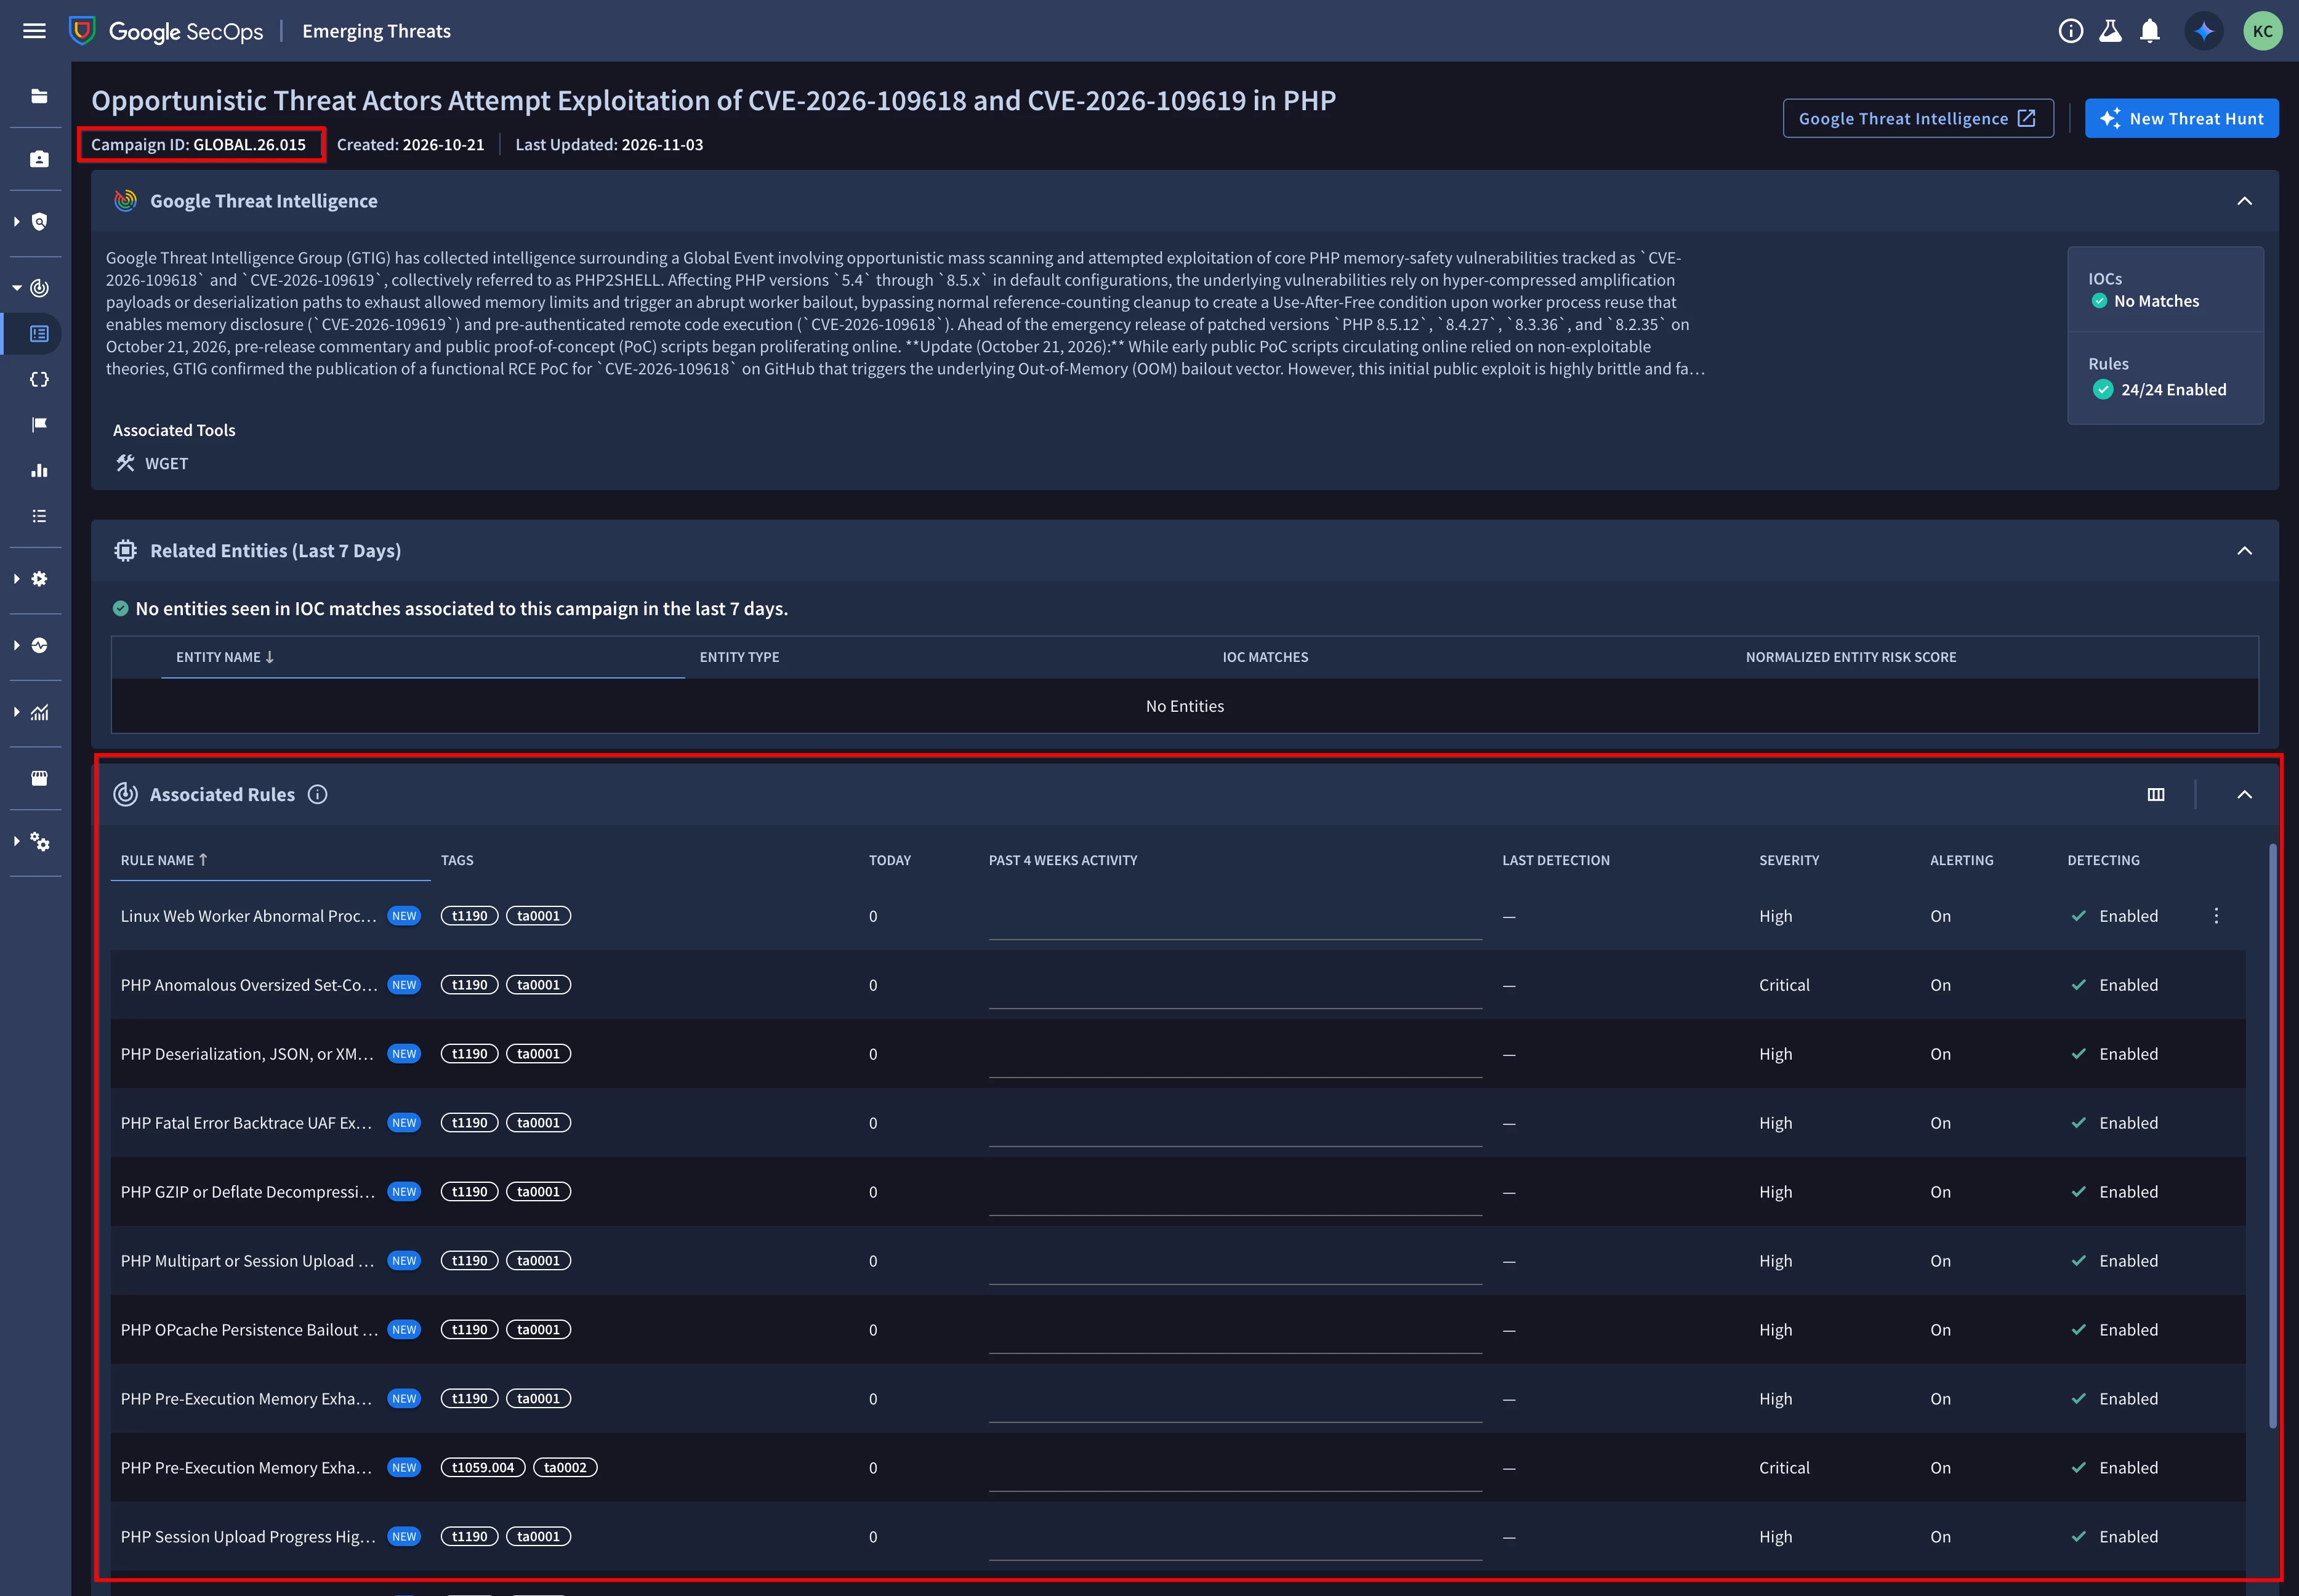
If you are so inclined, we bundled these rules up into the Pack “Mandiant Frontline Threats”, and you can also use the new Unified Rules search feature as well as the search feature in Content Hub to review and deploy them as you see fit. If you are an E+ customer, you can also use the Emerging Threats Center to look up the the GTI campaign GLOBAL.26.015 and the associated rules.
Rule Pack:
Unified Rules:
Content Hub:
Emerging Threats Center (E+ only customers):
(Bonus - you can turn this into an active threat hunt as well using the “New Threat Hunt” button in the top right)
Lastly, we also published a new rule related to a tampered copy of the Claude Code extension for Cursor - you can search for the rule name “Trojanized Anthropic Claude Code Extension Supply-Chain Compromise Artifacts” / “ttp_claude_code_extension_supply_chain_compromise”.
Good luck and happy hunting!
-Kyle & the SecOps Team
