Solved

Curated rules with detecting OFF and alerting ON

  • September 3, 2026
  • 6 replies
  • 107 views

ar3diu
Forum|alt.badge.img+11

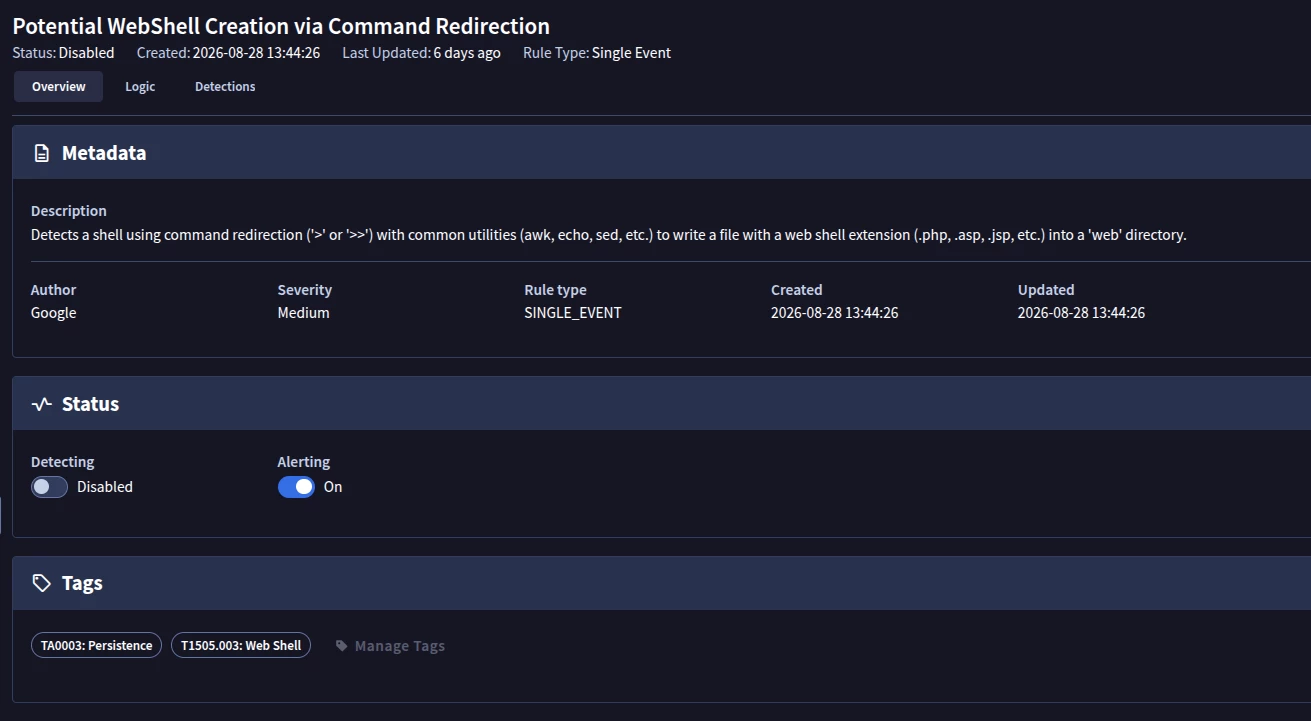
I noticed that some of the new curated rules land with detecting (status) disabled and alerting enabled.
I was wondering if this is a misconfiguration or if alerting will continue to work even though detecting (whose field name in the API calls is actually status) is disabled.
 

Best answer by cmorris

New rules in a pack should respect the pack’s setting. If you are not seeing that, it may be a bug with the release of this rule. Leaving a rule set to alerting with detections set to disabled does have a use case for retrohunts (rule can be run manually over set range and will still create alerts without running against live data), but that would be applicable to custom rather than curated detections.

View original

6 replies

cmorris
Staff
Forum|alt.badge.img+17
  • Staff
  • September 3, 2026

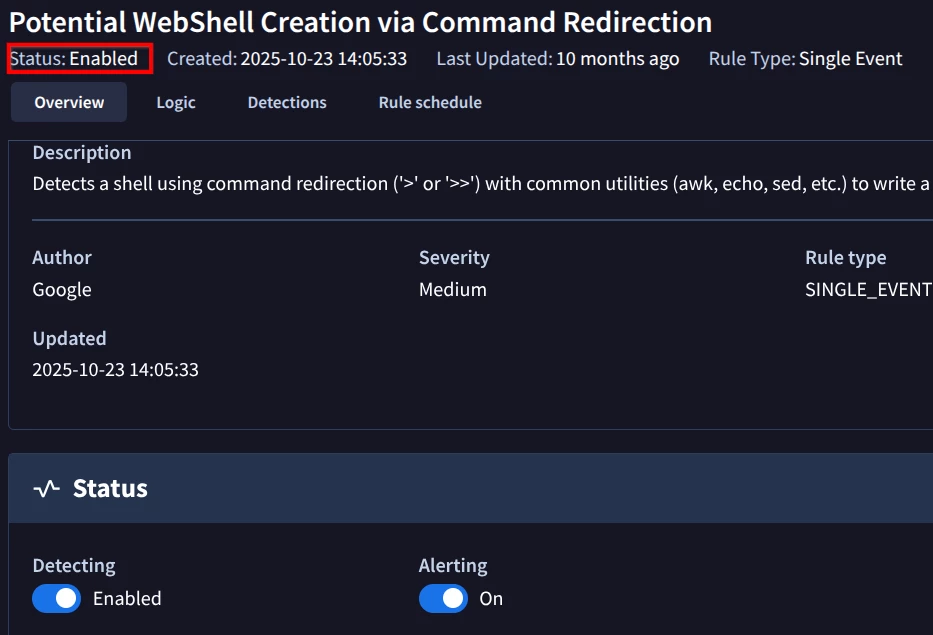
You would want to enable ‘Detecting’. The rule shows a status of Disabled at the top. After enabling the detecting piece, it will show Enabled


ar3diu
Forum|alt.badge.img+11
  • Author
  • Silver 2
  • September 4, 2026

Thanks ​@cmorris . The problem I was trying to highlight is that these rules come with this exact setting by default. I was only able to identify this through a DaC process. You shouldn’t be able to turn ON alerting on a rule if detecting (status) is OFF.


cmorris
Staff
Forum|alt.badge.img+17
  • Staff
  • Answer
  • September 4, 2026

New rules in a pack should respect the pack’s setting. If you are not seeing that, it may be a bug with the release of this rule. Leaving a rule set to alerting with detections set to disabled does have a use case for retrohunts (rule can be run manually over set range and will still create alerts without running against live data), but that would be applicable to custom rather than curated detections.


ar3diu
Forum|alt.badge.img+11
  • Author
  • Silver 2
  • September 4, 2026

Okay, thanks for your answers, ​@cmorris . In this case, the rules did not follow the rule set deployment state. This happened at the same time across multiple SecOps instances, which makes me think it’s the way they were deployed by Google. I’ll try to keep an eye on this, and if I see it again, I’ll update this post.


ar3diu
Forum|alt.badge.img+11
  • Author
  • Silver 2
  • September 10, 2026

​@cmorris I’m back with a fresh example.

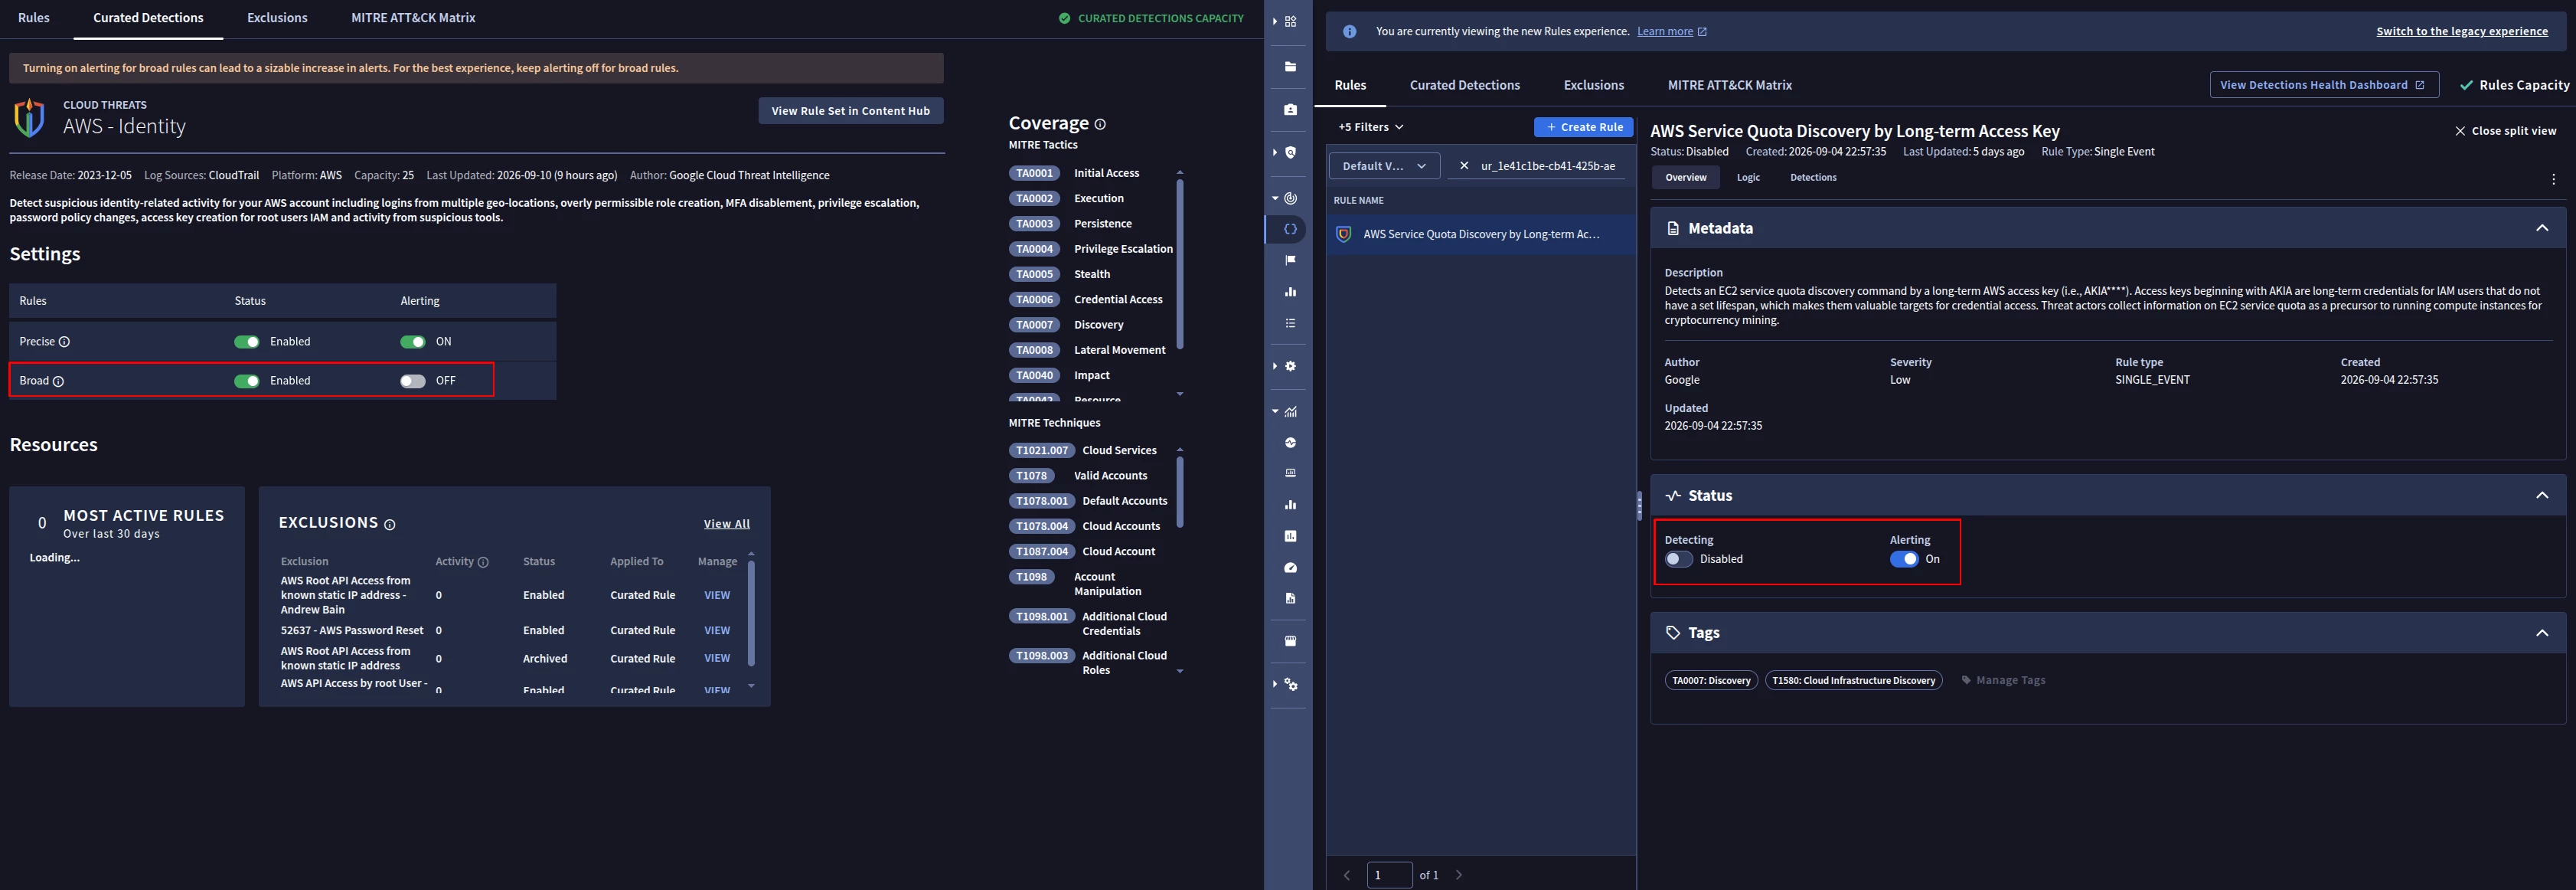
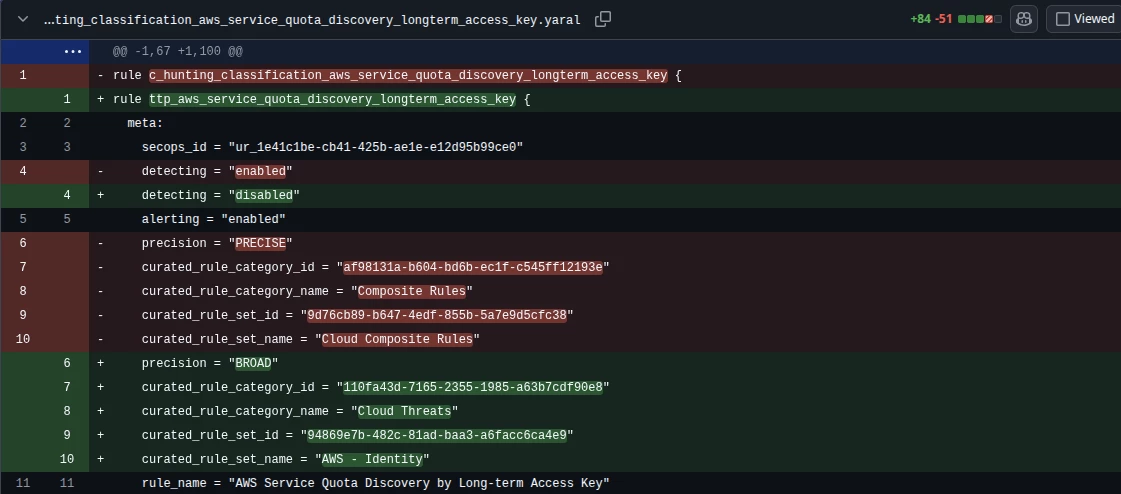
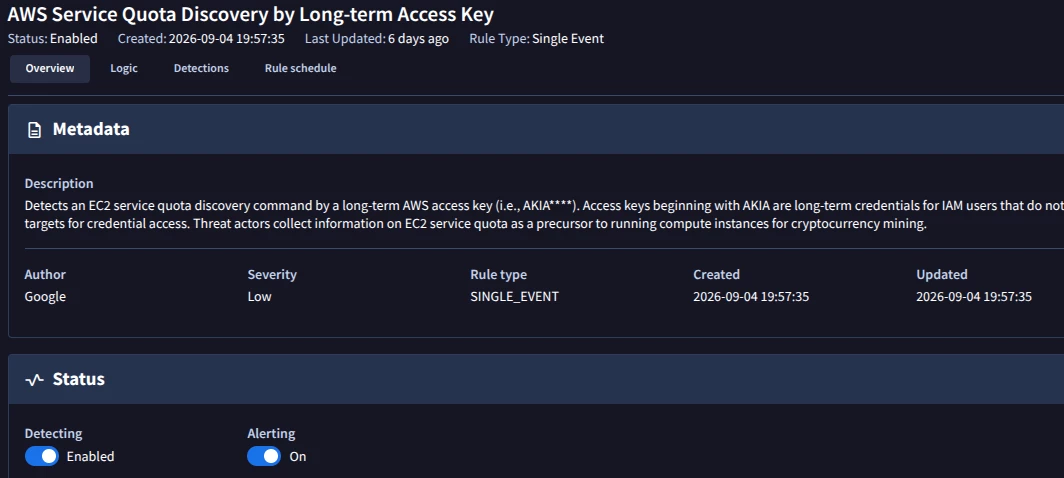
This curated rule was updated today by Google. The curated rule set (Cloud Composite Rules > AWS - Identity) and the rule precision changed from PRECISE to BROAD. The deployment state was updated from "detecting = enabled AND alerting = enabled" to "detecting = disabled AND alerting = enabled" when the curated rule set it is part of (as well as the one it was in before) has a different configuration. Something isn't right.


cmorris
Staff
Forum|alt.badge.img+17
  • Staff
  • September 10, 2026

​@ar3diu - Not certain why the change is happening, the new rules is respecting the pack settings in my testing.

Could you open a case for further investigation?