

Hi everyone,
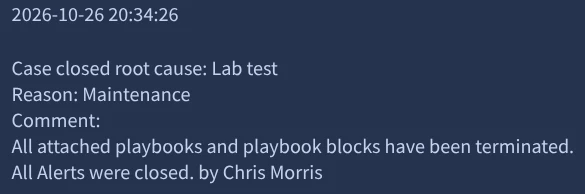
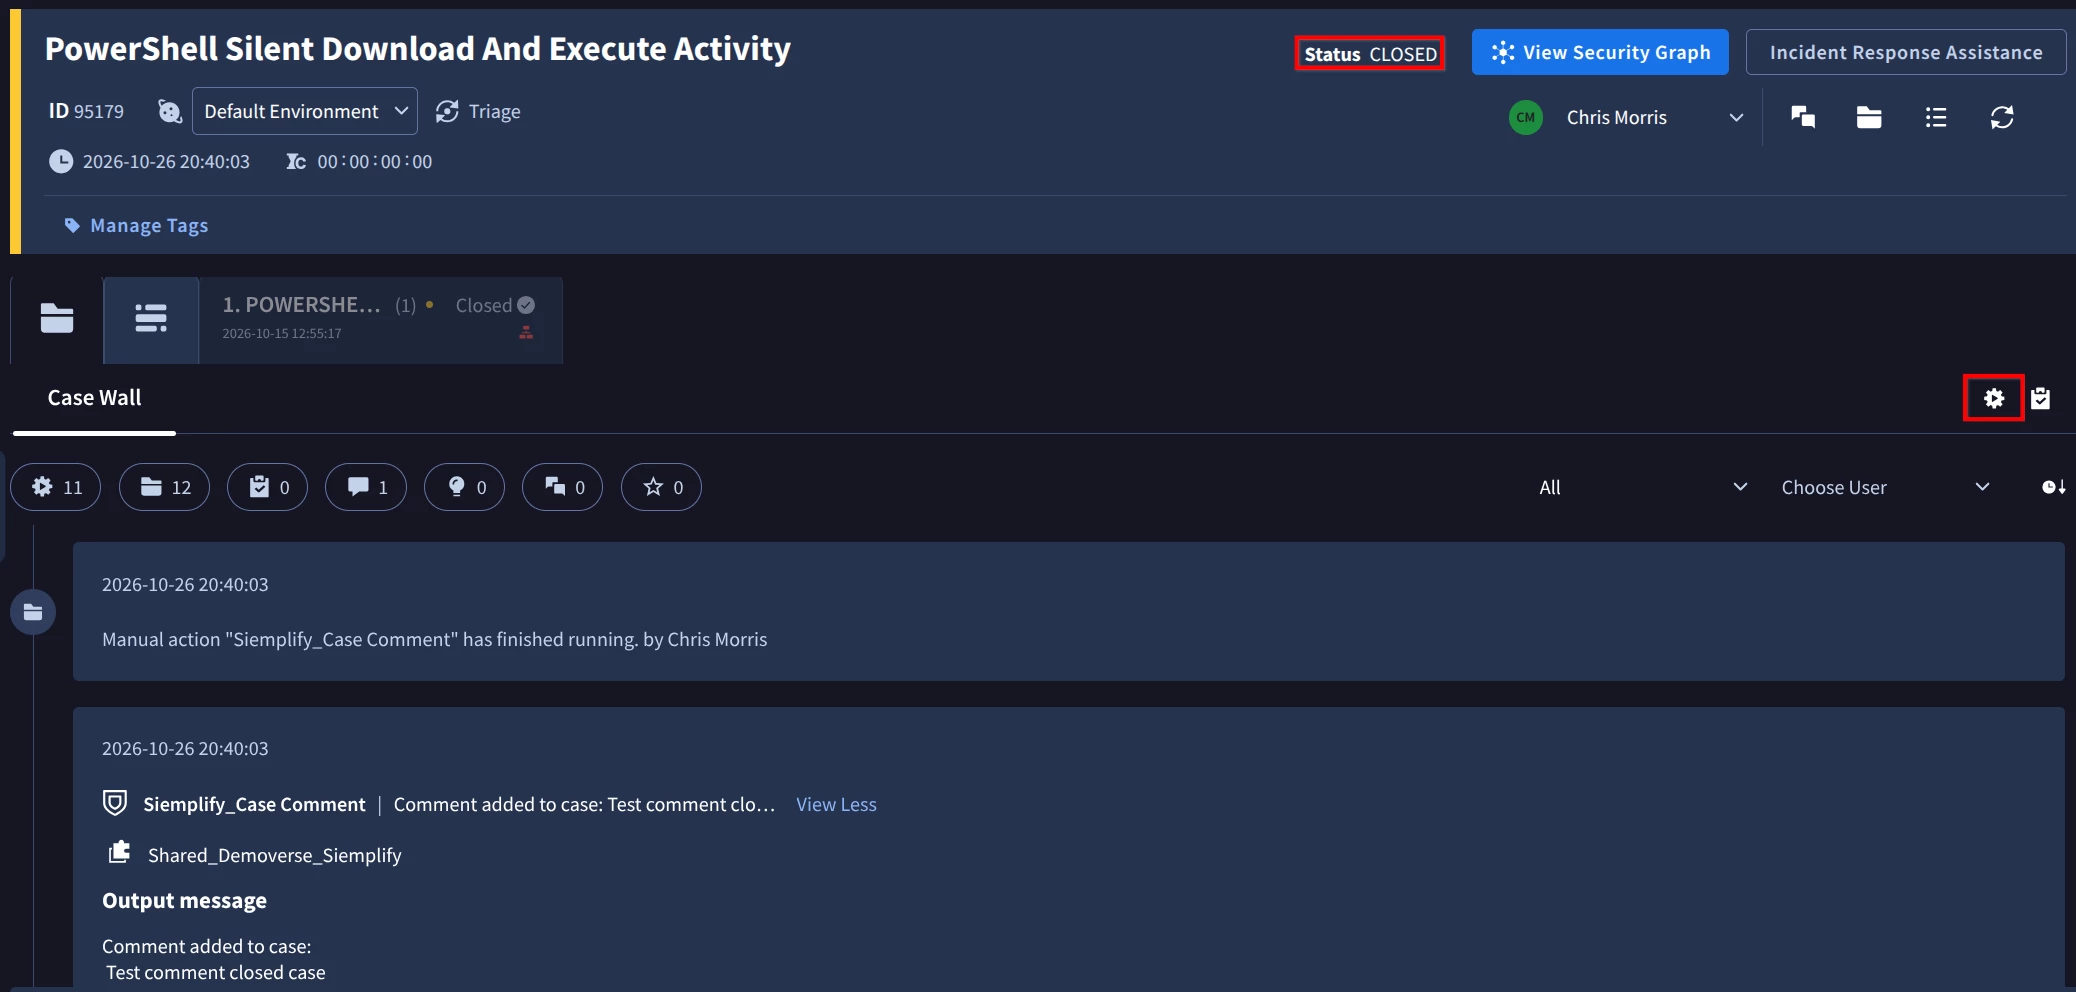
We are reviewing the behavior of the Close Case action in Google SecOps SOAR.
We would like to determine whether there are scenarios where an action can still run after another action has closed the case.
(this behavior could affect the SOC's SLA metrics)
I haven't found any official documentation clearly explaining the expected behavior.
Could someone help me to clarify these points?
- Does Close Case officially stop the entire playbook execution?
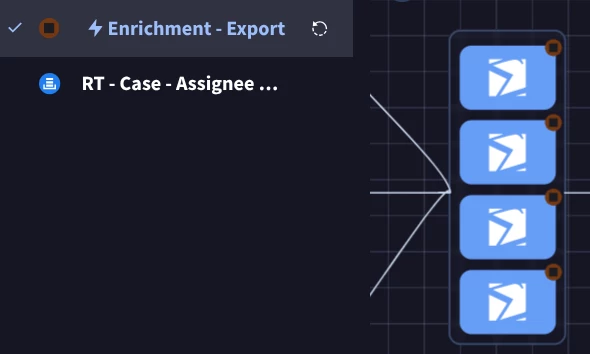
- If the action is executed inside a block, does it stop only the current block or also the parent playbook?
- What happens to asynchronous actions that started before the case was closed? Can they continue and complete afterward?
- What happens to parallel branches and pending or manual actions?
- Can a new action start after the case has been closed, or can only actions that were already running continue?
- Is the behavior consistent and reproducible, or can it vary depending on the action type and execution timing?
Finally, what is the recommended design pattern?
Should the Close Case action always be managed by the parent playbook and placed outside reusable blocks? For example, should a block return an outcome to the parent playbook and let the parent decide whether to close the case?
Many tank you for your help!!!