Solved

Explanation of Passthrough Rules

  • Mar 10, 2026 6:10 AM UTC
  • 3 replies
  • 116 views

0xM4XDF1R
Forum|alt.badge.img+4

Hi! 

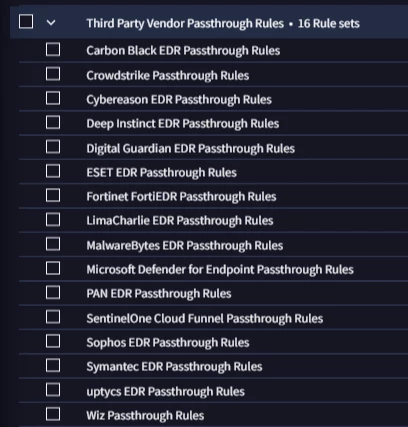
In the curated detection section in SecOps, there is something called Third Party Vendor Passthrough Rules. Does anyone know what they are?



Best answer by cmorris

Exactly. Rather than looking for a behavior, the events section of the detection will look for a log type and a severity and trigger based off of that and pass along additional context through the outcome section. No bi-directional sync through the Curated Detections as that is just taking the log and surfacing it. The SOAR integration for the technology may have options to sync or to update.

View original

3 replies

cmorris
Staff
Forum|alt.badge.img+17
  • Staff
  • Mar 10, 2026 12:15 PM UTC

These are rules designed to take an alert from one of the included log types and surface it as an alert in SecOps - https://docs.cloud.google.com/chronicle/docs/detection/third-party-vendor-alerts-category


0xM4XDF1R
Forum|alt.badge.img+4
  • Author
  • Bronze 3
  • Mar 10, 2026 12:17 PM UTC

These are rules designed to take an alert from one of the included log types and surface it as an alert in SecOps - https://docs.cloud.google.com/chronicle/docs/detection/third-party-vendor-alerts-category

So alert forwarding per say? And ofc not any bi-directional alert status sync between products


cmorris
Staff
Forum|alt.badge.img+17
  • Staff
  • Answer
  • Mar 10, 2026 12:21 PM UTC

Exactly. Rather than looking for a behavior, the events section of the detection will look for a log type and a severity and trigger based off of that and pass along additional context through the outcome section. No bi-directional sync through the Curated Detections as that is just taking the log and surfacing it. The SOAR integration for the technology may have options to sync or to update.