Solved

SCCP Toxic Combination Findings in SOAR Cases

  • Oct 22, 2025 12:57 PM UTC
  • 8 replies
  • 183 views

ar3diu
Forum|alt.badge.img+11

For SCCE customers, there’s a a SOAR SCC Enterprise Response Integration that can be used for ingesting Toxic Combination findings and syncing their status. What should I use if I have SCCP and SecOps? I can’t find the SCC Enterprise integration on the Marketplace. I can’t also import it from another instance. 

A detection rule in SIEM would be the easiest way to go but it looks like a new log is written in SIEM every time the toxic combination finding is updated by SCC engine. 

Any suggestions?

Best answer by kentphelps

​@ar3diu Take a look at Google SecOps Response Integrations release notes

Google Security Command Center: Version 14.0

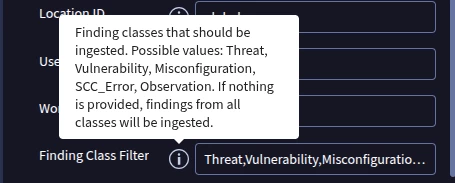
  • Added the ability to ingest Toxic Combinations and Chokepoints in the following connector:

    • Google Security Command Center - Findings Connector
View original

8 replies

kentphelps
Community Manager
Forum|alt.badge.img+12
  • Community Manager
  • Oct 24, 2025 3:56 PM UTC

ar3diu
Forum|alt.badge.img+11
  • Author
  • Silver 2
  • Oct 27, 2025 8:07 AM UTC

​@kentphelps But the Google Security Command Center doesn’t support collection of the Toxic Combination findings


kentphelps
Community Manager
Forum|alt.badge.img+12
  • Community Manager
  • Oct 27, 2025 2:38 PM UTC

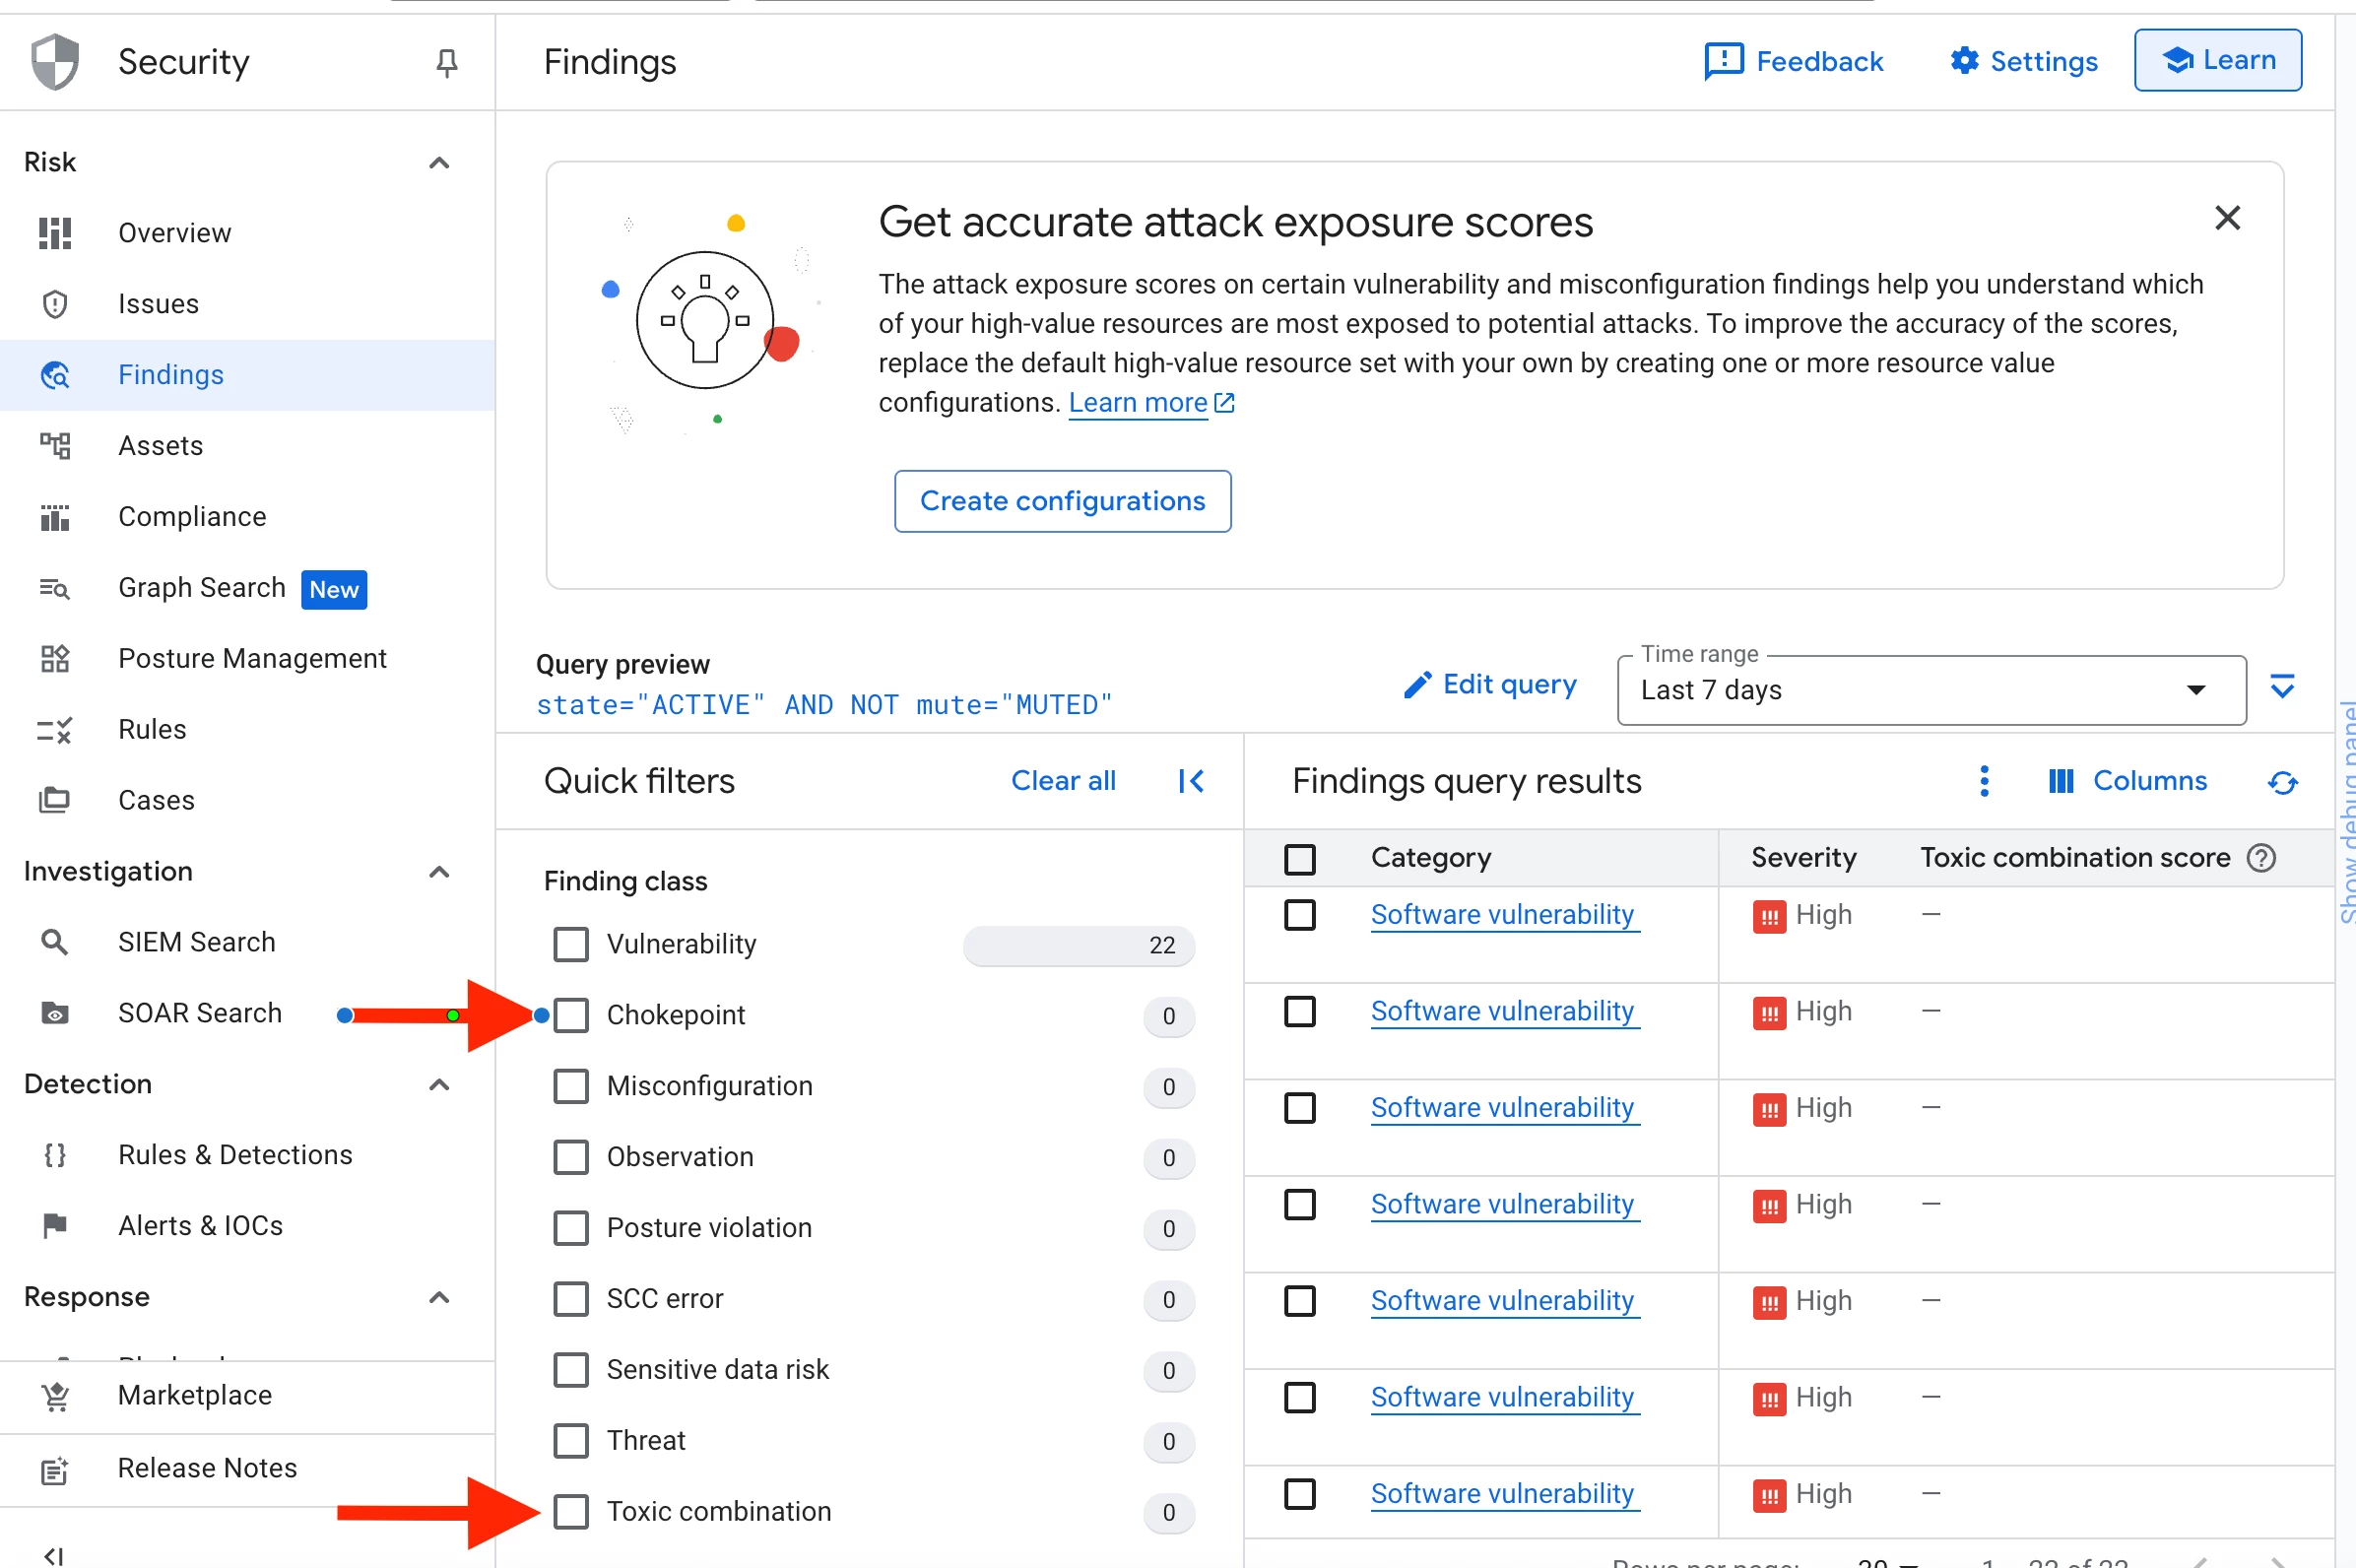
If you go under Findings do you see Toxic Combinations and Chokepoints under Quick Filters for Finding Class?


ar3diu
Forum|alt.badge.img+11
  • Author
  • Silver 2
  • Oct 27, 2025 3:55 PM UTC

Yes. 


kentphelps
Community Manager
Forum|alt.badge.img+12
  • Community Manager
  • Oct 27, 2025 8:03 PM UTC

The SOAR connector had not been updated to include the new classes.  I opened a ticket to get the product team to update the connector.  I am afraid I do not have a time frame for that.


kentphelps
Community Manager
Forum|alt.badge.img+12
  • Community Manager
  • Answer
  • Nov 13, 2025 1:33 PM UTC

​@ar3diu Take a look at Google SecOps Response Integrations release notes

Google Security Command Center: Version 14.0

  • Added the ability to ingest Toxic Combinations and Chokepoints in the following connector:

    • Google Security Command Center - Findings Connector

_K_O
Forum|alt.badge.img+13
  • Silver 2
  • Nov 13, 2025 4:29 PM UTC

With the update you should see all of the categories flowing into SecOps now. Here’s a basic query to show the different log types that are being ingested for SCC:
 

metadata.product_name = "Security Command Center"
match:
metadata.log_type
outcome:
$event_count = count(metadata.id)


YMMV:


ar3diu
Forum|alt.badge.img+11
  • Author
  • Silver 2
  • Nov 17, 2025 9:23 AM UTC

Thanks ​@kentphelps ! 🙌