
Solved

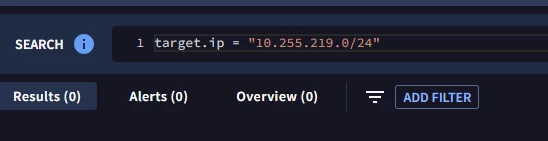
Searching for logs using subnet filter in UDM

  • Jan 2, 2026 6:56 PM UTC
  • 3 replies
  • 119 views

JoeBuilder1968
Forum|alt.badge.img

3 replies

cmorris
Staff
Forum|alt.badge.img+17
  • Staff
  • Answer
  • Jan 5, 2026 12:33 AM UTC

JoeBuilder1968
Forum|alt.badge.img

Here is the exact syntax I had to use.

net.ip_in_range_cidr($e.principal.ip, "192.0.2.0/24")

But I could not combine it using AND

I had to apply and run the search and then filter on other fields.


Does anyone know how I can combine in


cmorris
Staff
Forum|alt.badge.img+17
  • Staff
  • Jan 26, 2026 8:10 PM UTC

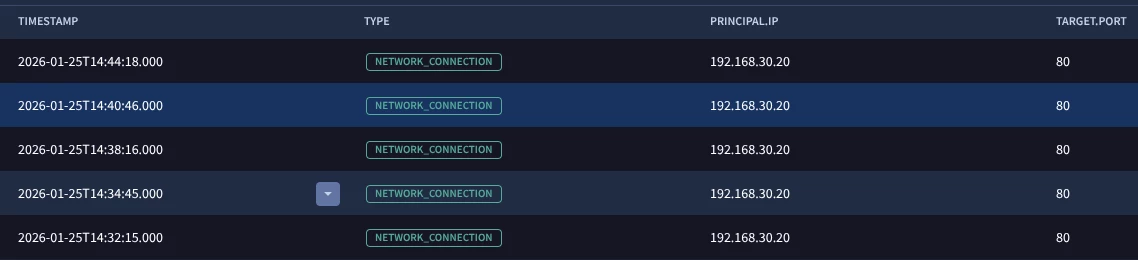
Can you try something like this? Please adjust event_type, port, and CIDR as needed.

metadata.event_type = "NETWORK_CONNECTION"
target.port = 80
net.ip_in_range_cidr(principal.ip, "192.168.0.0/16")

The query above works on my tenant and returns results here: