
Run faster searches in Google SecOps with Basic Mode in SIEM Search (now in Public Preview)
When you are hunting for threats, testing a query filter, or checking high-volume logs, you usually just want to see matching events and field counts right away without waiting for extra charts and background calculations to load.
The SIEM Search page now includes a mode selector (Basic Mode and Advanced Mode) in the query editor controls bar next to the query language selector, so you can choose between fast event retrieval and full visual enrichment.
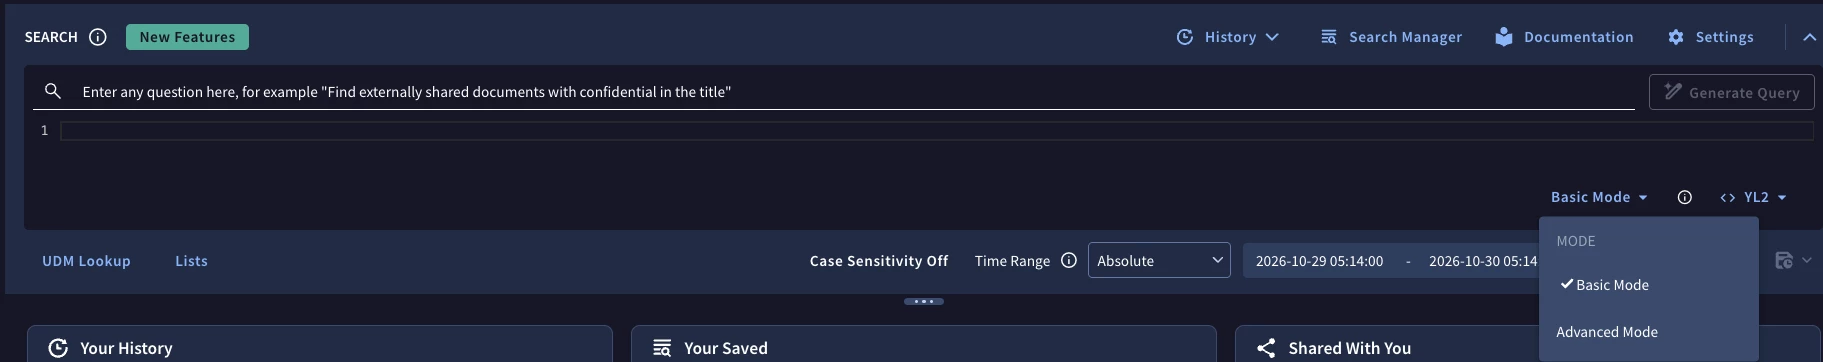
Figure 1: Selecting Basic Mode (default) or Advanced Mode in the SIEM Search query editor controls.
What is Basic Mode?
Basic Mode (now the default) focuses only on fetching your matching events and field aggregations. By skipping extra background lookups and chart data, Basic Mode reduces network payload size and speeds up UI rendering. Your search results transfer over the network faster and render more quickly in your browser—while keeping the exact same event data, query syntax (UDM, YARA-L 2.0, Reference Lists, and Data Tables), and Data RBAC permissions.
Advanced Mode gives you the full search experience with timeline charts, prevalence scores, entity context, and alert correlations.
Why Basic Mode is Faster
- Smaller Network Payloads & Faster Backend Execution:
- Skips prevalence lookups: Doesn't fetch historical indicator counts (domains, IP addresses, and file hashes) across your environment during the initial search.
- Skips alert correlation: Doesn't query the rules engine for matching YARA-L 2.0 alerts while pulling events.
- Skips timeline chart data: Streams matching events directly to your browser without generating or transferring bucketed timeline data, keeping the network payload lightweight.
- Faster UI Rendering & Cleaner Layout:
- Less browser rendering work: Hides the Alerts & Detections, Overview, and Visualize tabs—along with timeline charts (Activity Over Time and Trend Over Time), the Prevalence tab, and the Activity heatmap table—so the browser spends less time rendering heavy visual widgets and gives you more screen space for the Event Viewer.
- Events and Aggregations ready right away: Opens directly to the Results panel (with the Events view) and keeps the Aggregations panel active so you can check field counts and apply Show only or Filter out filters immediately.
- Built for Everyday Investigations:
- Easy mode switching: Start in Basic Mode to test queries and spot suspicious events quickly. Switch to Advanced Mode in the dropdown and rerun the query whenever you want timeline charts, heatmaps, Entity Context Graph (ECG) details, prevalence scores, or correlated alerts.
- Saves your preference: Remembers your selected mode (searchMode) in your browser across refreshes, tabs, and sessions.
- Shareable links: Adds the active mode (&searchMode=FAST for Basic Mode or &searchMode=ADVANCED for Advanced Mode) to the page URL, so links shared with teammates open in the same mode.
- Saved in Search History: The History dialog tracks which mode each search used and restores it when you rerun the query.
Quick Comparison: Basic Mode vs. Advanced Mode
The following table summarizes the differences between the two modes on the SIEM Search page:
| Feature | Basic Mode (Default) | Advanced Mode |
| Main goal | Fast event retrieval, smaller network payload, and quick UI rendering | Full visual analysis and background enrichment |
| Visible tabs | Results only | Results, Alerts & Detections, Overview, and Visualize |
| Field aggregations | Included (Aggregations panel active) | Included (Aggregations panel active) |
| Timeline charts & heatmaps | Hidden (reduces network payload and UI rendering time) | Displayed (the Activity Over Time chart, the Trend Over Time chart, and the Activity heatmap table) |
| Prevalence scoring | Skipped | Included |
| Correlated detections | Skipped | Included |
| Entity Context Graph (ECG) | Skipped | Included |
| Query syntax & Data RBAC | Same in both modes | Same in both modes |
| Network payload & UI speed | Smaller payload and faster browser rendering | Larger payload (transfers and renders full enrichment data) |
When to Use Each Mode
- Use Basic Mode for:
- Quick threat hunting: Check indicators across broad time ranges without waiting for timeline charts to transfer and render.
- High-volume log searches: Search noisy log sources with smaller network payloads and faster browser rendering.
- Building and tuning queries: Test UDM syntax, regular expressions, reference lists, and data table filters quickly before running a deeper investigation.
- Use Advanced Mode for:
- Building incident timelines: Use the Activity Over Time chart and Activity heat-map to spot spikes in activity.
- Checking indicator rarity: View enterprise prevalence scores to see whether an IP, domain, or file hash is common or unusual.
- Checking triggered alerts: See whether matching events triggered YARA-L 2.0 rules in the Alerts & Detections tab.
Have you tried Basic Mode in your threat hunting workflows yet? Share your feedback and use cases in the replies below!
