What’s New in Google SecOps for the interval Sep 28th through 4th Oct, 2026.
Product Updates & New Features
Google SecOps
🚀 Release Notes from Google Cloud Docs
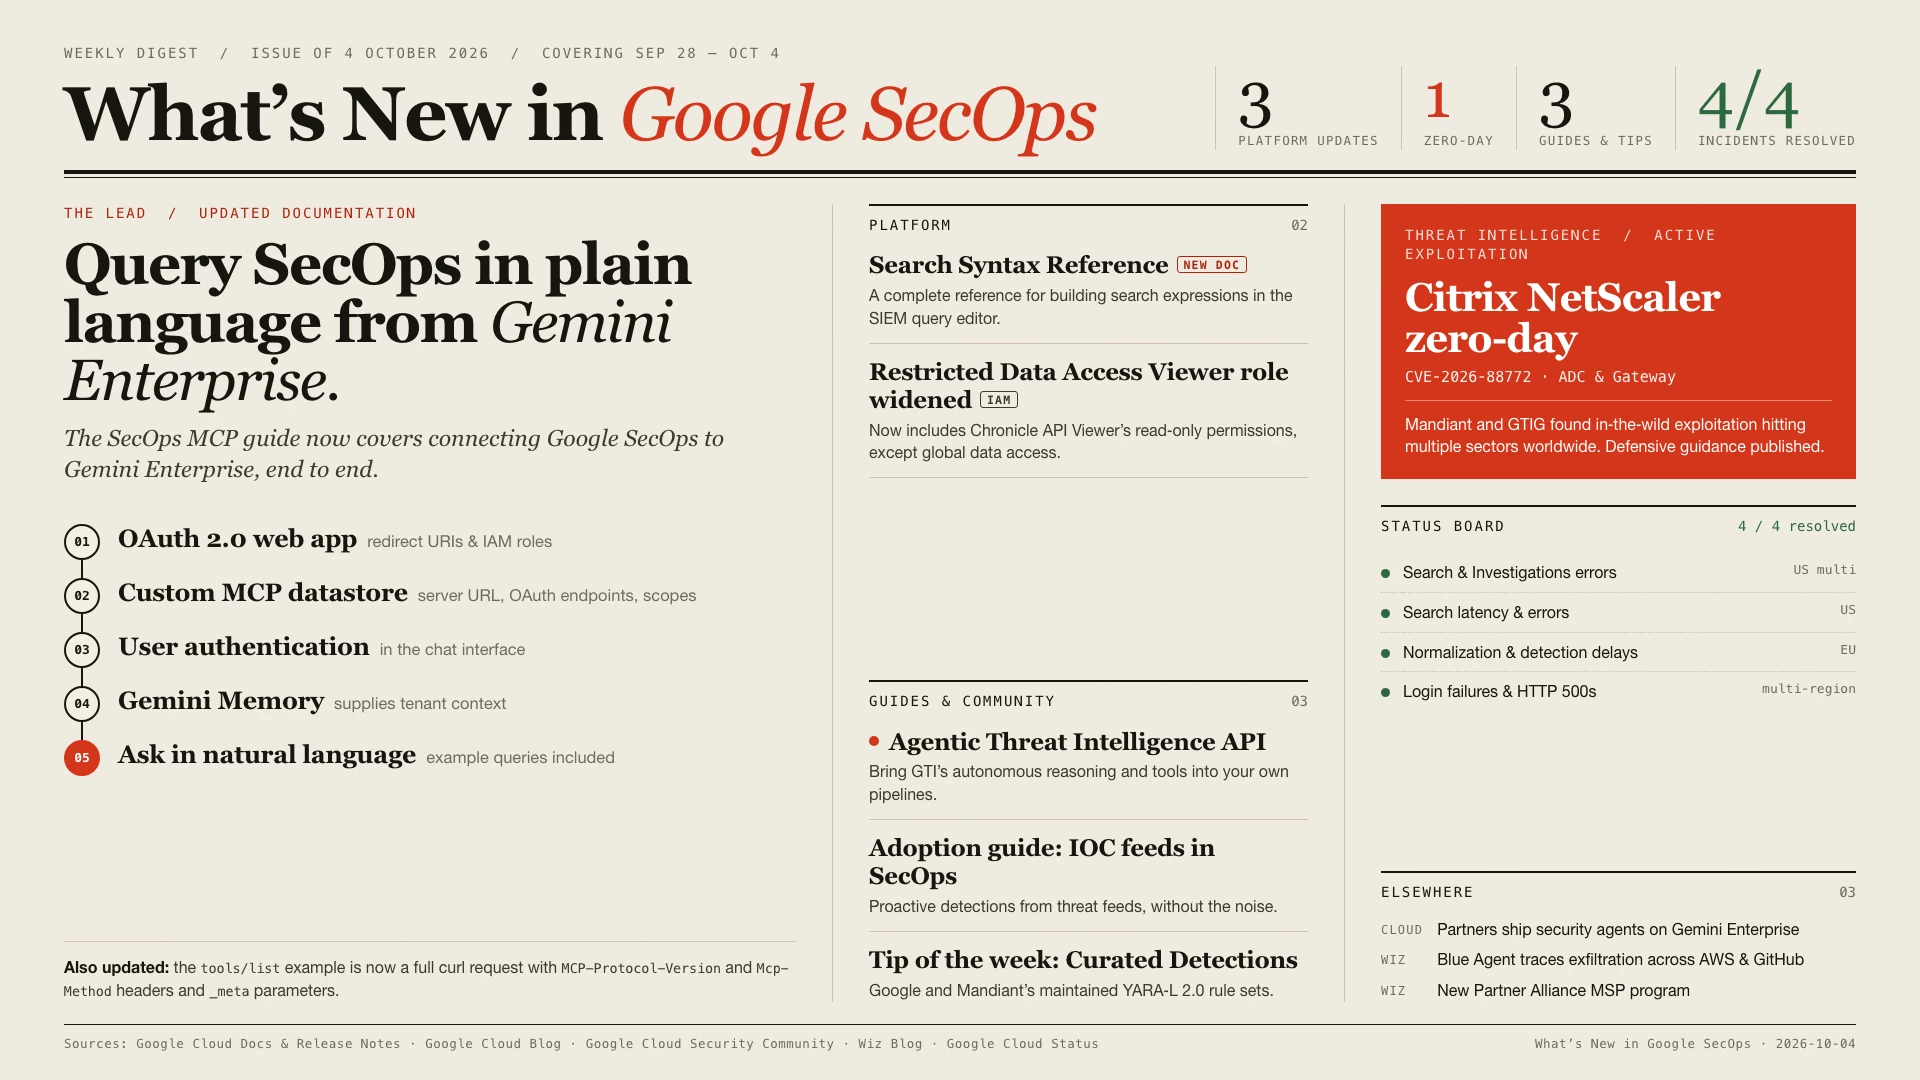
Google SecOps has updated the Chronicle API Restricted Data Access Viewer IAM role, expanding its read-only permissions to include those of the Chronicle API Viewer role, excluding global data access. Read More
📑 New Docs: Investigation > Search Syntax Reference from Google Cloud Docs
This document outlines the comprehensive search syntax for Google SecOps SIEM, guiding security analysts on configuring search expressions in the query editor. Read More
📝 Updated Docs: Use Google Secops MCP from Google Cloud Docs
This update introduces a comprehensive guide for integrating Google SecOps with Gemini Enterprise. The new section details the process, including:
-
Setting up an OAuth 2.0 Web Application in Google Cloud Console, specifying redirect URIs, and outlining required IAM roles.
-
Configuring a Custom MCP datastore within Gemini Enterprise, providing steps for entering MCP server URL, OAuth details (Authorization URL, Token URL, Client ID/Secret), and OAuth Scopes.
-
User authentication for the connector within the chat interface.
-
Setting up Gemini Memory to provide necessary tenant context for queries.
-
Examples for querying Google SecOps using natural language within Gemini Enterprise.
Additionally, the documentation significantly updates the example for listing MCP tools (tools/list method), replacing the basic HTTP POST with a detailed curl command that includes specific headers (MCP-Protocol-Version, Mcp-Method) and an expanded JSON request body with _meta parameters for protocol version and client capabilities. New placeholders for TOOLSET_ENDPOINT and MCP_PROTOCOL_VERSION are also introduced. Read More
Google Threat Intelligence
✍️ Defending Against Active Exploitation of Citrix NetScaler ADC and Gateway Appliances from Google Cloud Blog
Mandiant Consulting and Google Threat Intelligence Group identified active, in-the-wild exploitation of a zero-day vulnerability (CVE-2026–88772) affecting Citrix NetScaler ADC and Gateway appliances, impacting various sectors globally. The article discusses defending against this critical exploitation. Read More
Google Cloud
✍️ Google Cloud partners deliver new security agents and AI defenses with Gemini Enterprise from Google Cloud Blog
Google Cloud partners are integrating new security agents and AI defenses, powered by Gemini Enterprise, to help businesses combat AI-accelerated cyberattacks across all enterprise layers. Read More
Adoption Guides & Deep Dives
🔥 ✍️ Agentic Threat Intelligence, now in your own pipelines: a practical guide to the API from Google Cloud Security Community
The article introduces the Agentic Threat Intelligence API, allowing security analysts to integrate Google Threat Intelligence’s autonomous reasoning and tools directly into their existing security pipelines and automated workflows. This new API aims to move threat intelligence beyond browser-based investigations into core operational tools. Read More
Community & Events
✍️ Tuesday’s Tips of the Week — Curated Detections from Google Cloud Security Community
Google and Mandiant offer “Curated Detections,” which are YARA-L 2.0 rule sets providing vendor-maintained coverage against known threat techniques for UDM-normalized telemetry. Read More
✍️ Leveraging IOC Feeds in SecOps from Google Cloud Security Community
Google Cloud Security has released a new “Adoption Guide: Leveraging IOC Feeds in SecOps” to help security teams use threat intelligence feeds for proactive detections effectively, reducing unmanageable noise. Read More
Wiz
✍️ The Blue Agent POV: Investigating Multi-Platform Data Exfiltration Across AWS and GitHub from Wiz Blog
The article details a ‘Blue Agent’ investigation into a multi-platform data exfiltration attack spanning AWS and GitHub, uncovering compromised credentials, stolen source code, and custom exfiltration tools. Read More
✍️ Introducing the Wiz Partner Alliance Managed Service Provider Program from Wiz Blog
Wiz is launching a new Managed Service Provider (MSP) program within its Partner Alliance to empower partners in delivering world-class cloud and AI security solutions at scale. Read More
Platform Issues
✅ RESOLVED: We are experiencing elevated error rates and latency affecting Chronicle Search & Investigations in the US Multiregion from Google Cloud Status
Google Cloud is experiencing elevated error rates and latency affecting Chronicle Search & Investigations and Chronicle Search & Rules in the US Multiregion. Read More
✅ RESOLVED: Some Google SecOps customers may experience increased search latencies and intermittent error rates in the US region from Google Cloud Status
Google SecOps customers in the US region are experiencing increased search latencies and intermittent error rates due to an ongoing issue. Read More
✅ RESOLVED: Some Google SecOps customers in EU may experience delays with data normalization and detections from Google Cloud Status
Google SecOps customers in the EU are experiencing an ongoing incident causing delays with data normalization and detections, which began on 2026–09–29 05:26 PDT. Read More
✅ RESOLVED: Google SecOps is experiencing intermittent login failures and HTTP 500 errors in multiple regions, including us-east1, us-central1, and europe-west1 from Google Cloud Status
Google SecOps is experiencing intermittent login failures and HTTP 500 errors in multiple regions, including us-east1, us-central1, and europe-west1, impacting customer access to the platform. Read More
